In short
A few lines in your HTTP response can tell the browser to refuse fake frames, block injected scripts and never use plain HTTP again. Free protection, if you send them.
Response headers like Strict-Transport-Security, X-Content-Type-Options and Content-Security-Policy that instruct browsers to enforce additional protections for your app.
Think of it like this
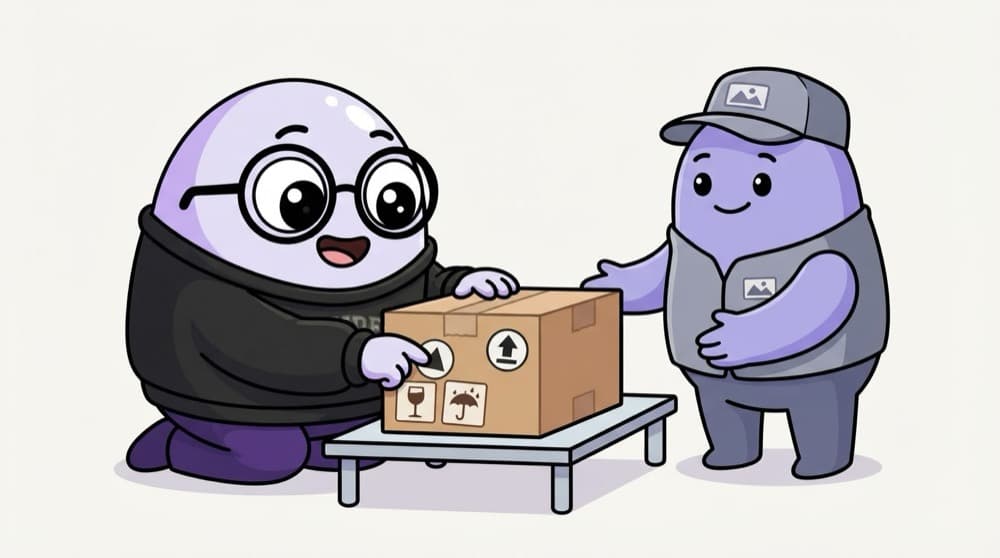
Stickers on a courier parcel
'This side up', 'Fragile', 'Keep dry'. The sender doesn't ride along; the stickers tell every handler how to treat the box. Security headers are stickers on your responses, and the browser is a very obedient handler.
Watch it happen
Headers the browser obeys
GET /dashboard
1/5The browser asks for your dashboard over HTTPS.
The big ideas
What you need to know
HSTS
Strict-Transport-Security forces HTTPS on future visits, so nobody can downgrade a user to plain HTTP.
CSP
Content-Security-Policy is an allowlist of script, style and image sources. It's the strongest XSS backup you have.
nosniff
X-Content-Type-Options: nosniff stops browsers guessing file types, so an uploaded .txt isn't run as a script.
Referrer and permissions
Referrer-Policy limits what URLs leak to other sites. Permissions-Policy turns off camera, mic and more if you don't use them.
See it in code
Walk through the code
1HTTP/1.1 200 OK2Strict-Transport-Security: max-age=31536000; includeSubDomains3Content-Security-Policy: default-src 'self'; frame-ancestors 'none'4X-Content-Type-Options: nosniff5Referrer-Policy: strict-origin-when-cross-origin6Permissions-Policy: camera=(), microphone=()1/3max-age is in seconds, so 31536000 is one year of HTTPS only, for subdomains too.
Helmet sets most of these in Express. Nginx or your host can add them too. Check any site's headers with curl -I.
Save yourself the pain
Common mistakes
Oops
Turning on HSTS with includeSubDomains before every subdomain supports HTTPS.
Do this instead
Start with a small max-age, confirm everything works on HTTPS, then raise it.
Oops
Writing a CSP with 'unsafe-inline' and 'unsafe-eval' to stop errors.
Do this instead
Those undo most of the protection. Move inline scripts into files or use nonces.
Your mission
Grade a few real sites
Quick check
Which header stops other sites from loading your page inside an iframe?
Go deeper
- 1Scan a deployed API/site with a header-checking tool, e.g. securityheaders.com.
- 2Add any missing recommended headers via Helmet or manual configuration.
- 3Learn what each header specifically prevents.
More topics at this stop
 OWASP Top 10
 SQL Injection
 XSS Prevention
 CSRF Protection
 Helmet.js
 CORS Configuration
 Input Validation & Sanitization
 Rate Limiting
 Environment Variables & Secrets
 Data Encryption
 Dependency Vulnerability Scanning

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
