
Password Hashing (bcrypt)
Part of the Backend Developer Roadmap
In short
Databases get leaked. When yours does, plain-text passwords hand attackers your users' other accounts too, since people reuse passwords. bcrypt makes every stolen password slow and painful to crack.
Never store passwords in plain text — bcrypt is a slow, salted hashing algorithm specifically designed to make brute-forcing stolen password hashes impractical.
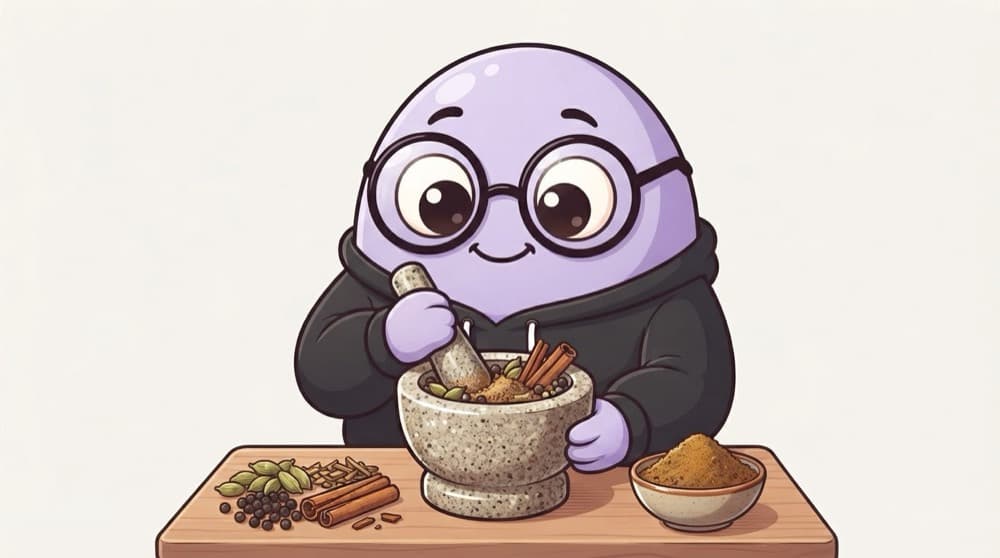
Think of it like this
Grinding masala
Once whole spices become garam masala, you can't turn the powder back into cardamom and cloves. Grind the same mix again and you get the same powder. Hashing is one-way like that. bcrypt also adds a unique pinch, the salt, and grinds slowly on purpose.
Watch it happen
From password to stored hash
1/5A user signs up with the password chai@123.
The big ideas
What you need to know
Hash, never encrypt
Encryption can be reversed with the key. Passwords should be hashed one-way, so even you can't read them.
Salt kills lookup tables
A random salt per password makes precomputed tables of common password hashes useless.
Slow is the point
Fast hashes like SHA-256 let attackers try billions of guesses per second. bcrypt's cost factor slows every guess.
Argon2id is the newer pick
OWASP now prefers Argon2id. bcrypt with a cost of 10 or more is still acceptable, especially in existing systems.
See it in code
Walk through the code
1import bcrypt from "bcrypt";2 3const COST = 12;4 5export async function hashPassword(plain: string) {6 return bcrypt.hash(plain, COST);7}8 9export async function checkPassword(plain: string, stored: string) {10 return bcrypt.compare(plain, stored);11}12 13// stored looks like: $2b$12$<22-char salt><31-char hash>1/4The cost factor. Each +1 doubles the work. 12 is a common choice today.
bcrypt only uses the first 72 bytes of a password, so very long passphrases get cut off. Argon2id, via the argon2 package, avoids that.
Save yourself the pain
Common mistakes
Oops
Hashing passwords with plain SHA-256 or MD5.
Do this instead
Those are built to be fast, which helps attackers. Use bcrypt or Argon2id, which are slow on purpose.
Oops
Hashing the login attempt yourself and comparing strings with ===.
Do this instead
Use bcrypt.compare. It re-hashes with the stored salt and cost and compares safely.
Your mission
Feel the cost factor
Quick check
Two users both pick the password 'hello123'. With bcrypt, their stored hashes are...
Go deeper
- 1Hash a password with bcrypt and verify a login attempt against the stored hash.
- 2Learn why bcrypt is deliberately slow, unlike a fast hash like SHA-256.
- 3Understand salting and why it prevents rainbow-table attacks.
More topics at this stop
 Sessions
 JWT
 OAuth 2.0
 Passport.js
 Role-Based Access Control (RBAC)
 Refresh Tokens
 Social Login (Google/GitHub)
 API Keys
 Multi-Factor Authentication
 Single Sign-On (SSO)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
