In short
When another company's server calls your API at 3 a.m., there's no human to type a password. An API key is a long secret that tells you which client is calling.
A simpler authentication mechanism for server-to-server or third-party integrations — a static secret string sent with each request, without the complexity of OAuth or sessions.
Think of it like this
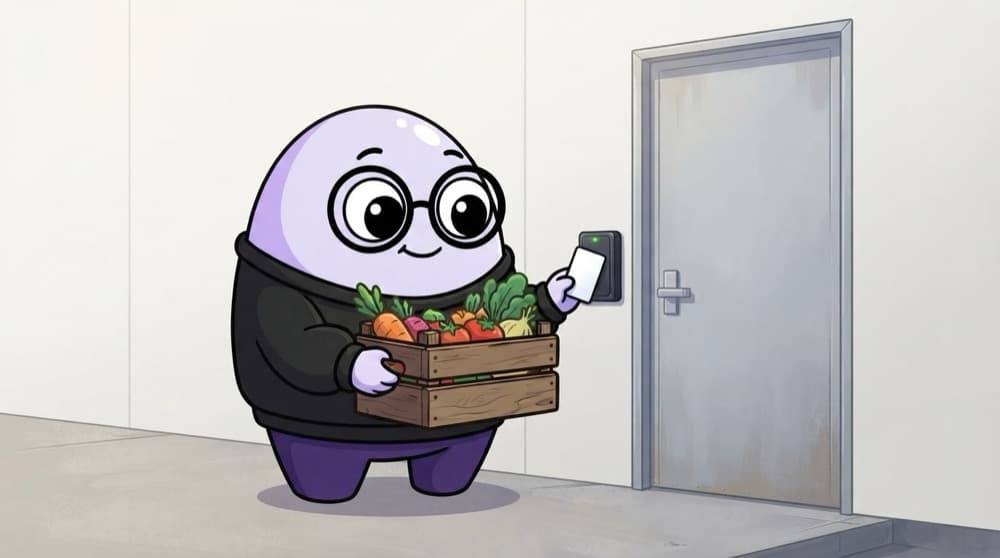
The supplier's access card
The vegetable supplier doesn't ring the watchman every morning. He has his own access card for the service door. If he stops supplying, security switches off just his card. An API key is that card: one per client, quick to check, easy to cancel.
Watch it happen
A partner server calls your API
x-api-key: key_9f…
1/5The partner's server sends its key in a header on every request.
The big ideas
What you need to know
Identifies a client
API keys say which app or company is calling. They're for servers and scripts, not end-user logins.
Show once, store a hash
Display the full key only at creation. Store its hash, plus a short prefix to help people find it.
Scope and limit each key
Give each key only the permissions it needs, and its own rate limit.
Rotate without downtime
Let a client hold two keys at once, so they can switch to the new one before you revoke the old.
See it in code
Walk through the code
1import crypto from "node:crypto";2 3export function createApiKey() {4 const key = "key_" + crypto.randomBytes(24).toString("base64url");5 const hash = crypto.createHash("sha256").update(key).digest("hex");6 return { key, hash, prefix: key.slice(0, 10) };7}8 9export async function apiKeyAuth(req: Request, res: Response, next: NextFunction) {10 const key = req.header("x-api-key");11 if (!key) return res.status(401).json({ error: { code: "MISSING_API_KEY" } });12 const hash = crypto.createHash("sha256").update(key).digest("hex");13 const client = await db.apiKeys.findActiveByHash(hash);14 if (!client) return res.status(401).json({ error: { code: "INVALID_API_KEY" } });15 req.client = client; next();16}1/4Make a long random key with a readable prefix. Show the key once; save only the hash and prefix.
Unlike passwords, API keys are long and random, so a fast hash is fine. req.client needs a small type extension in TypeScript.
Save yourself the pain
Common mistakes
Oops
Putting an API key in frontend JavaScript or a mobile app.
Do this instead
Anyone can pull it out of the bundle. Keys belong on servers; users should log in with sessions or OAuth.
Oops
Passing keys in the URL, like ?api_key=…
Do this instead
URLs end up in logs and browser history. Send keys in a header, over HTTPS.
Your mission
Issue and revoke a key
Quick check
Why is a fast hash like SHA-256 fine for API keys but not for passwords?
Go deeper
- 1Implement API key authentication for a public API endpoint.
- 2Learn to hash/store API keys the way you'd store passwords, not in plain text.
- 3Design a way for users to generate, view once, and revoke their own API keys.
More topics at this stop
 Sessions
 JWT
 OAuth 2.0
 Passport.js
 Password Hashing (bcrypt)
 Role-Based Access Control (RBAC)
 Refresh Tokens
 Social Login (Google/GitHub)
 Multi-Factor Authentication
 Single Sign-On (SSO)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
