DevSecOps Practices
Part of the Cybersecurity Roadmap
In short
DevSecOps weaves security into the automated pipeline that builds and ships software. Instead of a slow gate at the end, security checks run on every change, automatically.
Integrating security tooling (SAST, SCA, secrets scanning) directly into CI/CD pipelines so security checks run automatically on every code change, rather than as a separate, disconnected process.
Think of it like this
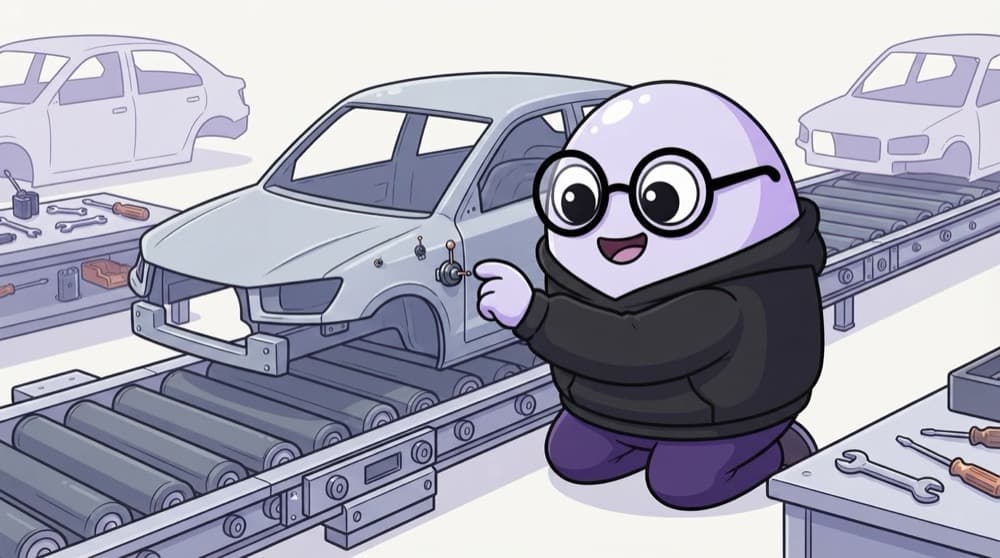
Quality checks on the assembly line
A modern car plant does not inspect only the finished car. Sensors check each part as it moves down the line, stopping a fault early. DevSecOps adds those security checkpoints to the software assembly line, so problems get caught as code flows through.
Watch it happen
Security inside the pipeline
1/5A developer pushes code, triggering the automated pipeline.
The big ideas
What you need to know
Automate the checks
Security tools run on every commit inside CI, so safety does not depend on someone remembering to check.
Shift left, stay fast
Checks run early and quickly. The aim is to add safety without turning delivery into a crawl.
Fail fast on serious issues
A high severity finding can stop the build, so a known vulnerability never quietly ships to users.
Shared ownership
Dev, security and ops share the pipeline and the responsibility. Security is part of delivery, not a separate team's chore.
Save yourself the pain
Common mistakes
Oops
Bolting on a slow manual security gate at the very end.
Do this instead
Automate checks throughout the pipeline. A late manual gate becomes a bottleneck people learn to bypass.
Oops
Making every low finding fail the build.
Do this instead
Tune thresholds so only serious issues block. Too much noise trains developers to ignore the pipeline entirely.
Your mission
Add three checks to a pipeline
Quick check
What is the core idea of DevSecOps?
Go deeper
- 1Add a security scanning step (SAST or SCA) to a sample CI pipeline.
- 2Learn why automated security gates in a pipeline scale far better than manual security reviews alone.
- 3Understand DevSecOps as the practical implementation of 'shift left' from earlier in this phase.
More topics at this stop
 Secure SDLC ('Shift Left')
 Threat Modeling
 Static Application Security Testing (SAST)
 Dynamic Application Security Testing (DAST)
 Software Composition Analysis (SCA)
 API Security
 Secure Code Review
 Security Champions Programs

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
