Secure SDLC ('Shift Left')
Part of the Cybersecurity Roadmap
In short
Finding a security bug the day before launch is painful and expensive. Shifting left means catching it while you code, when a fix is cheap and nobody is panicking.
Integrating security checks earlier in the development lifecycle (during coding and CI, not just before release) — 'shifting left' catches vulnerabilities when they're cheap to fix, not after deployment.
Think of it like this
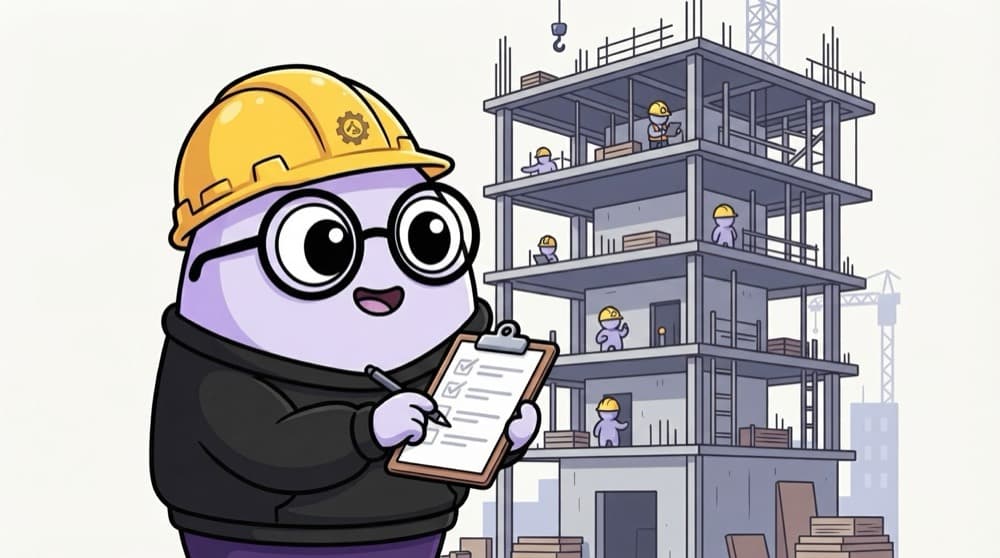
Checking the building as it rises
A wise site engineer checks the foundation and each floor as it is built, not after the whole tower is up. Fixing a crack early is simple; fixing it under a finished building is a disaster. Secure development checks security at every stage.
Watch it happen
Security at every stage
1/5Think about threats while designing. A flaw in the plan is cheapest to fix now.
The big ideas
What you need to know
Earlier is cheaper
A bug caught at design costs a fraction of one found in production. Shifting left saves time and money.
Security at every step
Do not leave it to one final gate. Bake checks into design, coding, building and testing.
Everyone owns it
Security is not only the security team's job. Developers, testers and ops all share it in a secure SDLC.
Fast feedback
Quick, automated checks in the pipeline teach developers as they work, so the next bug never ships.
Save yourself the pain
Common mistakes
Oops
Leaving all security to one test right before launch.
Do this instead
Late bugs are costly and rushed. Spread checks across design, coding and building so issues surface early.
Oops
Treating security as the security team's problem alone.
Do this instead
In a secure SDLC, developers and ops share ownership. Shared responsibility catches far more than one gate.
Your mission
Add one early check
Quick check
What does 'shift left' mean in a secure development lifecycle?
Go deeper
- 1Diagram a traditional 'security review at the end' process versus a shift-left approach.
- 2Learn why fixing a vulnerability in code review is far cheaper than fixing it in production.
- 3Identify one security check that could be added directly into a CI pipeline.
More topics at this stop
 Threat Modeling
 Static Application Security Testing (SAST)
 Dynamic Application Security Testing (DAST)
 Software Composition Analysis (SCA)
 API Security
 Secure Code Review
 Security Champions Programs
 DevSecOps Practices

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
