Secure Code Review
Part of the Cybersecurity Roadmap
In short
Tools catch patterns, but a human spots the subtle logic flaw a scanner misses. Secure code review is reading code with an attacker's mindset before it ships.
Manually reviewing code with a security lens — looking specifically for input validation gaps, authorization checks, and unsafe function usage, complementing automated SAST scanning.
Think of it like this
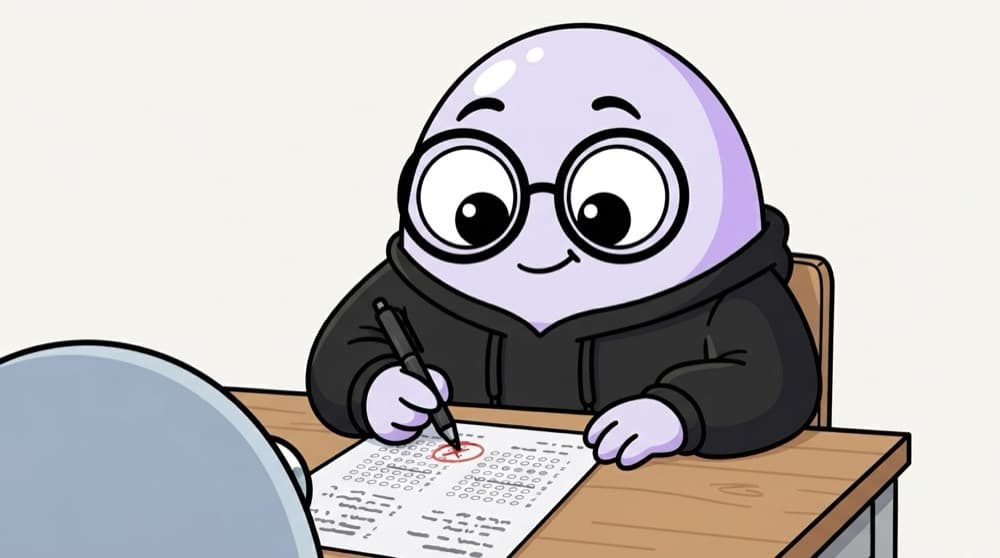
The second pair of eyes on an exam answer
You reread your own exam answer and it looks fine, because you know what you meant. A friend reads it fresh and instantly spots the gap in your logic. Secure code review is that fresh pair of eyes, hunting for security holes in particular.
Watch it happen
What a reviewer looks for
1/4Is every user input validated and used safely, with no unescaped queries or commands?
The big ideas
What you need to know
Think like an attacker
Ask 'how could this input break things?' at each spot where data enters or a decision is made.
Focus on the hotspots
Input handling, authentication, authorisation and anything touching money or secrets deserve the closest look.
Use a checklist
A short, shared checklist keeps reviews consistent and stops the reviewer forgetting a common class of bug.
Humans plus tools
SAST finds patterns fast; a reviewer understands intent and logic. Together they catch far more than either alone.
Save yourself the pain
Common mistakes
Oops
Approving a pull request after a quick skim.
Do this instead
Security review needs focus on risky spots. A rubber stamp lets logic flaws that tools miss slip into production.
Oops
Thinking a passing SAST scan means the code is safe.
Do this instead
Scanners miss logic and authorisation flaws. A human reviewer who understands intent catches what patterns cannot.
Your mission
Review a risky snippet
Quick check
Why keep human code review even when SAST tools run automatically?
Go deeper
- 1Review a sample code snippet specifically for missing input validation or authorization checks.
- 2Learn to build a personal checklist of common security anti-patterns to watch for during review.
- 3Practice explaining a security finding to a developer constructively, not just flagging it.
More topics at this stop
 Secure SDLC ('Shift Left')
 Threat Modeling
 Static Application Security Testing (SAST)
 Dynamic Application Security Testing (DAST)
 Software Composition Analysis (SCA)
 API Security
 Security Champions Programs
 DevSecOps Practices

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
