
Server-Side Request Forgery (SSRF)
Part of the Cybersecurity Roadmap
In short
Features like "import image from URL" make your server fetch addresses a user chooses. Without limits, that server can be steered to internal systems the user could never reach directly.
Tricking a server into making unintended requests to internal or external systems on the attacker's behalf — often used to reach internal services not otherwise exposed to the internet.
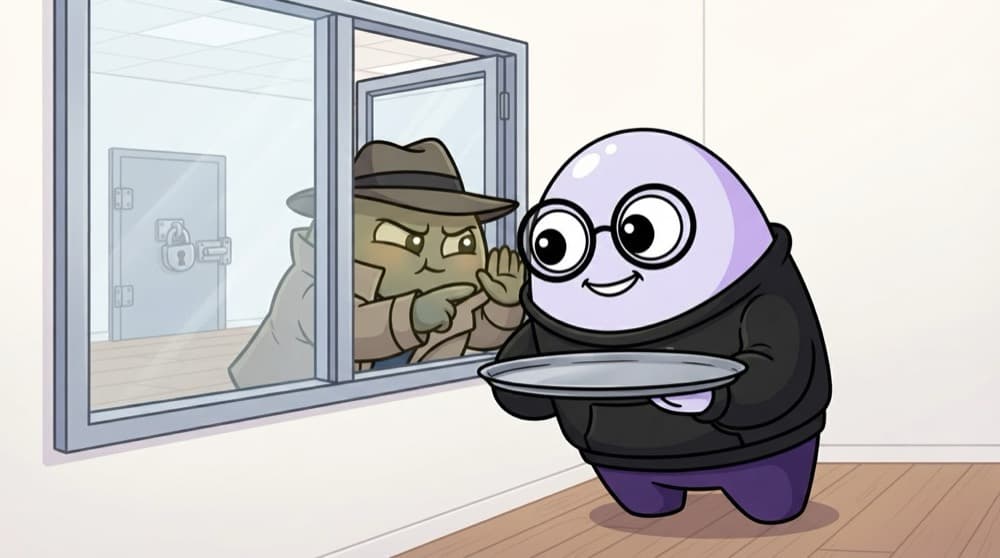
Think of it like this
The waiter who fetches anything
A restaurant waiter brings whatever a customer asks for. A sly customer asks him to fetch the cash box from the manager's back office. Staff can walk into rooms customers can't. A good waiter only goes to the kitchen counter, nowhere else.
Watch it happen
An allowlist stops a bad fetch
POST /import?url=…
1/6A user asks your API to download an image from a URL.
The big ideas
What you need to know
Allowlist, not blocklist
List the few hosts you need. Blocklists of "bad" addresses miss alternate spellings and redirects.
Network rules too
Firewall rules can stop app servers reaching internal admin panels or cloud metadata. Code checks plus network rules is defence in depth.
Protect cloud metadata
Cloud servers have an internal metadata service. On AWS, require IMDSv2 so simple forged fetches get less.
Watch redirects
An allowed URL can redirect elsewhere. Turn off automatic redirects or check every hop.
See it in code
Walk through the code
1const ALLOWED_HOSTS = new Set(["images.example-cdn.com", "api.partner.in"]);2 3async function safeFetch(input: string) {4 const url = new URL(input);5 if (url.protocol !== "https:") throw new Error("HTTPS only");6 if (!ALLOWED_HOSTS.has(url.hostname)) throw new Error("Host not allowed");7 return fetch(url, { redirect: "error", signal: AbortSignal.timeout(5000) });8}1/3Only these hosts may ever be fetched. Everything else is refused by default.
new URL parses the address properly, so you compare the real hostname instead of guessing with string checks.
Save yourself the pain
Common mistakes
Oops
Checking if the URL string "contains" your CDN's name.
Do this instead
Parse with new URL and compare url.hostname exactly. Substring checks are easy to fool.
Oops
Returning the fetched response body or error details straight to the user.
Do this instead
Return only what the feature needs, like a resized image, and generic errors.
Your mission
Guard a URL import feature
Quick check
Which check best defends a "fetch from URL" feature against SSRF?
Go deeper
- 1Learn how SSRF can be used to reach internal cloud metadata endpoints (a common real attack pattern).
- 2Practice identifying an SSRF vulnerability in a legal practice lab.
- 3Understand why validating and restricting outbound requests is the core defense.
More topics at this stop
 OWASP Top 10 Overview
 SQL Injection
 Cross-Site Scripting (XSS)
 Cross-Site Request Forgery (CSRF)
 Broken Authentication
 Security Misconfiguration
 Insecure Deserialization
 Broken Access Control
 Vulnerable & Outdated Components
 Common Web App Attack Techniques

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
