Security Misconfiguration
Part of the Cybersecurity Roadmap
In short
No clever code bug needed: a debug page left on, a default admin password, a storage bucket set to public. Misconfiguration is the security hole you create by forgetting.
Insecure default settings, unnecessary features left enabled, or overly verbose error messages — one of the most common vulnerability categories, since it results from omission rather than a coding flaw.
Think of it like this
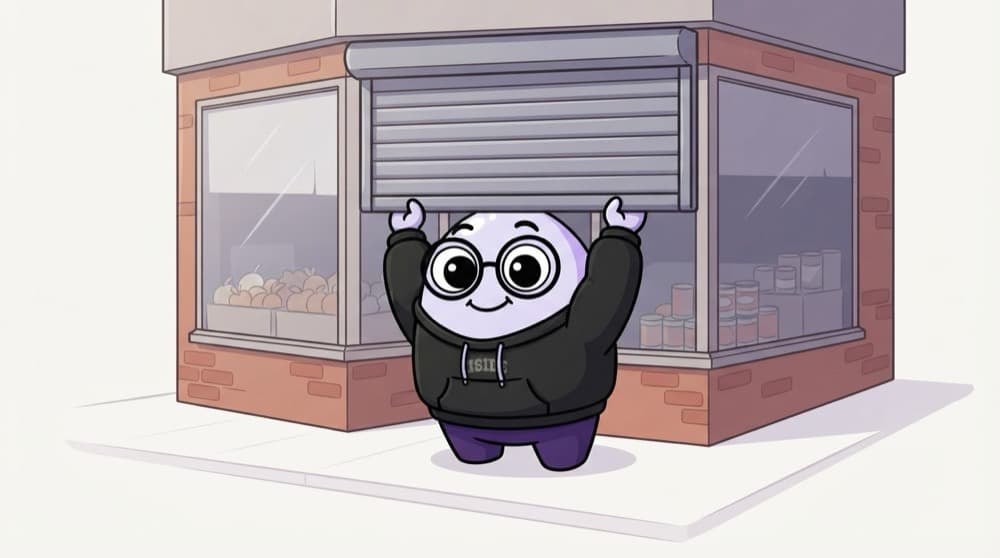
The shutter left half open
A kirana owner locks the cash box, installs a camera, then goes home with the shop shutter half up. All the good locks don't matter now. Misconfiguration is that half-open shutter: the protection exists, but a setting left it open.
Watch it happen
Fresh install vs hardened setup
Default install
- Debug mode and stack traces on
- Default admin account still active
- Directory listing and sample pages enabled
Hardened
- Generic errors, details only in logs
- Defaults removed, unique strong credentials
- Only needed features, ports and headers
Defaults are made for easy setup, not safety. Harden every environment the same way, ideally from one reviewed config file.
The big ideas
What you need to know
Defaults are for demos
Default passwords, sample apps and open admin panels are documented publicly. Change or remove them before going live.
Errors say too much
Stack traces reveal file paths, library versions and queries. Show users a short message and log the details.
Cloud storage settings
Many leaks are just storage buckets set to public. Block public access by default and review permissions.
Same config everywhere
Keep settings in code (Docker, Terraform, config files) so staging and production can't quietly drift apart.
See it in code
Walk through the code
1import express from "express";2import helmet from "helmet";3 4const app = express();5app.disable("x-powered-by");6app.use(helmet());7 8// Generic errors for users, full details only in server logs9app.use((err, req, res, next) => {10 console.error(err);11 res.status(500).json({ error: "Something went wrong" });12});1/3Stops Express announcing itself in every response header, giving outsiders one less clue.
Also run with NODE_ENV=production, which makes Express skip stack traces in its default error pages.
Save yourself the pain
Common mistakes
Oops
Leaving phpMyAdmin, /admin or a test route reachable on the public server.
Do this instead
Remove tools you don't need in production, or put them behind VPN and strong authentication.
Oops
Hardening production by hand once, then forgetting what changed.
Do this instead
Write the hardening into config files or scripts so every new server starts secure.
Your mission
Audit your own app's settings
Quick check
Your production API returns full stack traces on errors. Which category is this?
Go deeper
- 1Audit a practice application's configuration for unnecessary exposed features or verbose errors.
- 2Learn why default credentials and default configs are a recurring, preventable real-world issue.
- 3Understand why security misconfiguration often results from rushed deployment, not malicious intent.
More topics at this stop
 OWASP Top 10 Overview
 SQL Injection
 Cross-Site Scripting (XSS)
 Cross-Site Request Forgery (CSRF)
 Broken Authentication
 Insecure Deserialization
 Server-Side Request Forgery (SSRF)
 Broken Access Control
 Vulnerable & Outdated Components
 Common Web App Attack Techniques

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
