
Common Web App Attack Techniques
Part of the Cybersecurity Roadmap
In short
Path traversal, command injection, risky file uploads, open redirects: different names, same root cause. Untrusted input ends up somewhere it can change what your server does.
Beyond the specific OWASP categories — techniques like directory traversal, command injection, and file upload abuse recur across many vulnerability types and are worth recognizing as patterns.
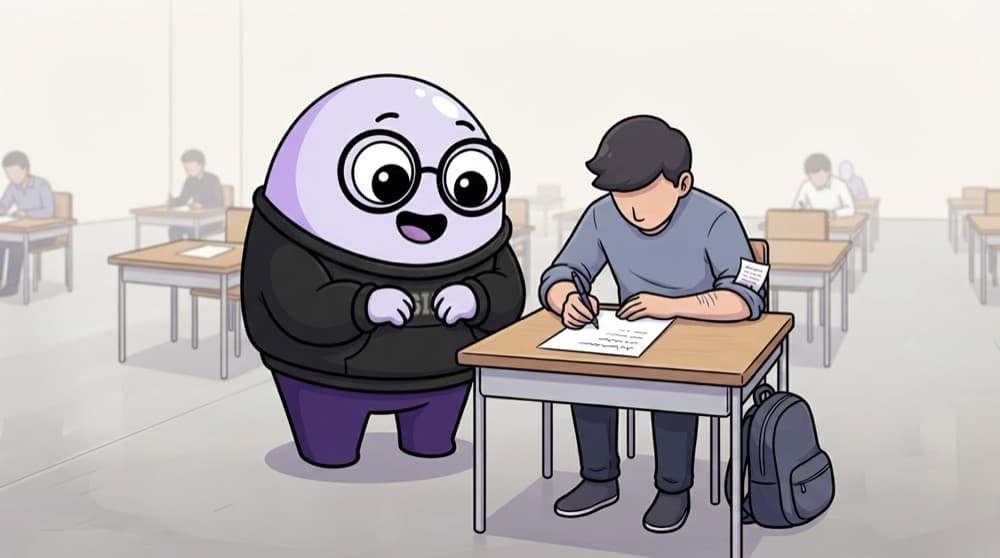
Think of it like this
The invigilator who knows the tricks
An experienced exam invigilator doesn't need to know every student. She knows the usual tricks: notes in sleeves, swapped answer sheets, phones under the desk. Learn the common patterns, and you spot new cases quickly.
Watch it happen
Where untrusted input lands, and the fix
1/5Anything from a request is untrusted: URL, body, headers, cookies and file names.
The big ideas
What you need to know
Validate by allowlist
Describe what good input looks like, like letters, digits and a .png ending, and reject everything else.
Avoid the shell
Shell features are powerful and easy to misuse. Use execFile or a library so input stays a plain argument.
Least privilege
Run the app as a limited user that can only read and write its own folders. Mistakes then do less harm.
Test in a lab
Practise spotting these patterns in deliberately vulnerable apps like DVWA, never on sites you don't own.
See it in code
Walk through the code
1import path from "node:path";2import { execFile } from "node:child_process";3 4const UPLOADS = path.resolve("uploads");5 6// File paths: resolve, then confirm it stays inside the folder7const filePath = path.resolve(UPLOADS, req.params.name);8if (!filePath.startsWith(UPLOADS + path.sep)) return res.sendStatus(400);9res.sendFile(filePath);10 11// Commands: no shell, arguments passed as a list12execFile("convert", [filePath, "-resize", "200x200", outPath], onDone);1/3The one folder files may be served from, as an absolute path.
Both fixes follow one idea: keep user input as data in a fixed slot, never as part of a path or command you build by hand.
Save yourself the pain
Common mistakes
Oops
Trusting the file's extension or the browser's Content-Type for uploads.
Do this instead
Check the actual file content, limit size, rename it and serve it from a separate domain or storage bucket.
Oops
Using exec with a template string because it's quicker to write.
Do this instead
Use execFile or spawn with an argument array, or a library that does the job without a shell.
Your mission
Spot the pattern in a training lab
Quick check
What do path traversal, command injection and open redirects have in common?
Go deeper
- 1Practice identifying a directory traversal vulnerability in a legal practice lab.
- 2Learn the general pattern: unvalidated user input reaching a sensitive operation (file access, command execution).
- 3Build a personal mental checklist of 'what could this input actually do' when reviewing any app.
More topics at this stop
 OWASP Top 10 Overview
 SQL Injection
 Cross-Site Scripting (XSS)
 Cross-Site Request Forgery (CSRF)
 Broken Authentication
 Security Misconfiguration
 Insecure Deserialization
 Server-Side Request Forgery (SSRF)
 Broken Access Control
 Vulnerable & Outdated Components

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
