
Intrusion Detection & Prevention Systems (IDS/IPS)
Part of the Cybersecurity Roadmap
In short
An IDS watches your network traffic and shouts when something looks like an attack. An IPS goes further and blocks it on the spot. Same brain, different power.
An IDS monitors traffic and alerts on suspicious patterns; an IPS actively blocks it — both rely on signature-based detection (known attack patterns) and/or anomaly-based detection (deviation from normal).
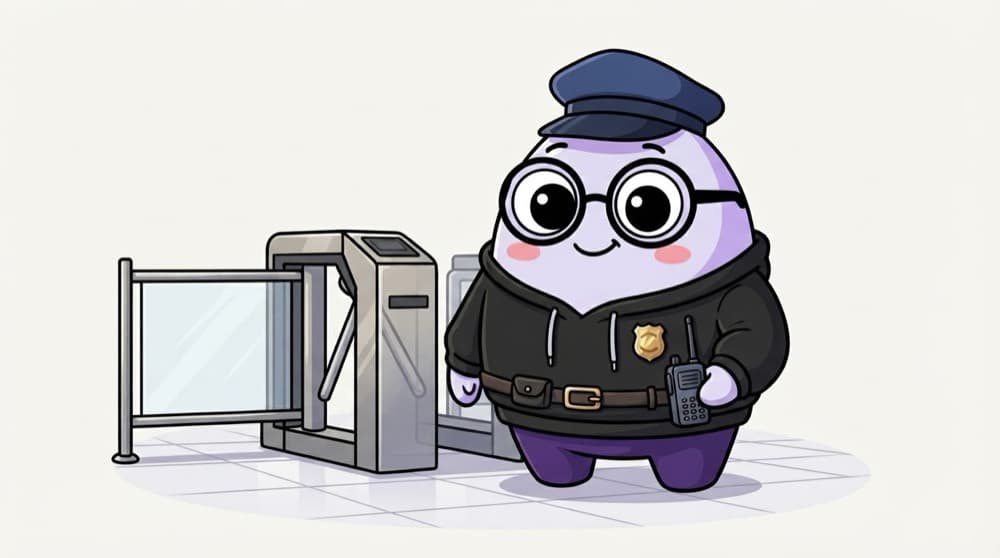
Think of it like this
Watchman versus turnstile
An IDS is a watchman who sees a suspicious person and radios the control room. An IPS is a turnstile that refuses to open for that person at all. One warns, the other stops. Most places want both: eyes that watch and a gate that can slam shut.
Watch it happen
Detect or prevent
IDS
- Watches a copy of traffic
- Alerts, never blocks
- No risk of blocking real users
IPS
- Sits inline in the traffic path
- Can drop bad packets live
- A bad rule can block real users
IDS is a safe listener; IPS acts but must sit inline. Teams often run detection widely and prevention on trusted, well tuned rules.
The big ideas
What you need to know
Signatures catch the known
Signature detection matches traffic against patterns of known attacks. Fast and accurate, but blind to brand new tricks.
Anomaly catches the odd
Anomaly detection learns normal traffic and flags what differs. Catches new attacks but gives more false alarms.
Placement matters
An IDS taps a copy of traffic. An IPS must sit in the live path, so its speed and reliability really count.
Tuning is the real work
Out of the box, these tools flood you with noise. Weeks of tuning turn alerts into signal.
See it in code
Walk through the code
1# A Suricata rule: alert on a known bad user agent in HTTP traffic2alert http any any -> any any ( \3 msg:"Suspicious scanner user agent seen"; \4 flow:established,to_server; \5 http.user_agent; content:"sqlmap"; nocase; \6 classtype:web-application-attack; sid:1000001; rev:1; )1/3alert means detect and log. The msg is what shows up in your console.
This rule only alerts, it does not attack anything. Swap the alert keyword for drop in an IPS to block the matching traffic instead.
Save yourself the pain
Common mistakes
Oops
Turning on IPS blocking everywhere on day one.
Do this instead
Run in alert only mode first. Watch what it would block, then switch risky rules to blocking once tuned.
Oops
Relying only on signatures.
Do this instead
Signatures miss new attacks. Pair them with anomaly detection and good logging for the unknowns.
Your mission
Run Suricata in a lab you own
Quick check
Why do many teams deploy IDS widely but IPS blocking more carefully?
Go deeper
- 1Explore an open-source IDS (like Snort or Suricata) and review a sample detection rule.
- 2Learn the trade-off: IDS observes without blocking, IPS blocks but risks false-positive disruption.
- 3Understand the difference between signature-based and anomaly-based detection approaches.
More topics at this stop
 SOC (Security Operations Center) Basics
 SIEM Fundamentals (Splunk, ELK)
 Log Analysis & Correlation
 Threat Hunting Basics
 Security Alerts & Triage
 Endpoint Detection & Response (EDR)
 Threat Intelligence Basics
 MITRE ATT&CK Framework
 Building Detection Rules

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
