SIEM Fundamentals (Splunk, ELK)
Part of the Cybersecurity Roadmap
In short
Your firewall, servers and laptops each keep their own logs in their own corner. A SIEM pulls them all into one searchable place, so you can ask one question and see everything.
Security Information and Event Management systems aggregate logs from across an organization into one searchable platform — the core tool a SOC analyst uses daily to investigate and correlate events.
Think of it like this
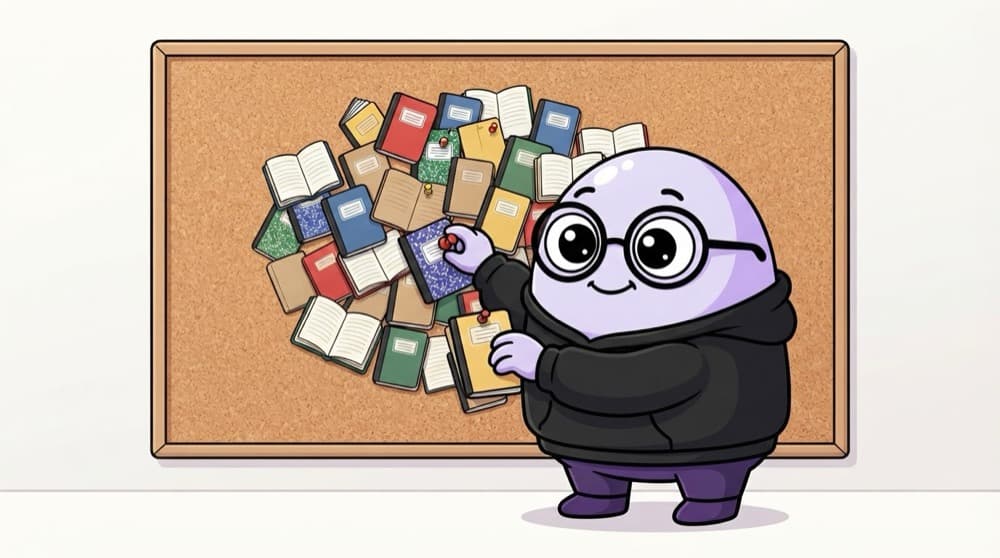
One mega notice board for the whole hostel
Imagine every hostel room kept its own diary. To find who left the gate open, you would read 200 diaries. A SIEM copies every diary into one searchable board, so one search across all rooms answers the question in seconds.
Watch it happen
How logs become answers
1/5Firewalls, servers, cloud and endpoints all produce logs in different shapes.
The big ideas
What you need to know
One place for all logs
SIEM stands for Security Information and Event Management. It collects, stores and searches logs from everywhere.
Parsing is the hard part
Raw logs are messy. Good field extraction, so user and IP always mean the same thing, makes searches reliable.
Each has its own language
Splunk uses SPL, the ELK stack uses KQL or Lucene. Same idea: filter, group and count events.
Storage costs real money
Logs are huge. Decide what to keep hot for fast search and what to archive cheaply.
See it in code
Walk through the code
1# Splunk SPL: find accounts with many failed logins in an hour2index=auth action=failure3| stats count by user, src_ip4| where count > 105| sort - count6 7# ELK KQL: same idea, failed SSH logins from one source8event.action : "failed_login" and source.ip : "203.0.113.5"1/3Pick the auth index and keep only failure events. This is the filter stage.
Both queries filter to failed logins, then group and count. This spots password guessing without reading a single raw log by hand.
Save yourself the pain
Common mistakes
Oops
Sending every log at full volume with no plan.
Do this instead
Pick the sources that help detection first. Too much noise raises cost and buries real signals.
Oops
Trusting timestamps blindly across sources.
Do this instead
Set every system to the same time zone, ideally UTC with NTP, or correlation across logs breaks.
Your mission
Try a free SIEM search
Quick check
Why does a SIEM normalise logs into common fields before you search?
Go deeper
- 1Explore a free or trial SIEM instance (like Splunk's free tier) with sample data.
- 2Practice writing a basic search query to find events matching a specific pattern.
- 3Learn why centralizing logs from many sources is essential for spotting cross-system attack patterns.
More topics at this stop
 SOC (Security Operations Center) Basics
 Log Analysis & Correlation
 Intrusion Detection & Prevention Systems (IDS/IPS)
 Threat Hunting Basics
 Security Alerts & Triage
 Endpoint Detection & Response (EDR)
 Threat Intelligence Basics
 MITRE ATT&CK Framework
 Building Detection Rules

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
