Threat Hunting Basics
Part of the Cybersecurity Roadmap
In short
Alerts tell you about attacks the tools already recognise. Threat hunting is going looking for the ones that slipped past quietly, before they do damage.
Proactively searching for signs of compromise that automated alerts missed — a hypothesis-driven investigation, rather than waiting passively for a SIEM alert to fire.
Think of it like this
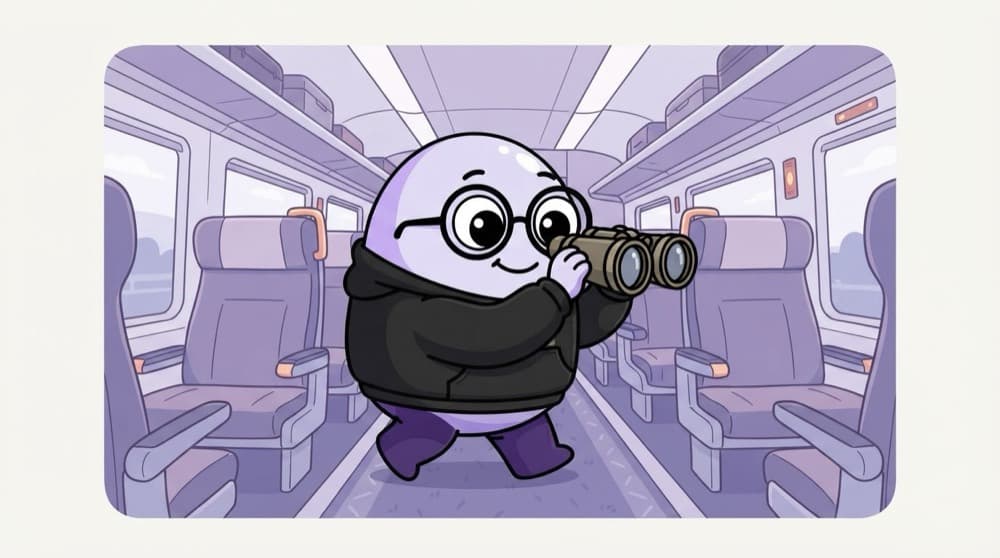
The ticket checker who walks the train
Some checkers sit at the gate and wait. A good one walks through every coach, looking for the passenger quietly hiding without a ticket. Threat hunting is that walk through: you do not wait for an alarm, you go searching with a hunch.
Watch it happen
A hunt, start to finish
1/4Start with a guess, like 'an attacker might use scheduled tasks to stay hidden'.
The big ideas
What you need to know
Hunts start with a hypothesis
You do not search at random. You form a specific guess about how an attacker might hide, then test it.
ATT&CK gives you ideas
The MITRE ATT&CK list of attacker techniques is a ready made menu of things worth hunting for.
Every hunt leaves value
Even a quiet hunt pays off: turn the query you wrote into a saved detection so the tool catches it next time.
Know normal first
You cannot spot the unusual without a solid picture of what normal looks like in your own network.
See it in code
Walk through the code
1# Hunt hypothesis: an attacker added a new persistence task2# KQL over endpoint process logs3DeviceProcessEvents4| where ProcessCommandLine has_any ("schtasks /create", "New-ScheduledTask")5| summarize count() by DeviceName, AccountName, ProcessCommandLine6| order by count_ asc1/3Look across all endpoint process events for task creation commands.
Rare commands on few machines are more interesting than common ones everywhere. Sorting ascending puts the odd one out at the top.
Save yourself the pain
Common mistakes
Oops
Hunting with no hypothesis, just scrolling logs.
Do this instead
Pick one clear question first. A focused hunt finishes and teaches you something; aimless scrolling does not.
Oops
Throwing away a hunt that found nothing.
Do this instead
A clean hunt still gives you a tested query. Save it as a detection so the work keeps paying off.
Your mission
Run one guided hunt
Quick check
What makes threat hunting different from waiting for SIEM alerts?
Go deeper
- 1Form a hypothesis (e.g. 'is there unusual PowerShell activity?') and search sample data to test it.
- 2Learn why threat hunting complements, but doesn't replace, automated detection.
- 3Understand this skill typically develops after strong log analysis fundamentals.
More topics at this stop
 SOC (Security Operations Center) Basics
 SIEM Fundamentals (Splunk, ELK)
 Log Analysis & Correlation
 Intrusion Detection & Prevention Systems (IDS/IPS)
 Security Alerts & Triage
 Endpoint Detection & Response (EDR)
 Threat Intelligence Basics
 MITRE ATT&CK Framework
 Building Detection Rules

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
