Threat Intelligence Basics
Part of the Cybersecurity Roadmap
In short
Why learn an attack the hard way when someone else already got hit by it? Threat intelligence is shared knowledge of current attacks, so you can spot them before they reach you.
Information about known threats, attacker tactics, and indicators of compromise (IOCs) that helps an organization anticipate and detect attacks — sourced from feeds, reports, and shared industry intelligence.
Think of it like this
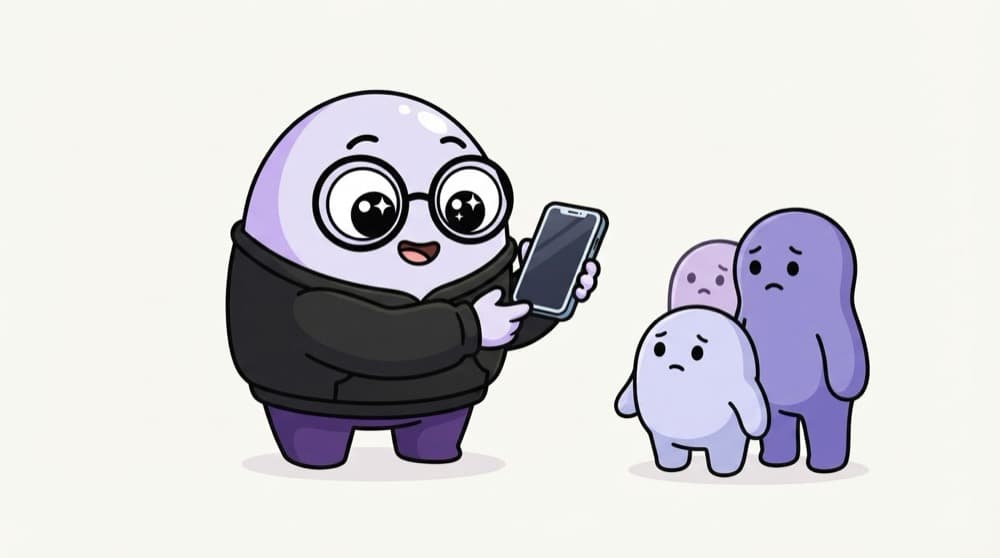
The neighbourhood WhatsApp group
One flat gets a fake courier scam. They post the caller's number and trick in the building group. Now every other flat knows the pattern and is ready. Threat intelligence is that group, but for attacker tools, addresses and methods.
Watch it happen
Raw data to useful intel
1/4Gather from feeds, reports and your own incidents: bad IPs, file hashes, domains.
The big ideas
What you need to know
IOCs are the clues
Indicators of compromise are concrete signs: a bad IP, a domain, a file hash. Feed them to your tools.
Three levels
Strategic for leaders, operational for campaigns, tactical for the IPs and hashes your tools block today.
TTPs beat lone IOCs
Attackers change IPs daily but keep their methods. Knowing their tactics and techniques lasts longer.
Intel goes stale
A bad IP today may be a normal site next month. Expire old indicators or you create false positives.
Save yourself the pain
Common mistakes
Oops
Blindly importing every feed and blocking everything.
Do this instead
Unfiltered feeds cause false positives and block real sites. Pick trusted sources and add context first.
Oops
Chasing only IPs and hashes.
Do this instead
Those change constantly. Focus also on attacker techniques, which are far harder for them to change.
Your mission
Enrich one indicator
Quick check
Why are attacker TTPs often more useful than a list of bad IP addresses?
Go deeper
- 1Explore a free threat intelligence feed or report and identify a specific IOC (like a malicious IP).
- 2Learn the difference between strategic (high-level trends) and tactical (specific IOCs) threat intelligence.
- 3Understand how threat intel feeds into SIEM rules and detection logic.
More topics at this stop
 SOC (Security Operations Center) Basics
 SIEM Fundamentals (Splunk, ELK)
 Log Analysis & Correlation
 Intrusion Detection & Prevention Systems (IDS/IPS)
 Threat Hunting Basics
 Security Alerts & Triage
 Endpoint Detection & Response (EDR)
 MITRE ATT&CK Framework
 Building Detection Rules

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
