
Provision a Multi-Tier Architecture With Terraform
Part of the Cloud Computing Roadmap
In short
This project ties everything together: a VPC, a load balancer, app servers and a private database, all from code. Run one command to build it and one to tear it down. Recruiters love seeing this.
The practice project for this phase — use Terraform to provision a realistic multi-tier setup (networking, compute, database) as a single, reviewable, version-controlled codebase.
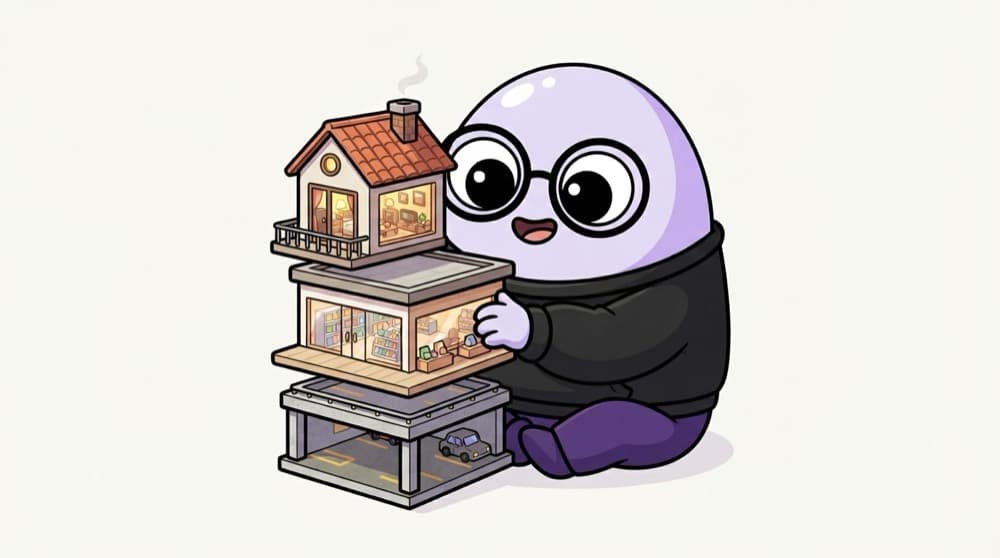
Think of it like this
A three-floor building
Ground floor is parking where visitors enter. First floor is the shop where the work happens. Top floor is the home, private, reachable only by the inside staircase. Web tier, app tier, data tier, stacked with locked doors between them.
Watch it happen
Build plan, one layer at a time
1/5VPC across two AZs: public subnets for the load balancer, private subnets for app and database.
The big ideas
What you need to know
Three tiers
Only the load balancer is public. App and database live in private subnets with no public IPs.
Chained security groups
Each tier allows traffic only from the security group of the tier in front of it.
Modules
Split into network, app and database modules, or use the well-known terraform-aws-modules/vpc for the VPC.
Show your work
A README with an architecture diagram, terraform plan output and a cost note makes this portfolio-ready.
See it in code
Walk through the code
1resource "aws_security_group" "alb" { vpc_id = aws_vpc.main.id }2resource "aws_security_group" "app" { vpc_id = aws_vpc.main.id }3resource "aws_security_group" "db" { vpc_id = aws_vpc.main.id }4 5resource "aws_vpc_security_group_ingress_rule" "db_from_app" {6 security_group_id = aws_security_group.db.id7 referenced_security_group_id = aws_security_group.app.id8 ip_protocol = "tcp"9 from_port = 543210 to_port = 543211}1/3One security group per tier, all in the same VPC.
Terraform removes AWS's default allow-all egress on aws_security_group, so add egress rules where your app needs to call out.
Save yourself the pain
Common mistakes
Oops
Putting the database in a public subnet so you can connect from your laptop.
Do this instead
Keep it private. Use Session Manager port forwarding through an app instance to reach it.
Oops
Committing terraform.tfstate or a DB password to GitHub.
Do this instead
Use a remote backend for state, add *.tfstate to .gitignore, and let RDS manage the password in Secrets Manager.
Your mission
Milestone 1: network and load balancer
Quick check
Which security group rule best protects the database tier?
Go deeper
- 1Design an architecture with at least networking, compute, and a managed database.
- 2Organize your code into reusable modules rather than one giant configuration file.
- 3Document your remote state setup and how you'd safely make changes as a team.

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
