
Threat Actors & Motivations
Part of the Cybersecurity Roadmap
In short
Knowing who might attack you tells you what they want and how hard they'll try. A bored teenager, a ransomware gang and a foreign government need very different defences.
Understanding who attacks systems and why — financially motivated cybercriminals, state-sponsored actors, hacktivists, and insider threats each have different goals, resources, and typical tactics.
Think of it like this
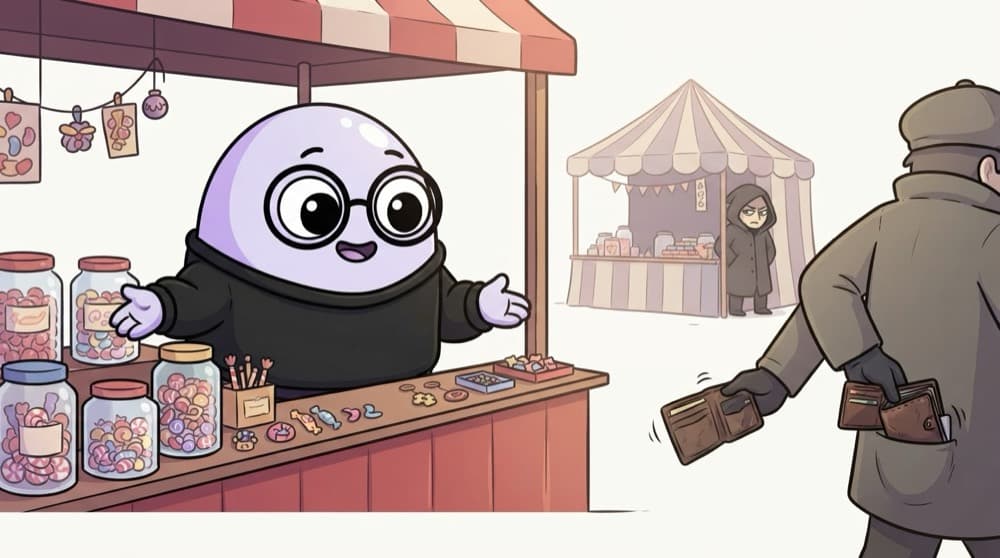
Trouble at the village mela
At a busy fair, the pickpocket wants quick cash, a rival stall owner wants your secret recipe, a protester wants attention, and your own helper might quietly skim the cash box. Same mela, different people, different goals.
Watch it happen
Who attacks, and why
1/6A threat actor is whoever is behind an attack. Their motive shapes how they attack.
The big ideas
What you need to know
Money drives most attacks
Ransomware and fraud are businesses with suppliers, support desks and affiliates. Treat them as organised crime.
Motive predicts the target
A small shop faces criminals, not spies. A defence lab must plan for nation-state actors.
Insiders are hard to spot
They log in legitimately. Least privilege and logging matter more than any firewall here.
Capability varies wildly
Defend first against common, low-effort attacks. They're far more likely than a movie-style operation.
Save yourself the pain
Common mistakes
Oops
Assuming 'we're too small to be a target'.
Do this instead
Criminals scan the whole internet automatically. Anyone with an unpatched server or a weak password is a target.
Oops
Ignoring insiders because you trust your team.
Do this instead
Most insider incidents are accidents. Give people only the access they need, and log what matters.
Your mission
Build a threat profile
Quick check
A group encrypts a hospital's files and demands crypto payment for the key. Who is most likely behind it?
Go deeper
- 1Classify 3 real, publicized breaches by likely threat actor type and motivation.
- 2Learn why understanding motivation helps predict what an attacker is likely to target.
- 3Understand insider threats (malicious or accidental) as a distinct category from external attackers.
More topics at this stop
 What Cybersecurity Professionals Actually Do
 CIA Triad (Confidentiality, Integrity, Availability)
 Types of Security Roles (SOC Analyst, Pentester, GRC, AppSec)
 Common Attack Vectors Overview
 A Day in the Life of a Security Analyst
 The Cybersecurity Career Ladder
 Key Domains Overview (Network, App, Cloud, GRC)
 Security Certifications Landscape (Overview)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
