
Security Orchestration (SOAR) Basics
Part of the Cybersecurity Roadmap
In short
A SOC can get thousands of alerts a day. SOAR tools connect your security tools together and run routine responses automatically, so analysts spend time on the hard cases.
Automating multi-step incident response workflows — SOAR platforms connect multiple security tools together so a routine response (like blocking an IP after a confirmed alert) happens automatically.
Think of it like this
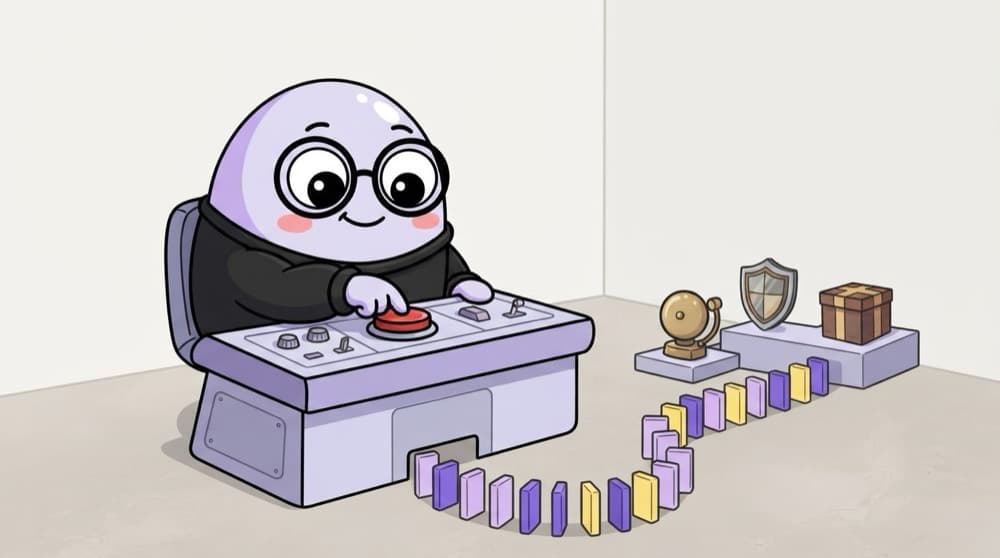
One button, a chain of dominoes
Picture a control desk with one big button. Press it and a line of dominoes falls: a bell rings, a shield goes up, a box gets sealed. You designed the chain once; now it runs the same way every time. A SOAR playbook is that chain.
Watch it happen
A phishing alert playbook
alert: phish reported
1/6An employee reports a suspicious email. The SIEM raises an alert and the playbook starts.
The big ideas
What you need to know
Automate the routine
Enrichment, lookups and ticket creation are perfect for automation. Judgement calls stay with people.
Humans approve big moves
Blocking a CEO's account or isolating a server needs a human click. Wrong automation can cause its own outage.
Playbooks are documents
Write the manual steps first. If you cannot describe the process clearly, you cannot automate it safely.
Measure time saved
Track how long each alert took before and after. Mean time to respond is the number managers care about.
See it in code
Walk through the code
1# Illustrative playbook, not tied to one product2name: phishing-report3trigger: siem.alert.type == "phish_reported"4steps:5 - extract: [sender_domain, urls]6 - enrich: threat_intel.lookup(sender_domain)7 - if: verdict == "malicious"8 then:9 - approval: soc_on_call # human in the loop10 - email.block_domain: sender_domain11 - email.purge_matching: true12 - ticket.create: {severity: medium, attach: all}1/4The trigger decides which alerts start this playbook.
Most SOAR tools express playbooks as steps like these, either in YAML or a visual editor. Note the approval step before anything destructive.
Save yourself the pain
Common mistakes
Oops
Automating account lockouts with no approval or safety limits.
Do this instead
Add approvals and caps for disruptive actions, or a bad rule could lock out half the company.
Oops
Buying a SOAR platform before writing down any processes.
Do this instead
Document and run the playbook by hand first. Automate once the steps are stable and clear.
Your mission
Design a playbook on paper
Quick check
Which step is the best candidate for full automation without human approval?
Go deeper
- 1Read a conceptual overview of a SOAR playbook automating a common response action.
- 2Learn why SOAR reduces analyst fatigue on repetitive, well-understood response steps.
- 3Understand SOAR complements, but doesn't replace, human judgment on complex or ambiguous incidents.
More topics at this stop
 Python for Security Automation
 Vulnerability Scanners (Nessus, OpenVAS)
 Building Custom Security Scripts
 API Integration for Security Tools
 Automating Repetitive Security Tasks
 Version Control for Security Scripts
 Open Source Security Tools Landscape

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
