PowerShell Basics
Part of the Cybersecurity Roadmap
In short
PowerShell can manage a whole Windows network from one window. That's why admins love it, why attackers abuse it, and why defenders need to read it fluently.
Windows' scripting and automation shell — used defensively for administration and investigation, and offensively by attackers ('living off the land') since it's built into every modern Windows machine.
Think of it like this
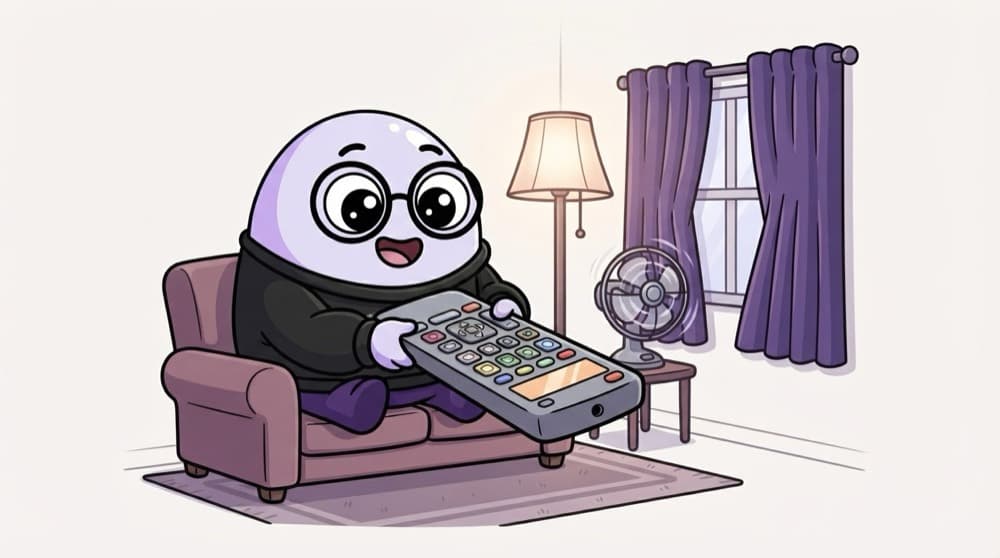
One remote for the whole house
Instead of walking to every switch, one universal remote turns on the lights, fan and curtains together. PowerShell is that remote for Windows. In the wrong hands, though, the same remote controls everything too.
Watch it happen
Objects flowing through a pipeline
1/4Get-Process returns objects, not plain text. Each one has properties like Name, Id and CPU.
The big ideas
What you need to know
Verb-Noun commands
Get-Service, Stop-Process, Get-LocalUser. Get-Help and Get-Command help you discover the rest.
Objects, not text
Output keeps its structure, so filtering and sorting are reliable compared to cutting text.
Attackers 'live off the land'
PowerShell is built in and trusted, so attackers use it instead of bringing their own tools.
Log it
Turn on script block logging (event 4104). It records the code that ran, even when it was obfuscated.
See it in code
Walk through the code
1# PowerShell on your own Windows VM2Get-Process |3 Where-Object { $_.WorkingSet64 -gt 100MB } |4 Sort-Object WorkingSet64 -Descending |5 Select-Object Name, Id, @{n='MB'; e={[int]($_.WorkingSet64 / 1MB)}}6 7Get-NetTCPConnection -State Listen | Select-Object LocalPort, OwningProcess8Get-LocalUser | Where-Object Enabled1/3Get every process, then keep only those using more than 100 MB of memory.
$_ means 'the current object in the pipeline'. 100MB is a real PowerShell number, so no maths needed.
Save yourself the pain
Common mistakes
Oops
Thinking the execution policy blocks attackers.
Do this instead
Microsoft says it isn't a security boundary. It's easy to bypass. Rely on logging and application control.
Oops
Ignoring long base64 strings after -EncodedCommand in logs.
Do this instead
Encoded commands hide what runs. Decode them during investigations and treat them as suspicious until explained.
Your mission
Investigate with PowerShell
Quick check
Why do attackers like using PowerShell on Windows targets?
Go deeper
- 1Write a simple PowerShell script automating a basic Windows administration task.
- 2Learn why PowerShell is a favorite tool for both defenders and attackers on Windows.
- 3Research PowerShell logging and why enabling it matters for detecting malicious use.
More topics at this stop
 Linux Fundamentals for Security
 Linux File Permissions & Users
 Bash Scripting Basics
 Windows Fundamentals for Security
 Windows Active Directory Basics
 Windows Event Logs
 System Hardening Basics
 Command Line Log Analysis
 Virtual Machines & Lab Setup

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
