In short
Your Node app listens on port 3000, but users type a plain domain. Something has to stand in front, handle HTTPS and pass requests along. That's a reverse proxy, and Nginx is the most common one.
A server that sits in front of your application, forwarding client requests to the right backend — commonly used for load balancing, SSL termination, and serving static content efficiently.
Think of it like this
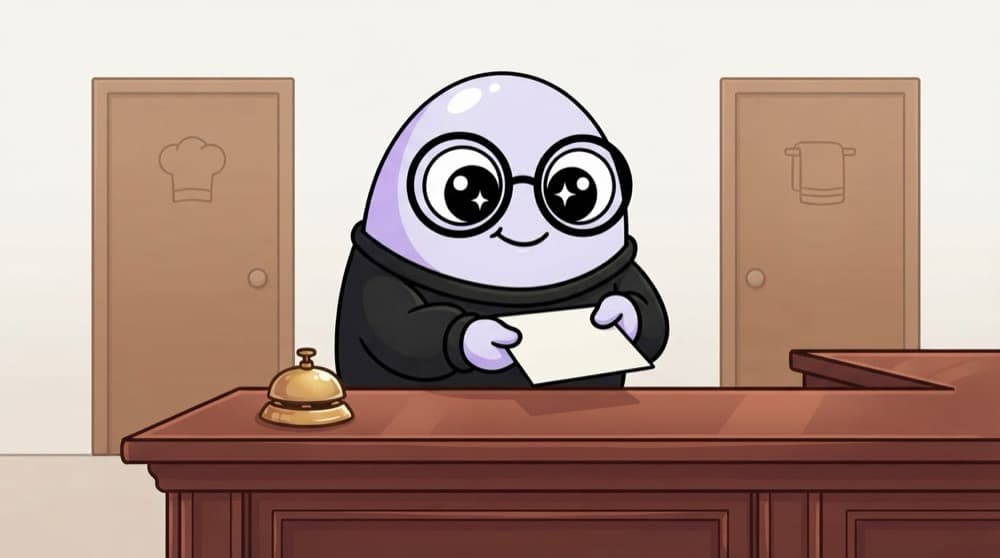
The hotel reception desk
Hotel guests never walk into the kitchen or laundry. They tell reception, and reception sends the request to the right department, then hands back the result. Guests only ever see the front desk. Nginx is that desk for your apps.
Watch it happen
One domain, two apps behind Nginx
GET /api/orders
1/6The browser connects over HTTPS. Nginx holds the certificate and decrypts the request.
The big ideas
What you need to know
Hide the backends
Apps listen only on localhost. The outside world sees just Nginx, so there are fewer doors for attackers.
TLS termination
Nginx handles HTTPS certificates in one place. Tools like Certbot can get and renew free Let's Encrypt certificates.
Route by path or domain
Send api.example.com to one app and /blog to another, all on the same server and port 443.
Forward the real client
Pass headers like X-Forwarded-For so your app logs the user's IP, not Nginx's 127.0.0.1.
See it in code
Walk through the code
1server {2 listen 443 ssl;3 server_name shop.example.com;4 ssl_certificate /etc/letsencrypt/live/shop.example.com/fullchain.pem;5 ssl_certificate_key /etc/letsencrypt/live/shop.example.com/privkey.pem;6 7 location /api/ {8 proxy_pass http://127.0.0.1:3000;9 proxy_set_header Host $host;10 proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;11 }12 13 location / {14 root /var/www/shop;15 }16}1/4Listen for HTTPS on this domain using the certificate and private key.
After any edit, run sudo nginx -t to test the config before sudo systemctl reload nginx.
Save yourself the pain
Common mistakes
Oops
Reloading Nginx after an edit without testing, and taking the site down with a typo.
Do this instead
Run nginx -t first. It checks syntax and refuses to load a broken config.
Oops
Letting the Node app listen on 0.0.0.0:3000 so it's reachable without Nginx.
Do this instead
Bind the app to 127.0.0.1 and block port 3000 in the firewall. Everything should come through the proxy.
Your mission
Put Nginx in front
Quick check
Your app logs every visitor's IP as 127.0.0.1 after you added Nginx. What's the fix?
Go deeper
- 1Set up a basic Nginx reverse proxy forwarding requests to a local application.
- 2Learn how Nginx can handle SSL termination so your backend doesn't need to manage certificates directly.
- 3Understand the difference between a reverse proxy and a forward proxy.
More topics at this stop
 OSI & TCP/IP Models
 IP Addressing & Subnetting
 DNS
 HTTP/HTTPS & TLS
 Load Balancers
 Firewalls & Security Groups
 VPNs & Private Networking
 Common Network Troubleshooting

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
