In short
Terraform creates servers. Something still has to install packages, write config files and restart services on them. Ansible does that over plain SSH, with nothing to install on the servers themselves.
An agentless configuration management tool that connects over SSH to configure servers — commonly used alongside (or instead of) Terraform for installing software and managing configuration on existing infrastructure.
Think of it like this
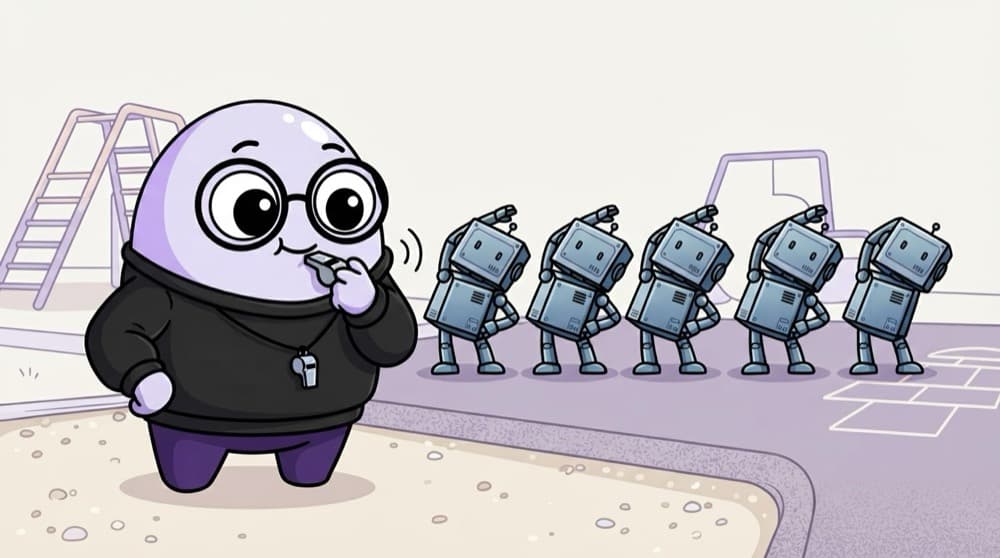
The PT teacher's whistle
At school assembly, the PT teacher doesn't visit each student. One whistle and the whole line does the same stretch at once. Ansible is that teacher: one command from your laptop, and every server in the group runs the same task over SSH.
Watch it happen
One command, two servers
ssh: gather facts
1/5Ansible connects over SSH and collects facts like OS, IP and memory. No agent is needed on web1.
The big ideas
What you need to know
Agentless
Ansible only needs SSH and Python on the target. Nothing to install or keep running on each server.
Inventory
A file listing your hosts in groups like web and db. It can be static or pulled from a cloud API.
Modules do the work
apt, copy, template, service, user: each module knows how to check state and change it safely.
ok vs changed
Good modules only act when needed. Run twice and the second run should report everything as ok.
See it in code
Walk through the code
1# inventory.ini2[web]3web1.example.internal4web2.example.internal5 6# Ad-hoc commands: no playbook needed7ansible web -i inventory.ini -m ping8ansible web -i inventory.ini -b -m apt -a "name=nginx state=present update_cache=true"1/3An inventory with one group called web holding two hosts. Swap in your own hostnames or IPs.
Lines 7 and 8 are shell commands run from your laptop. -b means become root with sudo on the target.
Save yourself the pain
Common mistakes
Oops
Using the shell module for everything, like shell: apt-get install -y nginx.
Do this instead
Use the dedicated module (apt, copy, service). It checks state first, so reruns are safe and reports are accurate.
Oops
Running against all hosts while testing a new task.
Do this instead
Limit it with --limit web1, and use --check --diff for a dry run first.
Your mission
Configure servers you own
Quick check
What must be on a target server for Ansible to manage it?
Go deeper
- 1Write a simple Ansible playbook that installs a package on a target machine.
- 2Learn the difference between Ansible's configuration management focus and Terraform's provisioning focus.
- 3Understand why Ansible being agentless (no software needed on target machines) simplifies adoption.
More topics at this stop
 IaC Concepts & Benefits
 Terraform Fundamentals
 Terraform State Management
 Terraform Modules
 Ansible Playbooks & Roles
 Pulumi / CloudFormation (Overview)
 Idempotency in IaC
 IaC Testing & Validation

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
