
Environment Variables in Production
Part of the Backend Developer Roadmap
In short
One leaked database password can ruin a company overnight. In production, secrets live in environment variables or a secrets manager. Never in code, never in Git, never in a screenshot.
Configuring secrets and settings for your live app safely — using your hosting platform's environment variable dashboard rather than committing any `.env` file to your repo.
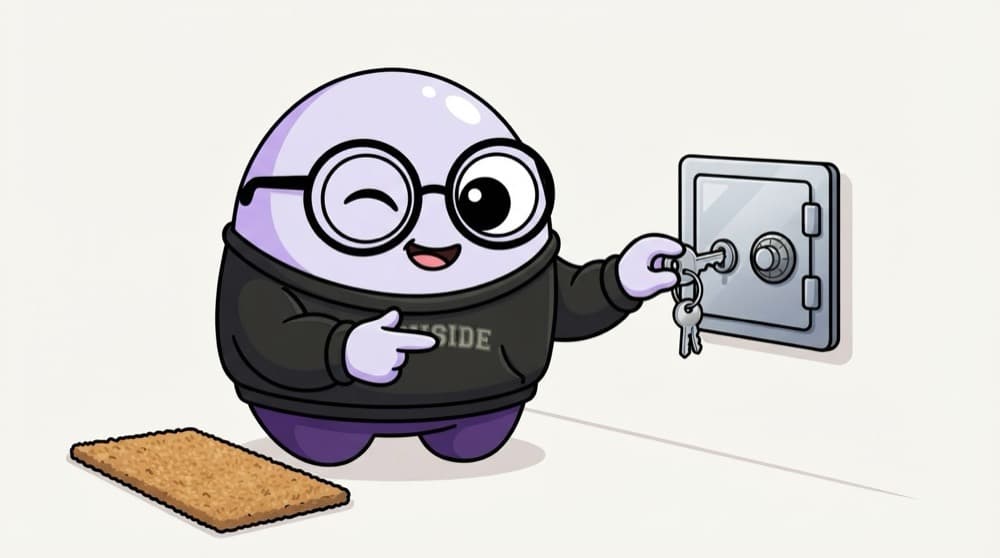
Think of it like this
Not under the doormat
Everyone knows the 'secret' key spot under the doormat, thieves included. A safe with a combination, and a short list of who knows it, is boring but works. Hardcoded keys are the doormat. A secrets manager is the safe, and it can change the combination without new locks.
Watch it happen
Fetching a secret at startup
GetSecretValue db/prod
1/5On boot, the app's IAM role lets it read the database password. No key is stored in the image.
The big ideas
What you need to know
Never in the repo
Not in code, not in a committed .env, not in Dockerfile ENV lines. Git history and image layers keep everything.
Use a secrets store
AWS Secrets Manager, GCP Secret Manager, Doppler or your platform's encrypted env settings keep values out of the image.
Least privilege
Each app reads only the secrets it needs. The blog service shouldn't be able to read the payments key.
Don't log them
Logging the whole config or req.headers can dump tokens into log storage. Redact sensitive fields.
See it in code
Walk through the code
1# Wrong: baked into the image, visible to anyone with the image2# ENV STRIPE_SECRET_KEY=sk_live_xxx3 4FROM node:22-slim5WORKDIR /app6COPY package*.json ./7RUN npm ci --omit=dev8COPY dist ./dist9USER node10CMD ["node", "dist/server.js"]11 12# Right: inject at runtime13# docker run -e STRIPE_SECRET_KEY="$STRIPE_SECRET_KEY" myapi:1.4.01/3ENV values become part of the image. docker history or docker inspect can reveal them.
The image contains code only. Kubernetes Secrets, ECS task definitions or your platform's dashboard supply the values when the container starts.
Save yourself the pain
Common mistakes
Oops
Deleting a leaked key from the repo and moving on.
Do this instead
Bots scrape public repos for keys all the time. Revoke and rotate the key first, then clean the history.
Oops
Sharing production secrets over WhatsApp or email.
Do this instead
Use the secrets manager's access controls or a shared password vault, so access can be removed later.
Your mission
Audit your secrets
Quick check
You pushed an AWS key to a public repo and deleted it in the next commit. What's the right first move?
Go deeper
- 1Set production environment variables through your hosting platform's dashboard, not in code.
- 2Confirm your app fails clearly at startup if a required variable is missing, rather than failing silently later.
- 3Learn how staging and production environments typically use different variable values for the same keys.
More topics at this stop
 Cloud Computing Basics
 AWS EC2
 AWS S3
 AWS Lambda & Serverless
 Railway/Render/Heroku
 Domain & DNS Setup
 HTTPS/SSL Certificates
 CDN Setup
 Google Cloud Platform (Overview)
 Azure (Overview)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
