In short
Without HTTPS, browsers warn 'Not secure' and anyone on the café Wi-Fi can read your API tokens. A certificate is free from Let's Encrypt and takes minutes to set up.
Serving your API securely over encrypted HTTPS — most modern hosting platforms provision and renew free certificates (via Let's Encrypt) automatically.
Think of it like this
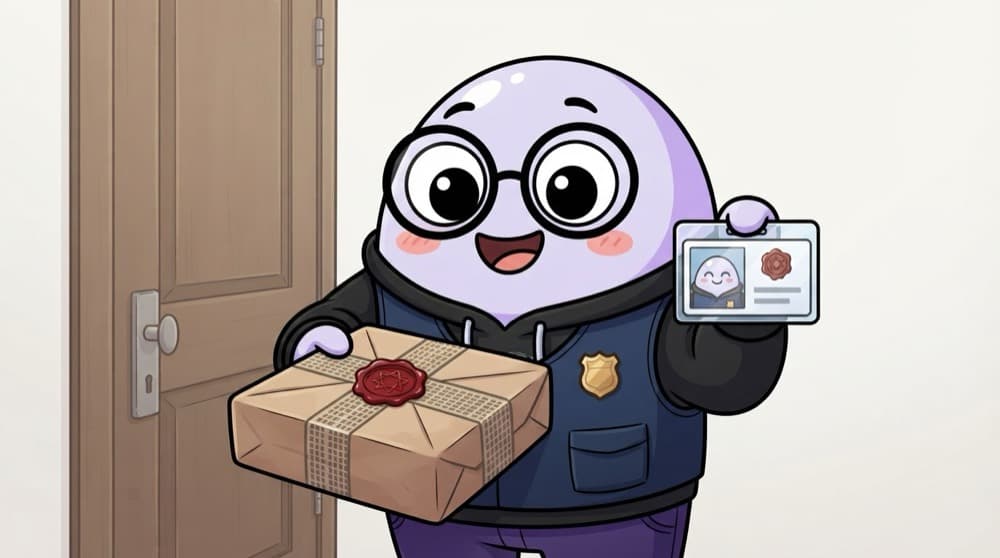
Courier with ID and a sealed packet
A good courier shows a company-issued ID before you sign, and the packet has tamper-proof tape. The ID proves who sent it, the seal proves nobody opened it on the way. A TLS certificate is the ID card, and encryption is the seal.
Watch it happen
The TLS 1.3 handshake, simplified
ClientHello
1/5The browser says hello, lists the ciphers it supports and sends its key share.
The big ideas
What you need to know
Certificate = signed ID
It ties your domain to a public key, signed by a certificate authority that browsers already trust.
Automate renewal
Let's Encrypt certificates are short-lived on purpose. Certbot or your platform should renew them automatically.
HTTPS everywhere
Redirect HTTP to HTTPS and add an HSTS header so browsers stop trying plain HTTP.
Serve the full chain
Send fullchain.pem, not just your own certificate, or some clients can't build the trust chain.
See it in code
Walk through the code
1# On Ubuntu with Nginx already serving api.shop.in on port 802sudo apt install -y certbot python3-certbot-nginx3 4# Get a certificate and let certbot update the Nginx config5sudo certbot --nginx -d api.shop.in --redirect6 7# Renewal runs on a timer; test that it works8sudo certbot renew --dry-run9 10# Inspect what the world sees11openssl s_client -connect api.shop.in:443 -servername api.shop.in </dev/null \12 | openssl x509 -noout -subject -issuer -dates1/4Install certbot and its Nginx plugin.
Let's Encrypt checks you control the domain by fetching a file over port 80, so DNS must already point at this server.
Save yourself the pain
Common mistakes
Oops
Setting a calendar reminder to renew certificates by hand.
Do this instead
Someone will miss it and users get a scary browser error. Automate renewal and monitor expiry dates.
Oops
Turning off certificate checks with rejectUnauthorized: false.
Do this instead
That makes HTTPS pointless, since anyone can pretend to be the server. Fix the certificate instead.
Your mission
Get the padlock
Quick check
During the TLS handshake, what does the browser check about the certificate?
Go deeper
- 1Confirm your deployed API automatically has a valid HTTPS certificate.
- 2Learn what Let's Encrypt is and how automatic certificate renewal works.
- 3Understand why plain HTTP APIs are unacceptable for anything handling real user data.
More topics at this stop
 Cloud Computing Basics
 AWS EC2
 AWS S3
 AWS Lambda & Serverless
 Railway/Render/Heroku
 Environment Variables in Production
 Domain & DNS Setup
 CDN Setup
 Google Cloud Platform (Overview)
 Azure (Overview)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
