
Rate Limiting Middleware
Part of the Backend Developer Roadmap
In short
One buggy script or one bot can send thousands of requests a minute and slow your API for everyone. A rate limiter says: this many, then wait.
Middleware (like `express-rate-limit`) that caps how many requests a client can make in a time window — protects your API from abuse and accidental overload.
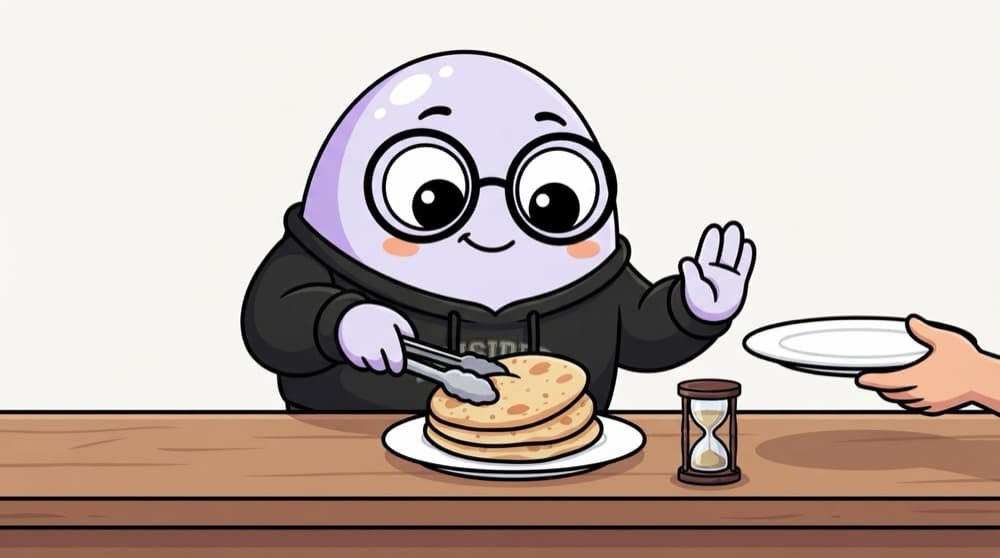
Think of it like this
Two rotis per round at the mess
At the hostel mess, the server gives two rotis per round. Want more? Come back after a bit. Nobody gets turned away for good, but nobody empties the tray either. Rate limiting does that per user or IP.
Watch it happen
Limit: 5 requests per minute per IP
1/5A new one-minute window starts when the first request from this IP arrives.
The big ideas
What you need to know
429 Too Many Requests
The standard status for 'slow down'. Good clients read it and retry later.
Stricter on sensitive routes
Login and OTP routes need tight limits, like 5 tries per 15 minutes, to stop password guessing.
Share counters across servers
The default memory store counts per process. With several servers, use a shared store like Redis.
Behind a proxy, set trust proxy
Behind a load balancer every request looks like one IP. app.set("trust proxy", 1) reads the real client IP.
See it in code
Walk through the code
1import { rateLimit } from "express-rate-limit";2 3const apiLimiter = rateLimit({4 windowMs: 60 * 1000, // 1 minute5 limit: 100, // 100 requests per IP per window6 standardHeaders: "draft-7",7 legacyHeaders: false,8});9 10const loginLimiter = rateLimit({ windowMs: 15 * 60 * 1000, limit: 5 });11 12app.set("trust proxy", 1); // only if you're behind one proxy, like a load balancer13app.use("/api", apiLimiter);14app.post("/auth/login", loginLimiter, loginHandler);1/4A general limit: 100 requests per IP every minute.
Set trust proxy to match your real setup. Trusting too many hops lets clients fake their IP with a header.
Save yourself the pain
Common mistakes
Oops
Running three server instances with the default memory store, so each allows the full limit.
Do this instead
Use a shared store such as Redis so every instance counts the same requests.
Oops
Using one generous limit for everything, including login.
Do this instead
Give sensitive routes like login, OTP and password reset their own tight limits.
Your mission
Throttle a route
Quick check
Your API runs behind a load balancer without trust proxy set. What goes wrong with IP rate limiting?
Go deeper
- 1Add rate limiting to a login endpoint to slow down brute-force attempts.
- 2Configure different rate limits for authenticated vs unauthenticated requests.
- 3Learn how rate limiting interacts with running multiple server instances — it needs shared storage like Redis.
More topics at this stop
 Express Basics
 Routing
 Middleware
 Request & Response Objects
 Error Handling Middleware
 Route Parameters
 Query Parameters
 Request Validation
 File Uploads
 Static Files
 Templating (EJS/Pug)
 Express Router
 Alternative Frameworks (Fastify, NestJS, Koa)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
