Request Validation
Part of the Backend Developer Roadmap
In short
Anything can arrive in a request: missing fields, wrong types, a 10 MB name. Validation checks input at the door, so bad data never reaches your database.
Checking that incoming request data (body, params, query) matches your expected shape and constraints before your business logic runs — your API's first line of defense.
Think of it like this
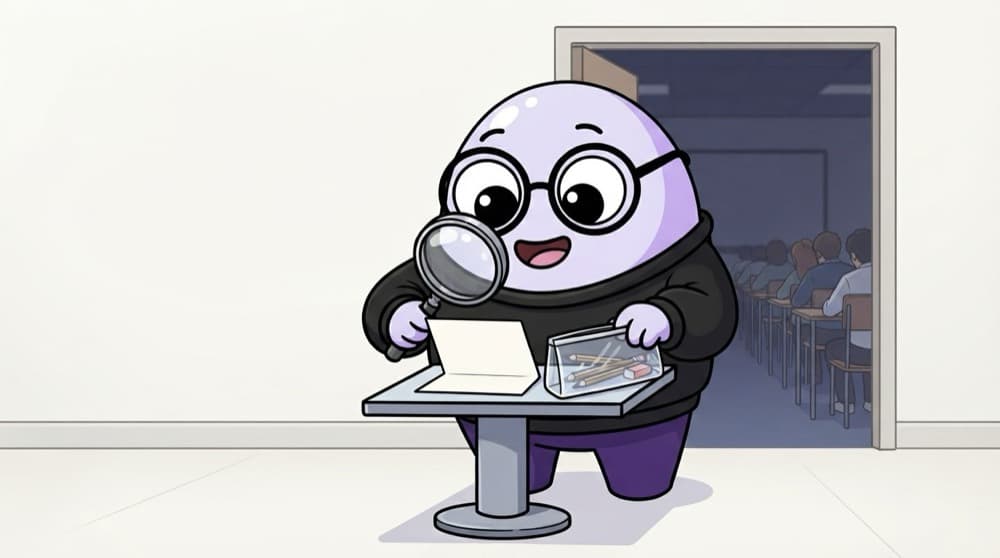
The exam hall invigilator
Before you enter the exam hall, the invigilator checks your admit card, your photo ID and that your pencil pouch is see-through. Missing anything? You don't get in. Validation is that invigilator for every request.
Watch it happen
Validating a signup request
POST /signup
1/6Body: { email: "riya@", age: "17" }. The email is broken and age is a string.
The big ideas
What you need to know
Never trust the client
Frontend checks are for user comfort. Anyone can skip them with curl, so the server must check again.
Describe with a schema
Libraries like Zod or Joi let you declare rules once: required, type, length, format.
Strip unknown fields
Only keep fields you expect. Otherwise someone can sneak in role: "admin" with their signup.
Helpful 400 errors
Tell the client which field failed and why, so the frontend can show it next to the input.
See it in code
Walk through the code
1import { z } from "zod";2 3const SignupSchema = z.object({4 email: z.string().email(),5 password: z.string().min(8).max(72),6 age: z.number().int().min(18),7});8 9app.post("/signup", (req, res) => {10 const result = SignupSchema.safeParse(req.body);11 if (!result.success) {12 return res.status(400).json({ errors: result.error.flatten().fieldErrors });13 }14 const { email, password, age } = result.data; // typed and clean15 res.status(201).json({ email, age });16});1/4One schema describes a valid signup: a real email, a password of sensible length, an adult age.
z.object drops keys it doesn't know by default, so an extra role: "admin" in the body never reaches result.data.
Save yourself the pain
Common mistakes
Oops
Validating only on the frontend form.
Do this instead
Always validate on the server too. The server is the only place you control.
Oops
Validating, then still using req.body instead of the parsed result.
Do this instead
Use the validated output. It has the right types and no unexpected extra fields.
Your mission
Validate a product API
Quick check
The frontend form already checks the email format. Why validate on the server too?
Go deeper
- 1Add validation to a POST endpoint using a library like Zod, Joi, or express-validator.
- 2Return clear, field-specific error messages when validation fails.
- 3Learn to validate at the API boundary even if your database also has constraints.
More topics at this stop
 Express Basics
 Routing
 Middleware
 Request & Response Objects
 Error Handling Middleware
 Route Parameters
 Query Parameters
 File Uploads
 Static Files
 Templating (EJS/Pug)
 Express Router
 Rate Limiting Middleware
 Alternative Frameworks (Fastify, NestJS, Koa)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
