Metasploit Framework
Part of the Cybersecurity Roadmap
In short
Metasploit is a well known security testing framework. For learners, the useful part is understanding what such tools do, so defenders can recognise and block the activity they generate.
A widely used exploitation framework bundling known exploits, payloads, and post-exploitation modules — accelerates testing but should be understood, not used as an unthinking black box.
Think of it like this
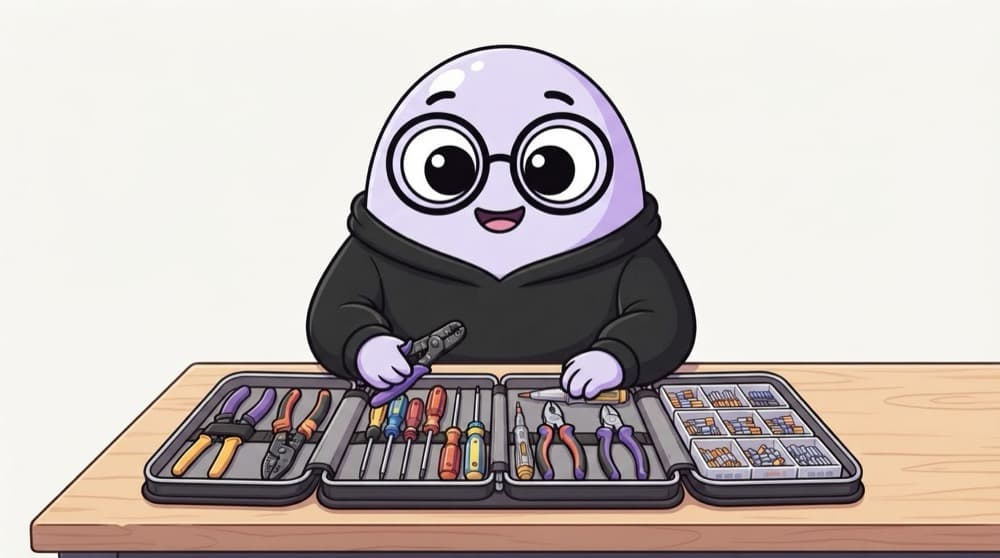
A standardised toolkit
A professional electrician carries one organised kit instead of loose tools, so every job is consistent. Metasploit organises security testing modules the same way. Knowing it exists helps defenders recognise its footprints in their logs.
Watch it happen
Why defenders study these tools
1/4A framework bundles known modules into a single, repeatable testing tool.
The big ideas
What you need to know
Know your adversary's tools
Defenders study common testing frameworks so they can recognise and block the same activity from real attackers.
Tools leave fingerprints
Standard frameworks generate known signatures. IDS and EDR rules can detect their default behaviour.
Authorised use only
Such frameworks belong in sanctioned tests on systems you own or have written permission to assess.
Patching still wins
These frameworks mostly bundle known issues. Keeping systems patched removes what they rely on.
Save yourself the pain
Common mistakes
Oops
Pointing a testing framework at a system you do not own.
Do this instead
Use it only in your own lab or an authorised engagement. Unauthorised use is illegal, whatever the tool.
Oops
As a defender, assuming you will never see these tools.
Do this instead
Real attackers use the same frameworks. Build detections for their known signatures and keep systems patched.
Your mission
Detect a known tool signature
Quick check
Why should a defender understand common security testing frameworks?
Go deeper
- 1Use Metasploit to exploit a known vulnerability on a practice VM.
- 2Learn the basic structure: exploits, payloads, and modules.
- 3Practice explaining what a chosen exploit is actually doing, not just running it blindly.
More topics at this stop
 Penetration Testing Methodology
 Reconnaissance & OSINT
 Scanning & Enumeration (Nmap)
 Exploitation Basics
 Burp Suite Fundamentals
 Privilege Escalation
 Post-Exploitation Basics
 Password Attacks & Cracking
 Wireless Security Testing (Overview)
 Report Writing for Pentests

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
