
Post-Exploitation Basics
Part of the Cybersecurity Roadmap
In short
After a foothold, attackers try to stay hidden, spread, and show impact. Understanding these goals tells defenders exactly what signs to hunt for after a breach.
What happens after gaining access — maintaining persistence, moving laterally to other systems, and gathering evidence of impact, all carefully scoped within an authorized engagement.
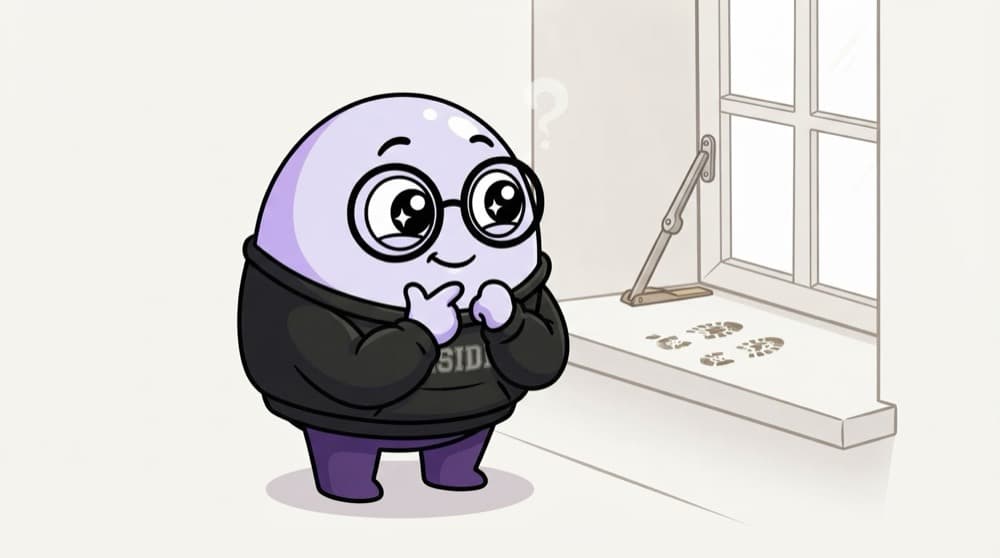
Think of it like this
The burglar who wants to return
A clever burglar does not just grab one thing. They prop a window so they can come back, learn the layout, and check which neighbours have valuables. Spotting those traces, a propped window, is how you catch them. Post-exploitation is the digital version.
Watch it happen
Attacker goals, and detections
1/4Post-exploitation covers what an attacker does after getting in, all things defenders can watch for.
The big ideas
What you need to know
Hunt for persistence
Attackers plant ways back in. New scheduled tasks, services or accounts deserve a close look.
Watch lateral movement
Spreading between machines leaves a trail of unusual internal logins. Correlate them across hosts.
Spot data collection
Sudden bulk reads or large outbound transfers hint someone is gathering data to steal.
Segmentation limits spread
Splitting the network into zones means one foothold cannot quietly reach everything else.
Save yourself the pain
Common mistakes
Oops
Assuming an incident ends when you find the first foothold.
Do this instead
Attackers plant persistence and move sideways. Hunt for extra accounts, tasks and odd logins before closing.
Oops
Having a flat network where everything can reach everything.
Do this instead
Segment the network. Zones and tight firewall rules stop one compromised host from spreading freely.
Your mission
List persistence signs
Quick check
What are defenders mainly hunting for in post-exploitation activity?
Go deeper
- 1Practice basic post-exploitation techniques (like data enumeration) on a lab target.
- 2Learn why 'lateral movement' is often how attackers turn one compromised machine into a full breach.
- 3Understand post-exploitation activity should always stay within the agreed scope of an engagement.
More topics at this stop
 Penetration Testing Methodology
 Reconnaissance & OSINT
 Scanning & Enumeration (Nmap)
 Exploitation Basics
 Metasploit Framework
 Burp Suite Fundamentals
 Privilege Escalation
 Password Attacks & Cracking
 Wireless Security Testing (Overview)
 Report Writing for Pentests

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
