AWS Core Services (EC2, S3, VPC, IAM)
Part of the DevOps Roadmap
In short
AWS has hundreds of services, but almost every architecture leans on the same four. Learn EC2, S3, VPC and IAM properly and the rest of the console starts to make sense.
The foundational AWS building blocks — EC2 (virtual servers), S3 (object storage), VPC (private networking), and IAM (identity and access management) — nearly every AWS architecture is built from these four.
Think of it like this
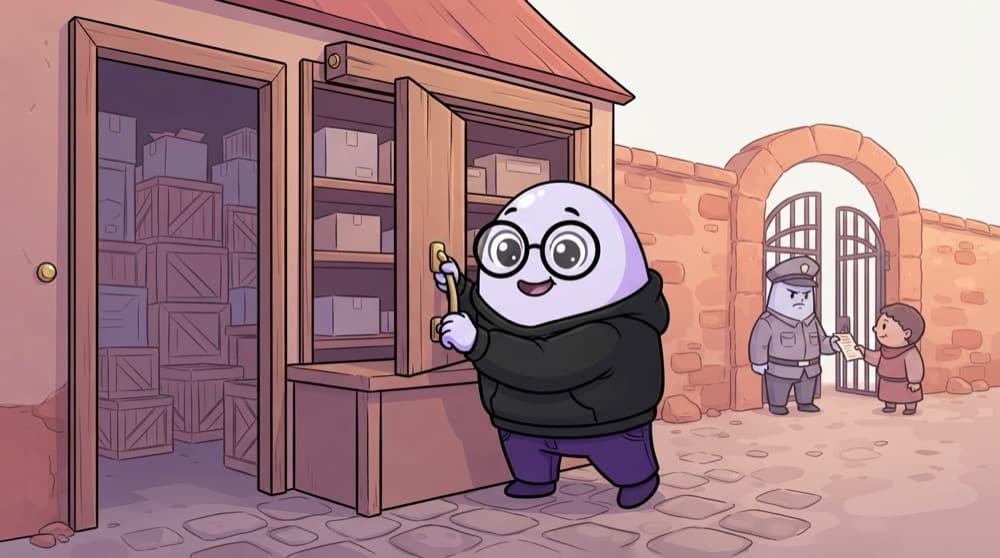
Opening a shop in a market
You rent a shop unit (EC2), keep stock in a storeroom behind it (S3), inside a walled market compound with its own gate and lanes (VPC). The guard checks passes so only your staff reach the storeroom (IAM). Four pieces, one working business.
Watch it happen
Serving a photo from S3 via EC2
GET /photos/42
1/6The request reaches your app on an EC2 instance, which sits in a subnet of your VPC.
The big ideas
What you need to know
EC2: virtual servers
Pick an instance type (CPU and memory) and an AMI (the OS image). You manage the OS from there.
S3: object storage
Store files as objects in buckets. Very durable, priced per GB and request. Keep buckets private by default.
VPC: your private network
Your own IP range, split into subnets across zones, with route tables deciding what reaches the internet.
IAM: who can do what
Users, roles and policies. Give apps roles instead of access keys, and grant only the actions they need.
See it in code
Walk through the code
1# Who am I? (checks your credentials)2aws sts get-caller-identity3 4# S3: make a bucket and upload a file5aws s3 mb s3://riya-notes-demo-2026 --region ap-south-16aws s3 cp notes.txt s3://riya-notes-demo-2026/7 8# EC2 and VPC: list what's running9aws ec2 describe-instances --query "Reservations[].Instances[].InstanceId"10aws ec2 describe-vpcs --query "Vpcs[].CidrBlock"1/3Always run this first. It shows which account and identity your commands will act as.
Set up the AWS CLI with aws configure or aws configure sso. Delete the bucket afterwards with aws s3 rb s3://<name> --force.
Save yourself the pain
Common mistakes
Oops
Using the root account login for daily work.
Do this instead
Turn on MFA for root, lock it away, and create a separate admin identity (IAM Identity Center or an IAM user) for everyday use.
Oops
Pasting access keys into application code or a public GitHub repo.
Do this instead
Use IAM roles for EC2, Lambda and containers. Leaked keys are found by bots and abused within minutes.
Your mission
Four services in one sitting
Quick check
Your app on EC2 needs to read from S3. What's the safest way to give it access?
Go deeper
- 1Launch a free-tier EC2 instance and connect to it via SSH.
- 2Create an S3 bucket and practice uploading/retrieving a file.
- 3Set up a basic VPC with public and private subnets, and an IAM user with limited permissions.
More topics at this stop
 Cloud Computing Fundamentals
 AWS Networking & Security
 GCP Fundamentals (Overview)
 Azure Fundamentals (Overview)
 Cloud Cost Management
 Auto Scaling
 Serverless Basics (Lambda / Functions)
 Multi-Cloud & Hybrid Cloud Concepts
 Cloud Certifications Overview
 Cloud Well-Architected Framework

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
