In short
'Permission denied' is the error you will see most in your first months. Once you can read those rwx letters, you'll fix it in seconds instead of googling for an hour.
Linux's read/write/execute permission model for owner, group, and others — understanding chmod and chown is essential for both security and for debugging 'permission denied' errors constantly.
Think of it like this
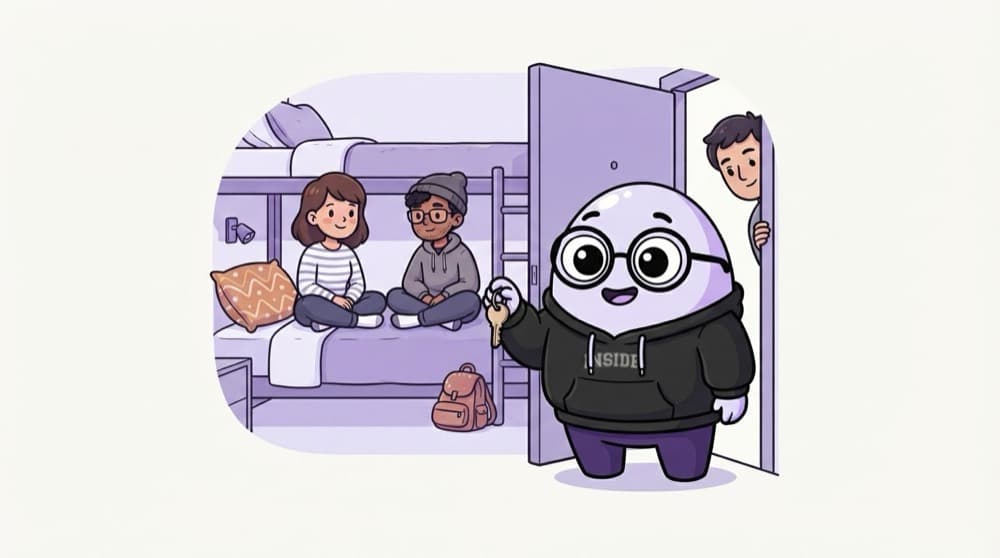
A hostel room and three kinds of people
You own the room and can do anything. Your roommates (the group) can use the cupboard but not your laptop. Random visitors (others) can only peek through the door. Linux gives every file the same three circles: owner, group, others.
Watch it happen
Reading -rwxr-x--- deploy.sh
1/4The first character is the type. - means a normal file, d means a directory.
The big ideas
What you need to know
r=4, w=2, x=1
Add them per circle. 644 means owner reads and writes, everyone else only reads. Common for config files.
x on a folder means enter
Without execute permission on a directory, you can't cd into it, even if you can read its files.
chown changes the owner
chown www-data:www-data file gives a file to the web server user, so nginx can read it.
777 is not a fix
chmod 777 lets anyone change the file. It hides the real problem and opens a security hole.
See it in code
Walk through the code
1ls -l deploy.sh2# -rw-r--r-- 1 riya devs 512 Oct 27 deploy.sh3 4chmod +x deploy.sh # add execute5chmod 750 deploy.sh # owner rwx, group r-x, others none6sudo chown riya:devs deploy.sh7 8chmod 600 ~/.ssh/id_ed25519 # private keys: owner only1/4ls -l shows permissions, owner (riya) and group (devs) for the file.
SSH refuses to use a private key that others can read. chmod 600 is the usual fix.
Save yourself the pain
Common mistakes
Oops
Fixing 'permission denied' with chmod -R 777 on the whole folder.
Do this instead
Find which user the process runs as, then give that user just the access it needs with chown or chmod 640.
Oops
Using sudo for every command so permissions never bother you.
Do this instead
Files created with sudo end up owned by root, causing new errors later. Use sudo only for system tasks.
Your mission
Lock it down
Quick check
A file has mode 640. Who can edit it?
Go deeper
- 1Practice reading a permission string (e.g. rwxr-xr--) and translating it into plain English.
- 2Use chmod and chown to change permissions and ownership on test files.
- 3Learn the difference between numeric (755) and symbolic (u+x) chmod syntax.
More topics at this stop
 Linux Fundamentals
 File System Navigation
 Process Management
 Package Managers (apt, yum)
 Shell Scripting Basics (Bash)
 Text Processing (grep, sed, awk)
 System Logs & journalctl
 Cron Jobs & Scheduling
 SSH & Remote Access
 systemd & Service Management

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
