In short
HTTP forgets you after every request. Sessions are how servers remember who you are, what's in your cart and whether you're logged in.
A server-side mechanism for remembering a user across multiple requests, typically identified by a session ID stored in a cookie. The server maintains session state while the browser normally carries only an identifier, making session lifecycle, expiration, rotation, and invalidation important parts of secure authentication.
Think of it like this
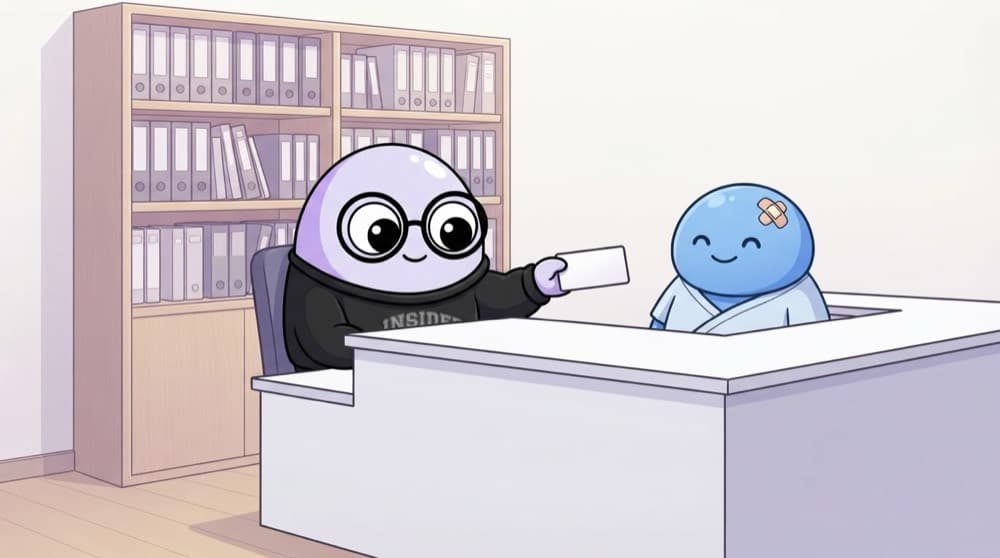
A hospital file number
At reception they give you a file number. The doctor uses it to pull up your full history. You only carry the number; the hospital keeps the file. A session works exactly like that.
Watch it happen
Life of a session
log in
1/6You log in with your password.
The big ideas
What you need to know
Data lives on the server
The server stores session data, like your user ID, cart or role, in memory, a database or Redis.
The browser holds only an ID
A random session ID, usually in a cookie, links the browser to its data on the server.
Sessions expire
Servers end sessions after some idle time or on logout, so a stolen ID stops working.
Sessions vs tokens
With sessions the server remembers you. With tokens like JWT, the browser carries signed details and the server just verifies them.
See it in code
Walk through the code
1import session from "express-session";2 3app.use(session({4 secret: process.env.SESSION_SECRET,5 resave: false,6 saveUninitialized: false,7 cookie: { httpOnly: true, secure: true, maxAge: 1000 * 60 * 60 },8}));9 10app.post("/login", (req, res) => {11 req.session.userId = user.id; // stored on the server12 res.send("Logged in");13});1/3Set up sessions: a secret to sign the cookie, and a cookie that's HttpOnly, HTTPS-only and lasts an hour.
express-session keeps userId on the server and gives the browser only a session ID cookie that lasts one hour.
Save yourself the pain
Common mistakes
Oops
Keeping the same session ID before and after login.
Do this instead
Create a fresh session ID on login, so an old, possibly leaked ID can't be reused.
Oops
Sessions that never expire.
Do this instead
Set an idle timeout and clear the session on logout.
Your mission
Trace a session
Quick check
In a session-based login, what does the browser actually store?
Go deeper
- 1Learn how a typical login flow creates and validates a session. Focus on understanding the underlying reason it works, not only memorizing the definition.
- 2Compare session-based auth with token-based (JWT) auth. Write down when you would choose each option and what trade-off drives that choice.
- 3Understand what happens to a session when a user logs out.
More topics at this stop
 Internet
 HTTP vs HTTPS
 DNS
 Browser rendering
 Request-response cycle
 Client vs Server
 Cookies
 LocalStorage
 SessionStorage
 Cache
 CDN
 REST APIs
 JSON

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
