In short
Once your app grows into several services, clients shouldn't have to know them all. An API gateway gives the world one front door and handles the boring checks in one place.
A single entry point that sits in front of one or more backend services, handling routing, authentication, rate limiting and logging before requests reach your actual application code.
Think of it like this
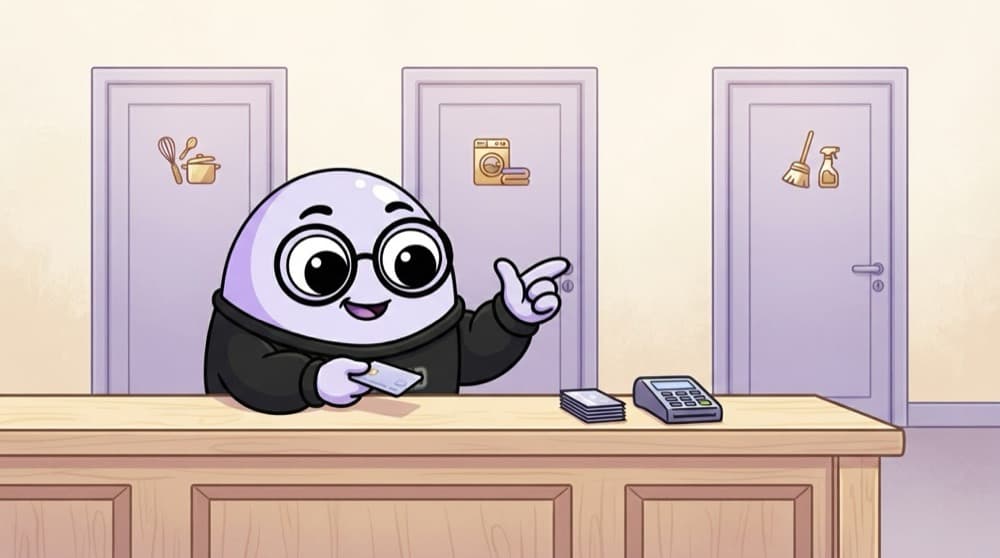
The hotel front desk
Guests don't wander into the kitchen or the laundry. They go to the front desk, which checks the room key and sends each request to the right team. If too many requests pile up, the desk asks guests to wait. That desk is your API gateway.
Watch it happen
One front door, many services
GET /api/orders/42
1/8The app only knows one address: api.example.com.
The big ideas
What you need to know
Routing by path
/api/orders goes to one service, /api/users to another. Clients see one host and one set of URLs.
Shared checks in one place
Auth, rate limits, CORS, TLS and request logs live at the gateway instead of being copied into every service.
Many ways to run one
Nginx, Kong, cloud API gateways, or a small Express proxy can all play this role.
Keep it thin and reliable
Every request passes through it, so avoid business logic there and run more than one instance.
See it in code
Walk through the code
1import express from "express";2import { createProxyMiddleware } from "http-proxy-middleware";3 4const gateway = express();5 6gateway.use((req, res, next) => {7 if (!req.headers.authorization) return res.status(401).json({ error: "Login first" });8 next();9});10 11const toService = (path, port) =>12 createProxyMiddleware({ pathFilter: path, target: `http://localhost:${port}`, pathRewrite: { "^/api": "" } });13 14gateway.use(toService("/api/orders", 4001));15gateway.use(toService("/api/users", 4002));16gateway.listen(8080);1/4One auth check for every service. A real gateway would verify the token, not just check it exists.
Install with npm i express http-proxy-middleware. The services on 4001 and 4002 never see requests without a token, and clients only ever talk to port 8080.
Save yourself the pain
Common mistakes
Oops
Putting business rules, like discount logic, inside the gateway.
Do this instead
Keep the gateway thin: routing, auth checks, limits and logging. Business logic belongs in the services.
Oops
Running a single gateway instance with no health checks.
Do this instead
If it goes down, everything goes down. Run at least two behind a load balancer and monitor them.
Your mission
Build a mini gateway
Quick check
What's the main reason to put an API gateway in front of several services?
Go deeper
- 1Read how an API gateway differs from a simple reverse proxy.
- 2Learn common gateway responsibilities: auth, rate limiting, request routing, logging.
- 3Explore a managed gateway (AWS API Gateway, Kong) to see what it configures out of the box.
More topics at this stop
 Internet
 HTTP vs HTTPS
 DNS
 Client-Server Architecture
 Request-Response Cycle
 HTTP Methods
 HTTP Status Codes
 Statelessness
 REST Principles
 JSON
 XML
 Headers & Cookies
 CORS
 Idempotency

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
