
Configuration Management (Ansible Overview)
Part of the Cloud Computing Roadmap
In short
Terraform creates the servers. Something still has to install packages, write config files and start services on them. Ansible does that, on one server or two hundred, with the same short playbook.
A complementary tool to Terraform — while Terraform provisions infrastructure, Ansible configures software and settings on existing servers, connecting agentlessly over SSH.
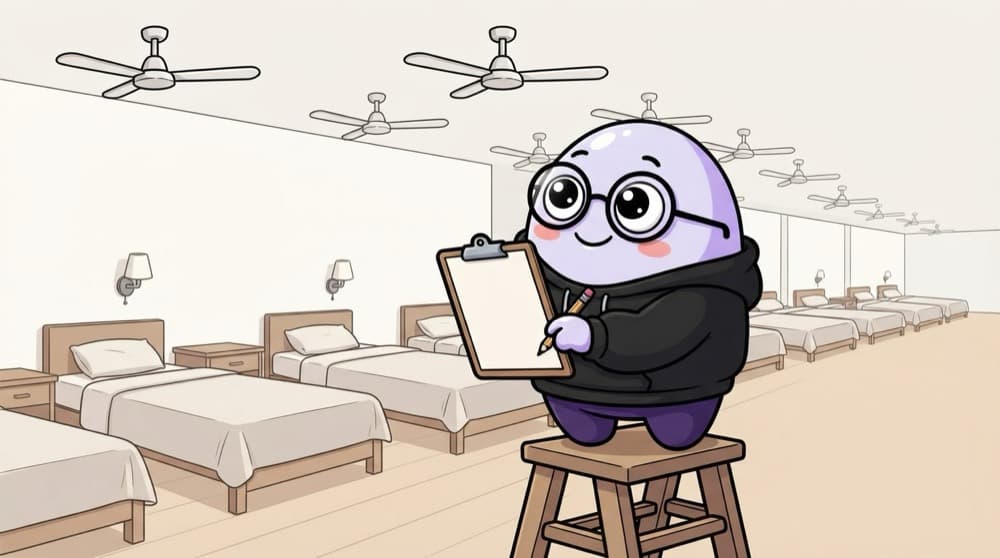
Think of it like this
The warden's room checklist
Before a new term, the warden walks every room with one checklist: fan works, bulb fitted, bed present. Room 12 has no bulb, so he fits one. Room 13 is fine, so he moves on. Checking again changes nothing. That's Ansible.
Watch it happen
One playbook, four servers, two runs
1/5The inventory lists four web servers. The playbook says: nginx installed and running.
The big ideas
What you need to know
Agentless
Ansible connects over SSH (or WinRM for Windows). Nothing extra to install on the servers.
Inventory
A file or a dynamic plugin listing your hosts and groups, such as [web] and [db].
Playbooks in YAML
Playbooks list tasks using modules like apt, copy, template and service. Each describes a desired state.
Where it fits
Terraform builds infrastructure; Ansible configures inside machines. With containers, much of this moves into the Dockerfile.
See it in code
Walk through the code
1- name: Set up web servers2 hosts: web3 become: true4 tasks:5 - name: Install nginx6 ansible.builtin.apt:7 name: nginx8 state: present9 update_cache: true10 11 - name: Make sure nginx is running12 ansible.builtin.service:13 name: nginx14 state: started15 enabled: true1/3Target the web group and use sudo (become) for package installs.
Run with ansible-playbook -i inventory.ini web.yml. Add --check to see what would change without changing anything.
Save yourself the pain
Common mistakes
Oops
Using ansible.builtin.shell for everything, like shell: apt install -y nginx.
Do this instead
Use real modules. They check current state first, so reruns are safe and reports are accurate.
Oops
Putting passwords in plain text in playbooks or inventory.
Do this instead
Encrypt them with Ansible Vault or pull them from a secrets manager at run time.
Your mission
Configure a server twice
Quick check
You run the same Ansible playbook twice. What should the second run report?
Go deeper
- 1Write a simple Ansible playbook that installs a package on a target machine.
- 2Learn the difference between Ansible's configuration management focus and Terraform's provisioning focus.
- 3Understand these tools are often used together: Terraform provisions, Ansible configures.
More topics at this stop
 IaC Concepts & Benefits
 Terraform Fundamentals
 CloudFormation / ARM Templates / Deployment Manager
 Terraform State Management
 Terraform Modules
 CI/CD for Cloud Deployments
 GitOps Basics
 IaC Testing & Validation

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
