Firewalls & Security Groups
Part of the Cloud Computing Roadmap
In short
A fresh server on the internet gets poked by bots within minutes. Firewalls decide which knocks get answered, and in the cloud, security groups are usually the first rule you'll write.
Controlling what network traffic is allowed in and out of your cloud resources — security groups and network ACLs are the cloud-native mechanisms that serve this purpose.
Think of it like this
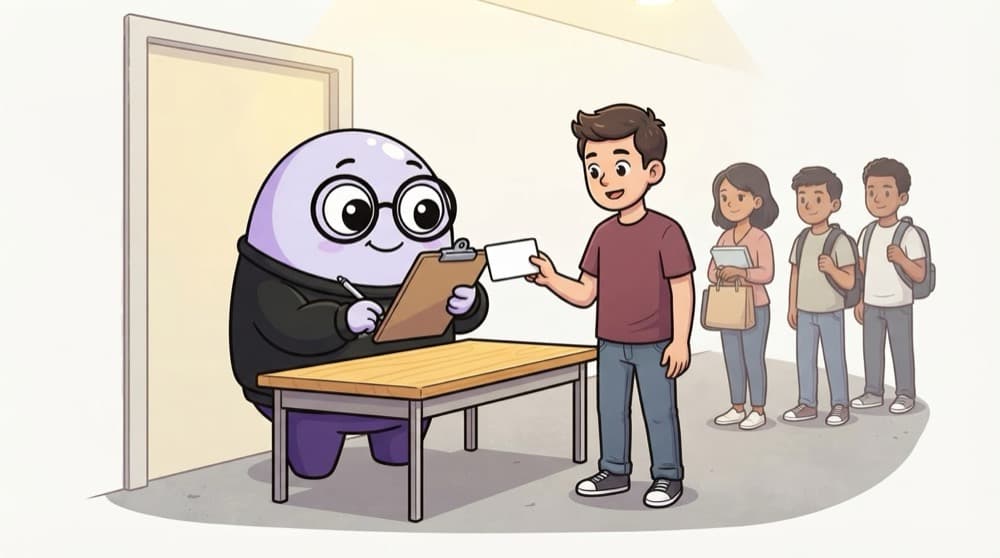
The exam hall invigilator at the door
The invigilator checks every student at the door: right hall, valid admit card, front door only. Anyone else is turned away, no discussion. A firewall checks every packet the same way: right port, allowed source, or it doesn't get in.
Watch it happen
Inbound rules, checked top to bottom
1/4SSH (port 22) is allowed only from your office or VPN IP, not the whole internet.
The big ideas
What you need to know
Default deny
Start by blocking everything, then open only what's needed. Never start open and try to close holes later.
Inbound and outbound
Inbound rules control who can reach you. Outbound rules control where your server can connect to.
Security groups are stateful
In AWS, if a request is allowed in, its reply is allowed out automatically. Network ACLs are stateless and need both directions.
Layers of defence
Use the cloud security group and a host firewall like ufw. If one is misconfigured, the other still protects you.
See it in code
Walk through the code
1sudo ufw default deny incoming2sudo ufw default allow outgoing3 4sudo ufw allow from 203.0.113.0/24 to any port 22 proto tcp5sudo ufw allow 80/tcp6sudo ufw allow 443/tcp7 8sudo ufw enable9sudo ufw status numbered1/3Block all incoming traffic by default, but let the server make outgoing connections.
Add the SSH rule before you run ufw enable on a remote server, or you'll lock yourself out.
Save yourself the pain
Common mistakes
Oops
Opening port 22 or the database port to 0.0.0.0/0 'just for testing'.
Do this instead
Open SSH only to your IP or a VPN, and keep databases private. Bots scan the whole internet for open ports.
Oops
Enabling a firewall over SSH before allowing port 22.
Do this instead
Always allow your SSH rule first. Many cloud consoles also offer a browser-based console if you get locked out.
Your mission
Lock down a VM
Quick check
Your app servers must reach the database, but users must not. How should the database's inbound rule look?
Go deeper
- 1Configure a security group allowing only necessary traffic to a resource.
- 2Learn the principle of least privilege applied to network access: deny by default, allow explicitly.
- 3Understand the difference between stateful security groups and stateless network ACLs.
More topics at this stop
 OSI & TCP/IP Models
 IP Addressing & Subnetting
 DNS
 HTTP/HTTPS & TLS
 Virtual Private Clouds (VPCs)
 Load Balancers
 CDNs (Content Delivery Networks)
 VPNs & Direct Connect / Interconnect

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
