
VPNs & Direct Connect / Interconnect
Part of the Cloud Computing Roadmap
In short
Plenty of companies keep some systems in their own office or data centre. To use the cloud safely, those systems need a private road into the VPC. You have two main ways to build it.
Secure connectivity options between your on-premise network and the cloud — a VPN tunnels traffic over the public internet, while Direct Connect/Interconnect provides a dedicated, more reliable private network link.
Think of it like this
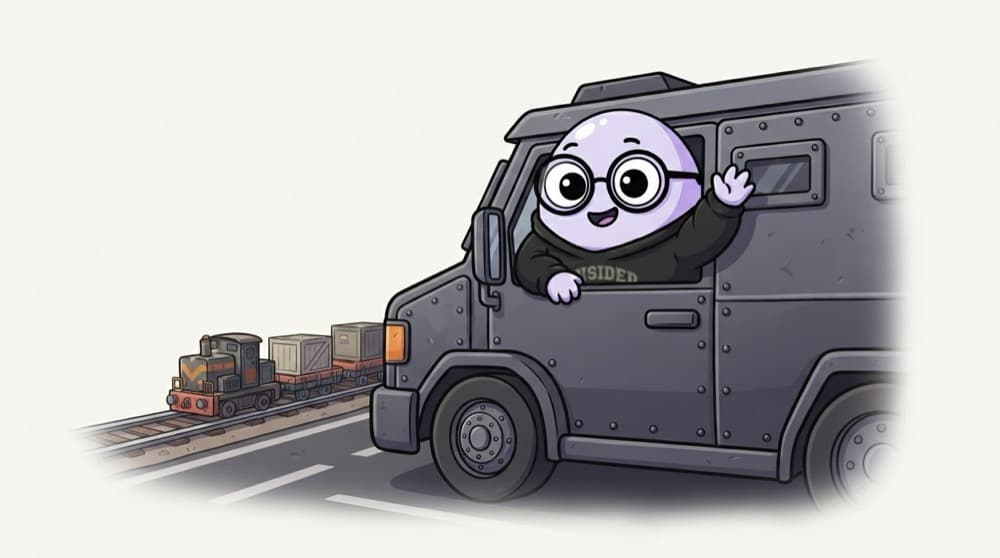
Armoured van vs private railway
An armoured van uses the public highway but nobody can open the cargo. That's a VPN. A private railway line from your factory to the port is Direct Connect: costly and slow to build, but nobody else is on that track.
Watch it happen
Two roads into your VPC
Site-to-site VPN
- Encrypted tunnel over the internet
- Set up in hours
- Speed varies with internet traffic
Direct Connect
- Dedicated physical link to the provider
- Takes weeks to set up
- Steady speed, lower latency
Start with a VPN. Add Direct Connect (Azure ExpressRoute, Google Cloud Interconnect) when traffic is heavy or steady performance matters. Many keep a VPN as backup.
The big ideas
What you need to know
VPN = encrypted tunnel
IPsec scrambles traffic between your office router and the cloud's VPN gateway, so the public internet can't read it.
Direct Connect = your own wire
A private fibre link from your data centre or a partner location straight into the provider's network.
Predictable performance
The internet's speed changes with traffic. A dedicated link gives steadier bandwidth and latency.
Plan for failure
Use two VPN tunnels or two links. If you have only one, a single cut cable takes your hybrid setup offline.
How it works
Setting up a site-to-site VPN on AWS
- 1
Gateway on the cloud side
Create a virtual private gateway (or transit gateway) and attach it to your VPC.
- 2
Describe your office
Create a customer gateway with your office router's public IP.
- 3
Create the connection
AWS gives you two tunnels and a config file for your router brand.
- 4
Route traffic
Add routes so VPC traffic for your office range goes through the VPN, then test with a ping.
Save yourself the pain
Common mistakes
Oops
Using the same IP range in the office and the VPC.
Do this instead
Ranges must not overlap, or routers can't tell which side an address belongs to. Plan ranges before connecting.
Oops
Thinking Direct Connect is encrypted by default.
Do this instead
It's private, not automatically encrypted. Sensitive traffic still needs TLS or a VPN running over the link.
Your mission
Design a hybrid link on paper
Quick check
A company moves terabytes daily between its data centre and AWS and needs steady latency. What fits best?
Go deeper
- 1Learn the basic concept of how a VPN tunnels traffic securely into a VPC.
- 2Understand why a dedicated connection (Direct Connect) is chosen over a VPN for latency-sensitive hybrid workloads.
- 3Compare the cost and reliability trade-offs between these two connectivity options.
More topics at this stop
 OSI & TCP/IP Models
 IP Addressing & Subnetting
 DNS
 HTTP/HTTPS & TLS
 Virtual Private Clouds (VPCs)
 Load Balancers
 Firewalls & Security Groups
 CDNs (Content Delivery Networks)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
