
Compliance Basics (SOC 2, ISO 27001)
Part of the Cloud Computing Roadmap
In short
The moment your startup tries to sell to a bank or a big company, someone asks: "Are you SOC 2 compliant?" Cloud engineers build most of the controls that answer yes.
Frameworks defining security and operational standards organizations must meet, often required to sell to enterprise customers — cloud engineers frequently implement the technical controls compliance requires.
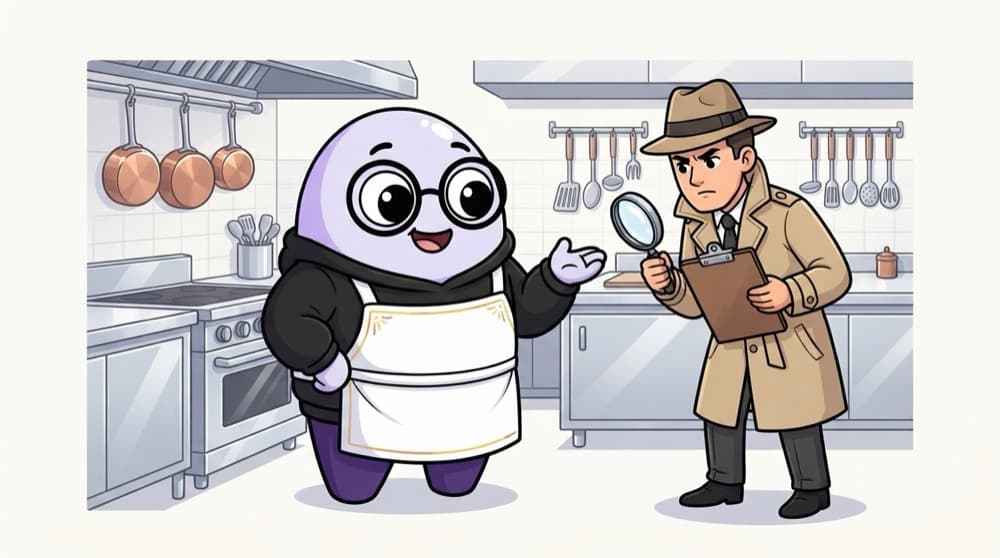
Think of it like this
The kitchen inspection
A food inspector doesn't taste one dish and leave. She checks fridge temperature logs, hairnets, pest control records and who cleans what. Compliance audits are the same: prove your habits, not one good day.
Watch it happen
How a company gets audited
1/5Pick which systems and teams are in scope, for example the production app and its AWS accounts.
The big ideas
What you need to know
SOC 2
An American attestation by a CPA firm on security and, optionally, availability, confidentiality and more. Type II covers a period of months.
ISO 27001
An international standard for running an information security management system, certified by an accredited body.
Shared responsibility
AWS's own certifications cover their data centres. How you configure your account is still on you.
Automate evidence
Config rules, Security Hub standards and tools like Vanta or Drata collect proof continuously instead of in a panic.
Save yourself the pain
Common mistakes
Oops
Saying "we're on AWS, so we're SOC 2 compliant".
Do this instead
AWS's report covers AWS. Your company needs its own audit of how you run your systems.
Oops
Treating compliance as a yearly scramble to fill a spreadsheet.
Do this instead
Build controls into daily work: MFA enforced, reviews in pull requests, logs kept by default.
Your mission
Map controls to your project
Quick check
What does a SOC 2 Type II report show that Type I does not?
Go deeper
- 1Read a high-level overview of what SOC 2 or ISO 27001 requires organizationally.
- 2Identify a technical control (like audit logging or encryption) that supports a specific compliance requirement.
- 3Understand why compliance often drives infrastructure decisions (like data residency) beyond pure technical preference.
More topics at this stop
 Identity & Access Management (IAM)
 Principle of Least Privilege
 Multi-Factor Authentication
 Roles vs Users vs Groups
 Encryption at Rest & in Transit
 Secrets Management
 Security Groups vs Network ACLs
 Cloud Security Posture Management
 Incident Response in the Cloud

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
