In short
Database passwords and API keys end up in GitHub more often than you'd think, and bots scan public repos constantly. A secrets manager keeps them out of your code entirely.
Storing credentials, API keys, and other sensitive values in a dedicated, access-controlled service rather than hardcoding them in configuration files or environment variables checked into version control.
Think of it like this
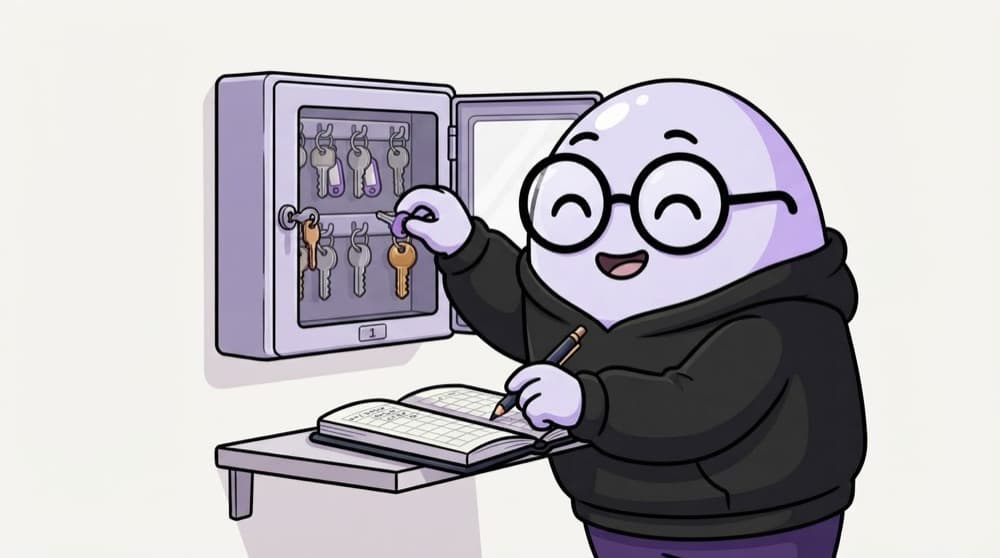
The society's key cabinet
Spare flat keys hang in a locked cabinet in the security cabin. The guard opens it only for listed residents and writes every key taken in a logbook. Nobody tapes keys under the doormat anymore.
Watch it happen
Fetching a password at runtime
GetSecretValue prod/db
1/5On startup the app asks for the secret by name. Its IAM role decides if it's allowed.
The big ideas
What you need to know
Never in Git
Not in code, not in committed .env files, not in Dockerfiles. Git history remembers even after you delete the line.
Access by role
Only the identity that needs a secret can read it, and every read is logged.
Rotation
Secrets that change on a schedule limit how long a leaked value stays useful.
Options
AWS Secrets Manager, SSM Parameter Store, GCP Secret Manager, Azure Key Vault and HashiCorp Vault all do this job.
See it in code
Walk through the code
1import json2import boto33 4client = boto3.client("secretsmanager", region_name="ap-south-1")5 6resp = client.get_secret_value(SecretId="prod/db")7creds = json.loads(resp["SecretString"])8 9conn_str = (10 f"postgresql://{creds['username']}:{creds['password']}"11 f"@{creds['host']}:5432/app"12)13# Never print or log conn_str1/3Credentials for this call come from the server's role, not a stored key.
The server's IAM role needs secretsmanager:GetSecretValue on just this one secret.
Save yourself the pain
Common mistakes
Oops
Deleting a committed API key in the next commit and moving on.
Do this instead
Treat it as leaked. Revoke and replace the key first, then clean history with a tool like git filter-repo.
Oops
Moving secrets to environment variables in the task definition, in plain text.
Do this instead
Reference the secret's ARN so the platform injects it at runtime from the secrets store.
Your mission
Catch a secret before it ships
Quick check
Why is storing a password in a secrets manager better than in a private repo?
Go deeper
- 1Store a sample secret in a managed secrets service and retrieve it programmatically.
- 2Learn why committing a secret to Git (even briefly) is a serious security incident, not a minor mistake.
- 3Understand secret rotation and why regularly changing credentials limits the damage of a leak.
More topics at this stop
 Identity & Access Management (IAM)
 Principle of Least Privilege
 Multi-Factor Authentication
 Roles vs Users vs Groups
 Encryption at Rest & in Transit
 Security Groups vs Network ACLs
 Compliance Basics (SOC 2, ISO 27001)
 Cloud Security Posture Management
 Incident Response in the Cloud

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
