Cryptographic Attacks
Part of the Cybersecurity Roadmap
In short
Strong maths rarely gets broken. Attackers go after weak choices and sloppy use instead. Knowing these patterns helps you pick safe settings and review code with sharp eyes.
Techniques for breaking or bypassing cryptographic protections — brute force, side-channel attacks, and exploiting weak implementations rather than the underlying math itself.
Think of it like this
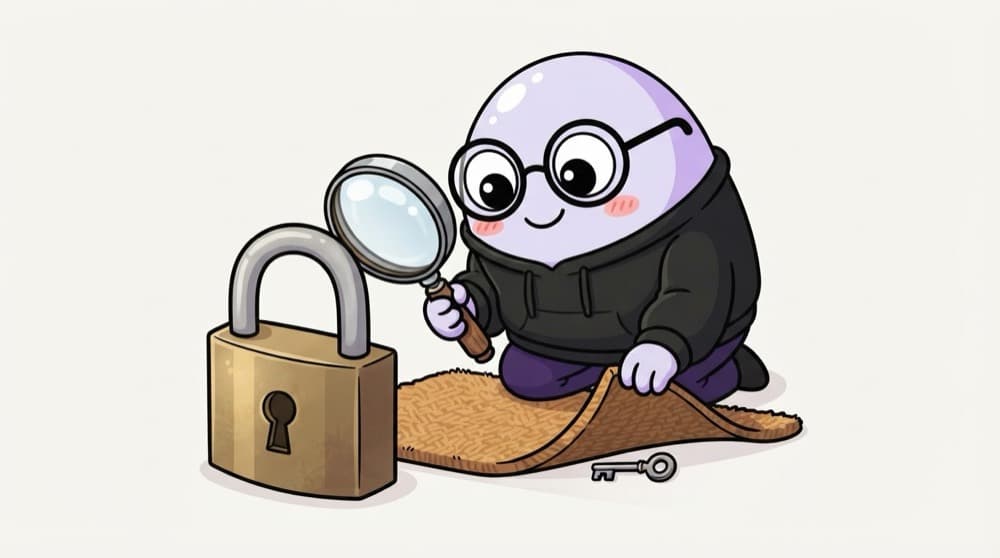
The unbreakable lock, the key under the mat
A family buys the toughest lock in the market, then hides the spare key under the doormat. A thief never touches the lock. Most crypto failures are like that: the algorithm is fine, but keys, settings or code around it are weak.
Watch it happen
Where crypto really fails
1/5Brute force: trying every key or password. Defence: long keys, slow password hashes, rate limits.
The big ideas
What you need to know
Make guessing slow
Password hashes like Argon2id are deliberately slow and salted, so a stolen database cannot be cracked quickly.
Constant time compare
Comparing secrets byte by byte with == can leak how many bytes matched through timing. Use a constant time function.
Watch for downgrades
If a system allows old protocol versions, a network attacker may push both sides to the weakest one. Turn old versions off.
Plan for quantum
NIST published post quantum standards in 2024. Large future quantum computers threaten RSA and ECC, so teams are planning migrations now.
See it in code
Walk through the code
1import hmac2from argon2 import PasswordHasher3 4ph = PasswordHasher() # Argon2id, salted, slow on purpose5stored = ph.hash("chai-at-4pm")6 7ph.verify(stored, "chai-at-4pm") # True, or raises on mismatch8 9def tokens_match(given: str, expected: str) -> bool:10 # constant time: no timing hint about how much matched11 return hmac.compare_digest(given, expected)1/3argon2-cffi adds a random salt and slow work factor automatically.
Two defensive habits in one file: store passwords with Argon2id, and compare secret tokens in constant time.
Save yourself the pain
Common mistakes
Oops
Using MD5 or SHA-1 for anything security related because it is "just a checksum".
Do this instead
Use SHA-256 or better for integrity, and a password hash for passwords. Collisions in MD5 and SHA-1 are practical.
Oops
Disabling certificate verification to fix a TLS error in code.
Do this instead
Fix the trust store or certificate. Turning verification off removes the protection TLS gives you.
Your mission
Review crypto in a lab app
Quick check
A login check compares tokens with a normal == string compare. Which risk does this create?
Go deeper
- 1Learn the difference between attacking a weak algorithm and attacking a weak implementation.
- 2Research a real-world side-channel attack (like a timing attack) at a conceptual level.
- 3Understand why most practical cryptographic attacks target implementation flaws, not the math.
More topics at this stop
 Cryptography Fundamentals Deep Dive
 Digital Signatures
 TLS/SSL Deep Dive
 Blockchain Security Basics
 IoT Security Basics
 AI & Security (Adversarial ML Overview)
 Emerging Threats Landscape

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
