Digital Signatures
Part of the Cybersecurity Roadmap
In short
How does your laptop know an update really came from the vendor and was not swapped on the way? Digital signatures prove who sent something and that nobody changed it.
Using asymmetric cryptography to prove a message's authenticity and integrity — the sender signs with their private key, and anyone can verify with the corresponding public key, without revealing the private key.
Think of it like this
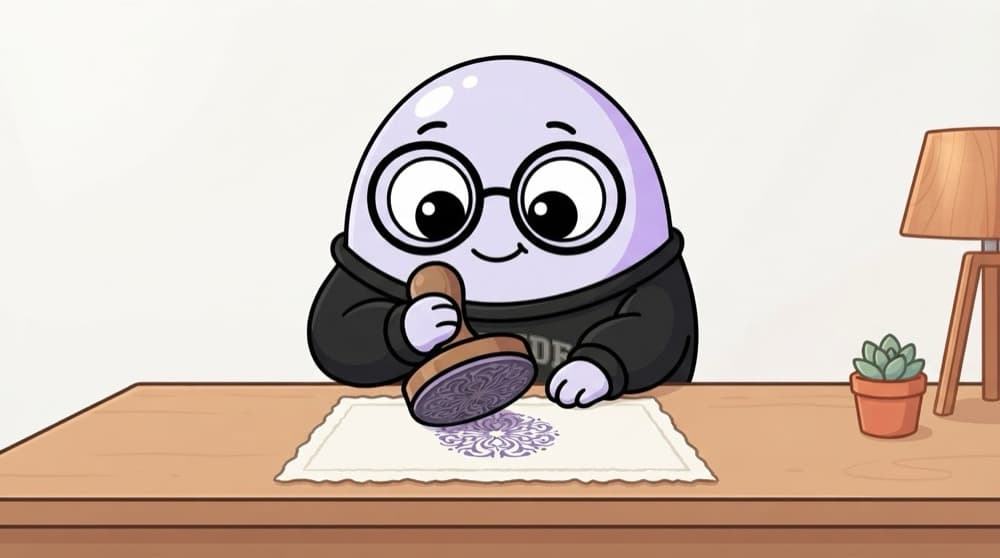
The principal's stamp and signature
A bonafide certificate carries the principal's signature and the college stamp. Anyone can compare it with the known specimen, but only the principal's office can produce it. If someone edits a mark, it no longer matches. A digital signature works like that, with maths instead of ink.
Watch it happen
Signing and verifying a release
1/5The developer hashes the release file to get a short fingerprint.
The big ideas
What you need to know
Private signs, public verifies
Only the private key holder can sign. Anyone with the public key can check. That is the reverse of encryption.
Integrity and origin
A valid signature proves the content was not changed and came from the key holder.
Trusting the public key
You must get the right public key. Certificates, signed by a trusted authority, bind a key to a name.
Guard the private key
If the signing key leaks, attackers can sign malware as you. Keep it in hardware or a managed key service.
See it in code
Walk through the code
1from cryptography.hazmat.primitives.asymmetric.ed25519 import Ed25519PrivateKey2from cryptography.exceptions import InvalidSignature3 4private_key = Ed25519PrivateKey.generate()5public_key = private_key.public_key()6 7sig = private_key.sign(b"Release v2.1 approved")8 9try:10 public_key.verify(sig, b"Release v2.9 approved")11except InvalidSignature:12 print("Tampered! Do not trust this.")1/3Generate a key pair. The public key can be shared with everyone.
One character changed in the message and verification fails. That is exactly how update systems reject modified files.
Save yourself the pain
Common mistakes
Oops
Thinking a signature hides the content.
Do this instead
Signatures prove authenticity and integrity, not secrecy. Encrypt separately if the content is private.
Oops
Accepting a public key sent in the same email as the file.
Do this instead
Get the public key from a trusted, separate source, or an attacker can swap both together.
Your mission
Verify a real download
Quick check
To verify a signed message from Priya, which key do you use?
Go deeper
- 1Diagram how a digital signature is created and verified using a public/private key pair.
- 2Learn the difference between encryption (confidentiality) and signing (authenticity/integrity).
- 3Understand where digital signatures are used in practice (code signing, document signing, certificates).
More topics at this stop
 Cryptography Fundamentals Deep Dive
 TLS/SSL Deep Dive
 Cryptographic Attacks
 Blockchain Security Basics
 IoT Security Basics
 AI & Security (Adversarial ML Overview)
 Emerging Threats Landscape

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
