In short
Every security control fails sometimes. Defence in depth stacks several independent layers, so an attacker who beats one still has to beat the next, and the next.
Layering multiple independent security controls so no single point of failure compromises the whole system — if one layer fails, another is there to catch the attack.
Think of it like this
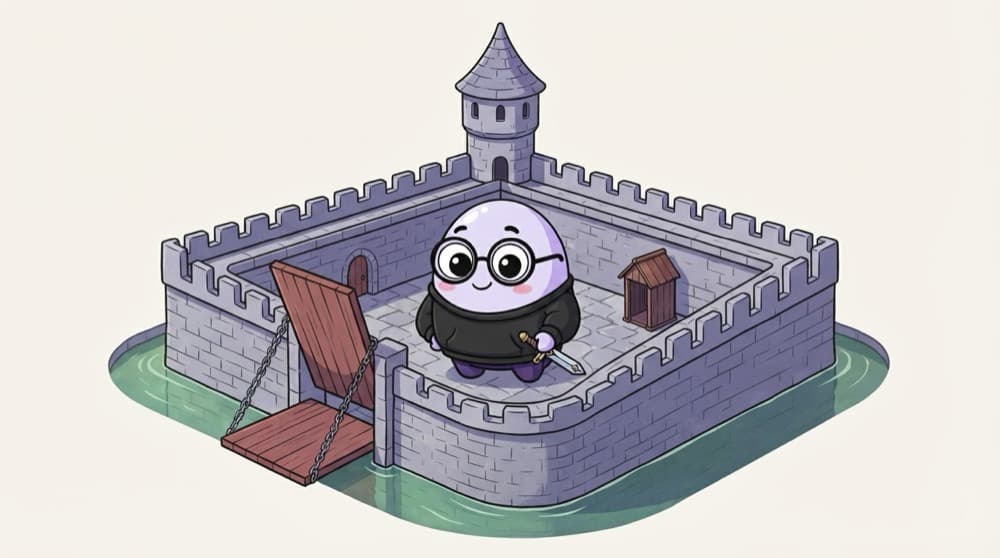
A hill fort
Old forts didn't rely on one wall. There was a moat, then a drawbridge, then thick walls, then guards on watchtowers, and finally the inner treasury. An invader crossing the moat still faced every other layer. That's defence in depth.
Watch it happen
One phishing email meets many layers
1/6The email filter catches most phishing, but this one slips through.
The big ideas
What you need to know
Layers must be independent
Two controls that fail for the same reason are really one layer. Mix people, process and technology.
Assume each layer fails
Ask, 'If this control is bypassed, what stops the attacker next?' for every critical system.
Detection is a layer too
Logging and monitoring don't block attacks, but they shorten how long attackers go unnoticed.
Balance cost and friction
Too many layers annoy users and get bypassed. Spend more layers on more valuable assets.
Save yourself the pain
Common mistakes
Oops
Relying on the perimeter firewall to protect everything.
Do this instead
Add controls inside too: MFA, endpoint protection, segmentation and backups.
Oops
Having backups that the same admin account can delete.
Do this instead
Keep at least one backup copy offline or immutable, so attackers with admin rights can't wipe it.
Your mission
Layer up your own laptop
Quick check
Ransomware encrypts a company's file server, but they recover in hours without paying. Which layer saved them?
Go deeper
- 1Diagram a defense-in-depth architecture for a hypothetical web application with at least 4 layers.
- 2Learn why relying on a single strong control (like just a firewall) is a common but risky mistake.
- 3Identify the layers present (or missing) in a real system you're familiar with.
More topics at this stop
 Authentication vs Authorization
 Encryption Basics (Symmetric vs Asymmetric)
 Hashing & Password Security
 Public Key Infrastructure (PKI)
 Multi-Factor Authentication
 Access Control Models (RBAC, ABAC)
 Zero Trust Architecture
 Security Policies & Standards
 The CVE & CVSS System

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
