Hashing & Password Security
Part of the Cybersecurity Roadmap
In short
Good apps never store your real password, not even the admins can see it. They store a hash. Do this wrong, and one database leak hands attackers every user's password.
Hashing turns data into a fixed-size, one-way fingerprint — used to store passwords without keeping the actual password, provided a proper algorithm (bcrypt, Argon2) and salting are used correctly.
Think of it like this
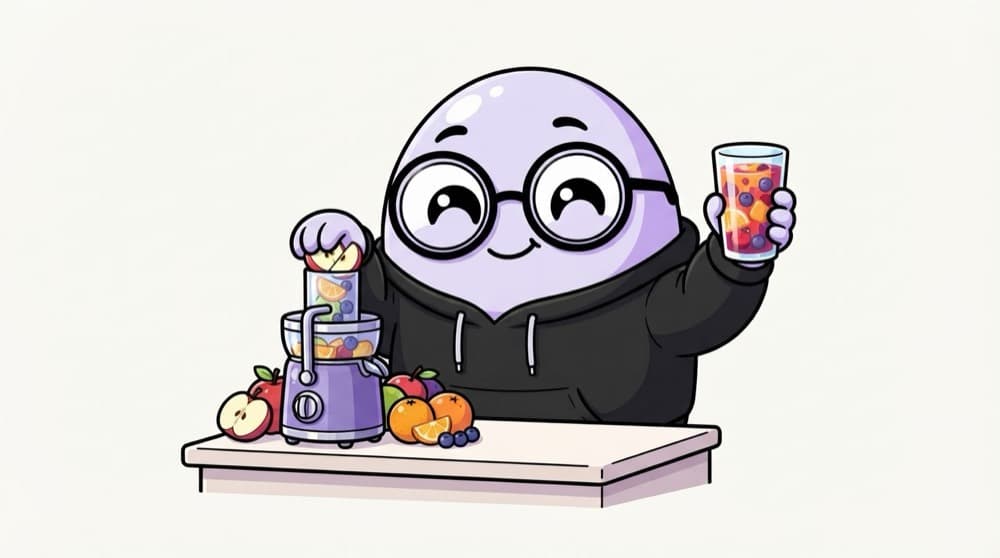
Fruit into juice
Put an apple, a banana and an orange into a juicer and you get one glass of mixed juice. You can check it's the same recipe by making it again, but nobody can turn the juice back into fruit. A hash is that juice: one way only.
Watch it happen
Storing and checking a password safely
1/5A user signs up with the password chai@123.
The big ideas
What you need to know
One way only
You can't reverse a hash. Attackers can only guess passwords and hash each guess to compare.
Salt every password
A unique random salt per user stops precomputed 'rainbow table' lookups and hides repeated passwords.
Slow is good here
SHA-256 is fast, which helps attackers. Use Argon2id, bcrypt or scrypt, built to be slow.
Hashes check integrity too
A file's SHA-256 changes if even one byte changes. That's how downloads are verified.
See it in code
Walk through the code
1import hashlib2import bcrypt # pip install bcrypt3 4# Fast hash: fine for checking files, wrong for passwords5print(hashlib.sha256(b"chai@123").hexdigest())6 7# Password hashing: salted and slow8stored = bcrypt.hashpw(b"chai@123", bcrypt.gensalt(rounds=12))9print(stored) # salt and hash are stored together10 11print(bcrypt.checkpw(b"chai@123", stored)) # True12print(bcrypt.checkpw(b"chai@124", stored)) # False1/3SHA-256 always gives the same output for the same input, and it's very fast to compute.
Run the bcrypt line twice and you'll get two different outputs for the same password. That's the salt doing its job.
Save yourself the pain
Common mistakes
Oops
Storing passwords with plain MD5 or SHA-256.
Do this instead
Use Argon2id, bcrypt or scrypt from a trusted library. Fast hashes are cracked quickly with GPUs.
Oops
Encrypting passwords so you can 'recover' them for users.
Do this instead
Never make passwords recoverable. Offer a reset link instead.
Your mission
Feel the speed difference
Quick check
Two users both pick the password 'india@2024'. With proper salting, what do their stored hashes look like?
Go deeper
- 1Learn why storing plaintext passwords is a critical vulnerability, and hashing solves it.
- 2Understand what 'salting' does and why it defeats precomputed rainbow table attacks.
- 3Research why older algorithms like MD5 and SHA-1 are no longer considered secure for passwords.
More topics at this stop
 Authentication vs Authorization
 Encryption Basics (Symmetric vs Asymmetric)
 Public Key Infrastructure (PKI)
 Multi-Factor Authentication
 Access Control Models (RBAC, ABAC)
 Zero Trust Architecture
 Security Policies & Standards
 Defense in Depth
 The CVE & CVSS System

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
