
Encryption Basics (Symmetric vs Asymmetric)
Part of the Cybersecurity Roadmap
In short
Encryption is how your UPI payment, WhatsApp chat and saved passwords stay unreadable to everyone else. There are two big families, and real systems use both together.
Symmetric encryption uses one shared key for both encrypting and decrypting (fast, but key distribution is hard); asymmetric uses a public/private key pair (slower, but solves the key distribution problem).
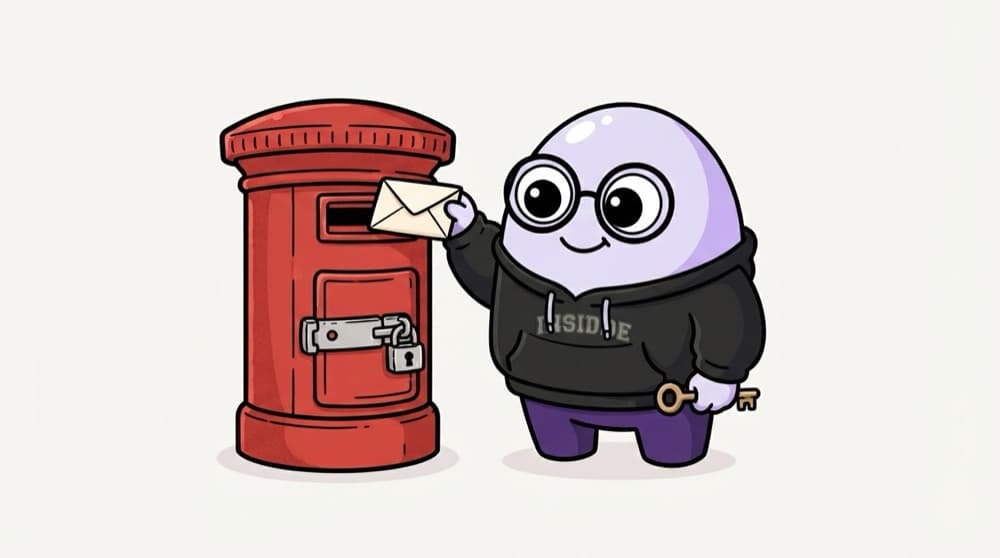
Think of it like this
A shared cupboard key vs a post box
You and your roommate share one cupboard key: fast and simple, but you had to hand it over safely first (symmetric). A post box has a slot anyone can drop letters into, but only the postman's key opens it (asymmetric). The slot is the public key.
Watch it happen
One key or a key pair?
Symmetric (AES)
- Same key locks and unlocks
- Very fast, good for big data
- Hard part: sharing the key safely
Asymmetric (RSA, ECC)
- Public key locks, private key unlocks
- Slower, used for small data
- Solves sharing: publish the public key
TLS uses both: asymmetric crypto to agree on a key safely, then fast symmetric AES for the actual data.
The big ideas
What you need to know
AES does the heavy lifting
Disk encryption, VPNs and HTTPS traffic all use symmetric ciphers like AES because they're fast.
Public keys can be shared
Anyone can encrypt to you with your public key. Only your private key can decrypt it.
Signatures flip it around
Sign with your private key, and anyone with your public key can verify it really came from you.
Never roll your own
Use well-tested libraries and standard algorithms. Home-made encryption is almost always broken.
See it in code
Walk through the code
1# Symmetric: one password-derived key for both directions2openssl enc -aes-256-cbc -pbkdf2 -salt -in notes.txt -out notes.enc3openssl enc -d -aes-256-cbc -pbkdf2 -in notes.enc -out notes.dec.txt4 5# Asymmetric: make a key pair6openssl genpkey -algorithm RSA -pkeyopt rsa_keygen_bits:3072 -out private.pem7openssl pkey -in private.pem -pubout -out public.pem8 9# Anyone with public.pem can encrypt; only private.pem can decrypt10openssl pkeyutl -encrypt -pubin -inkey public.pem -in msg.txt -out msg.enc11openssl pkeyutl -decrypt -inkey private.pem -in msg.enc1/3The same password unlocks what it locked. Lose it or share it badly and the scheme fails.
Try both in your terminal. Notice that the RSA step can only encrypt a small message. That's why real systems wrap a random AES key with RSA instead.
Save yourself the pain
Common mistakes
Oops
Calling base64 'encryption'.
Do this instead
Base64 is just encoding. Anyone can decode it instantly. It hides nothing.
Oops
Committing private keys to GitHub with the code.
Do this instead
Keep private keys in a secrets manager or a protected file, and add them to .gitignore.
Your mission
Send a secret to a friend
Quick check
Why does HTTPS use asymmetric encryption only at the start of a connection?
Go deeper
- 1Diagram how symmetric and asymmetric encryption each handle key exchange differently.
- 2Learn why real systems (like TLS) often use both together: asymmetric to exchange a symmetric key.
- 3Practice explaining the trade-off (speed vs key distribution) in plain language.
More topics at this stop
 Authentication vs Authorization
 Hashing & Password Security
 Public Key Infrastructure (PKI)
 Multi-Factor Authentication
 Access Control Models (RBAC, ABAC)
 Zero Trust Architecture
 Security Policies & Standards
 Defense in Depth
 The CVE & CVSS System

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
