Malware Analysis Basics
Part of the Cybersecurity Roadmap
In short
To defend against a suspicious file, you need to know what it does. Analysis answers that safely, by inspecting it instead of just trusting or deleting it.
Examining suspicious files to understand their behavior and impact — static analysis (examining the file without running it) and dynamic analysis (observing it run in an isolated sandbox) are the two main approaches.
Think of it like this
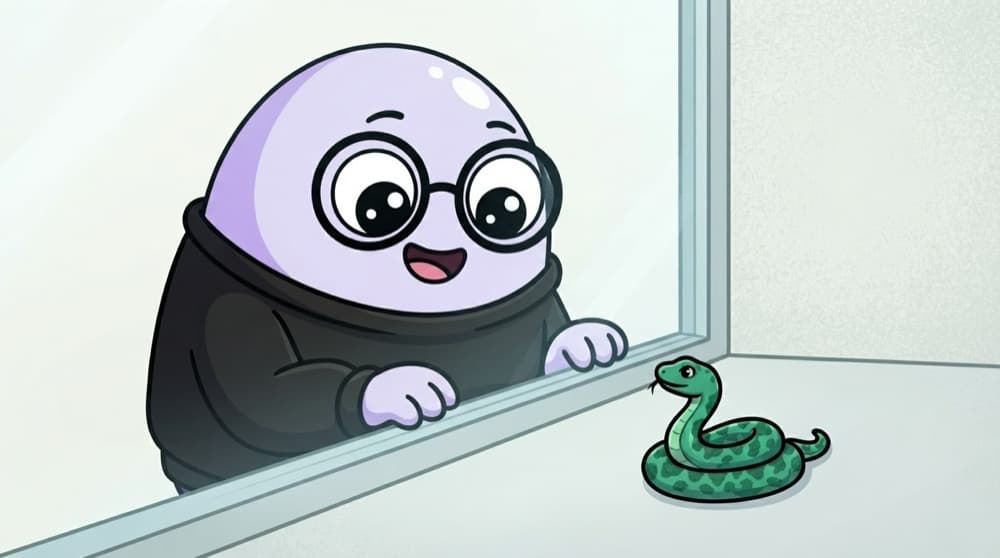
Studying a snake behind glass
A snake expert does not handle a venomous snake bare handed. They study it behind thick glass in a sealed room. Malware analysis is the same: you examine the sample inside a locked off sandbox, never on your real machine.
Watch it happen
Two ways to examine a sample
Static
- Inspect without running it
- Read strings and structure
- Safer, but can be hidden
Dynamic
- Run it in a sandbox
- Watch real behaviour
- Reveals what it actually does
Static analysis is safe reconnaissance; dynamic shows true behaviour but needs an isolated sandbox. Analysts use both, always away from real systems.
The big ideas
What you need to know
Static first
Look at the file without running it: its strings, type and structure. Low risk, quick clues.
Dynamic in a sandbox
Run it inside an isolated, disposable VM with no access to real data, and watch what it does.
Isolation is non-negotiable
Never run a sample on your real machine or network. A sandbox snapshot you can throw away keeps you safe.
Start with the hash
Before any analysis, hash the file and check free intel services. Someone may have already studied it.
Save yourself the pain
Common mistakes
Oops
Running a suspicious file on your own laptop to 'see what it does'.
Do this instead
Only run samples in an isolated, disposable sandbox VM with no path to real data or networks.
Oops
Trusting static analysis alone for a packed sample.
Do this instead
Malware often hides its strings. Pair static clues with dynamic sandbox behaviour to see the full picture.
Your mission
Safely inspect a benign sample
Quick check
Why must dynamic malware analysis happen in an isolated sandbox?
Go deeper
- 1Analyze a known-safe sample file using static analysis techniques (strings, hashes) in a lab.
- 2Learn why dynamic analysis must always happen in an isolated, disposable sandbox environment.
- 3Understand malware analysis as a specialized skill many security professionals only touch occasionally.
More topics at this stop
 Incident Response Lifecycle
 Incident Triage & Classification
 Containment, Eradication & Recovery
 Digital Forensics Fundamentals
 Chain of Custody
 Memory & Disk Forensics Basics
 Post-Incident Reporting
 Tabletop Exercises

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
