In short
Someone commits an AWS key again, or pushes YAML that doesn't even parse. Git hooks run checks automatically at commit time, so mistakes are caught before they leave your laptop.
Scripts that run automatically at specific points in the Git workflow (before a commit, before a push) — used to enforce standards like linting or preventing secrets from being committed.
Think of it like this
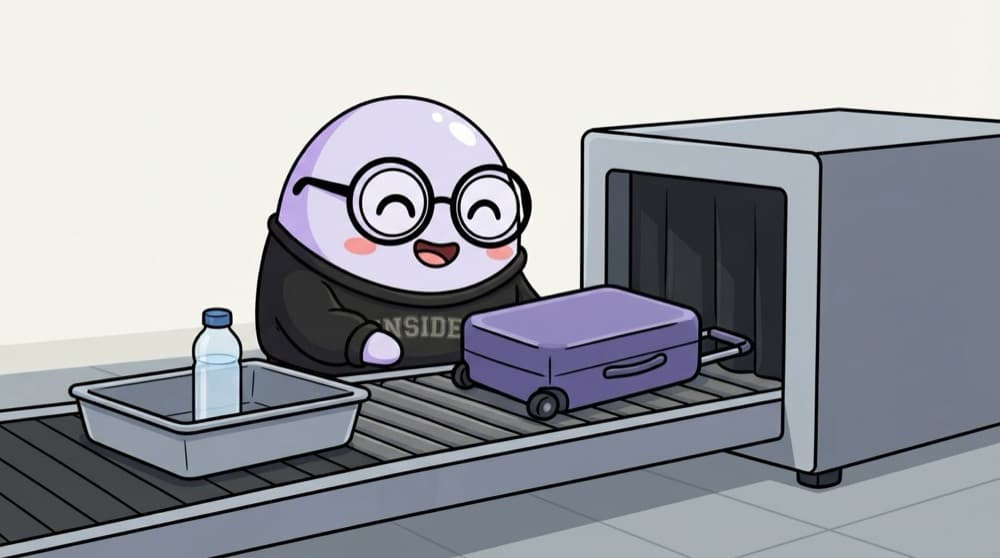
Airport security before boarding
Before you board, your bag goes through the scanner automatically. Carry a big bottle of water and it's stopped right there, not mid-flight. A pre-commit hook scans every commit the same way and stops it if something dangerous, like a password, is inside.
Watch it happen
What happens on git commit
1/4You run git commit. Before saving, Git looks in .git/hooks for scripts to run.
The big ideas
What you need to know
Hooks live in .git/hooks
They are plain scripts named after events, like pre-commit or pre-push. A non-zero exit code blocks the action.
Hooks aren't shared by default
.git/hooks isn't committed. Tools like the pre-commit framework or Husky let the whole team share them.
Catch secrets early
Secret scanners like gitleaks catch keys before they reach the remote, where they'd count as leaked.
CI is the real gate
Anyone can skip hooks with --no-verify. Run the same checks in CI so nothing gets through.
See it in code
Walk through the code
1# .pre-commit-config.yaml (shared via the repo)2repos:3 - repo: https://github.com/pre-commit/pre-commit-hooks4 rev: v5.0.05 hooks:6 - id: check-yaml7 - id: end-of-file-fixer8 - id: check-merge-conflict9 - repo: https://github.com/gitleaks/gitleaks10 rev: v8.21.211 hooks:12 - id: gitleaks1/3This file is committed, so every teammate gets the same hooks.
Run pip install pre-commit and pre-commit install once per clone. Check each project's releases for the latest rev before copying.
Save yourself the pain
Common mistakes
Oops
Writing a hook in .git/hooks and expecting teammates to have it too.
Do this instead
That folder isn't committed. Use a shared config like .pre-commit-config.yaml and document the install step.
Oops
Using --no-verify whenever a hook complains.
Do this instead
Fix what the hook found. If a hook is too slow or noisy, improve it rather than skipping it.
Your mission
Block a fake secret
Quick check
Why should secret scanning also run in CI, not just as a pre-commit hook?
Go deeper
- 1Set up a simple pre-commit hook that runs a check (e.g. a linter) before allowing a commit.
- 2Learn the difference between client-side hooks (local) and server-side hooks (on the remote).
- 3Explore a hook management tool (like pre-commit) that makes this easier to maintain across a team.
More topics at this stop
 Git Fundamentals
 Branching Strategies (Git Flow, Trunk-Based)
 Pull Requests & Code Review
 Merge Conflicts
 Monorepos vs Polyrepos (Overview)
 GitHub / GitLab Fundamentals
 Git for Infrastructure Code

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
