
Common Network Protocols (ARP, ICMP, DHCP)
Part of the Cybersecurity Roadmap
In short
These small protocols run quietly in the background of every network. Attackers abuse them because they were built for convenience, with almost no checks, so defenders need to know how they behave.
Lower-level protocols handling address resolution (ARP), diagnostics (ICMP), and automatic IP assignment (DHCP) — each has well-known attack techniques (ARP spoofing, ICMP tunneling) worth understanding.
Think of it like this
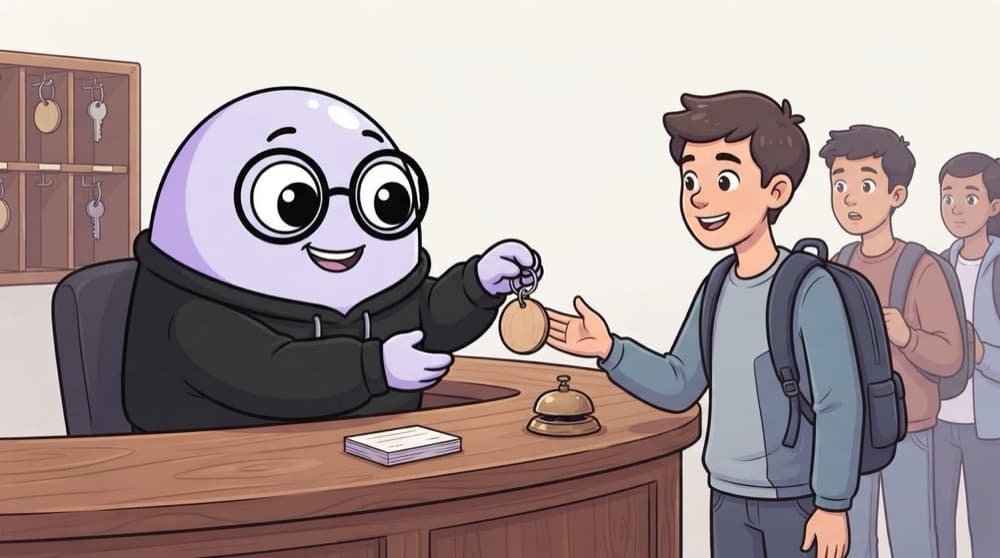
The hostel warden's desk
New students get a room number from the warden (DHCP). Someone shouts down the corridor 'Who's in room 204?' and that person answers (ARP). You knock on a door to see if anyone's home (ICMP ping). Nobody checks if the person answering is lying.
Watch it happen
A laptop joins Wi-Fi and finds the router
DHCP DISCOVER
1/5The laptop has no IP yet, so it broadcasts: is there a DHCP server here?
The big ideas
What you need to know
DHCP hands out addresses
A rogue DHCP server can give victims a fake gateway or DNS. Switches can block this with DHCP snooping.
ARP maps IP to MAC
ARP has no authentication. Spoofed replies let an attacker sit in the middle of local traffic.
ICMP is for diagnostics
Ping and traceroute use it. Attackers use it to map networks, and sometimes to hide data in pings.
All local, all trusting
These attacks need a foothold on the same network segment, which is another reason segmentation matters.
See it in code
Walk through the code
1# See your ARP table (IP to MAC mappings)2ip neigh # Linux3arp -a # Windows / macOS4 5# Watch ARP and DHCP traffic live on your lab network6sudo tcpdump -i eth0 -n arp or port 67 or port 681/2Each line pairs an IP with a MAC. Your gateway should always show the same MAC.
If your gateway's MAC address suddenly changes in the ARP table, something on the network may be spoofing it.
Save yourself the pain
Common mistakes
Oops
Blocking all ICMP 'for security'.
Do this instead
Some ICMP types are needed for networks to work properly. Filter carefully rather than blocking everything.
Oops
Assuming local network traffic is safe because it's internal.
Do this instead
ARP and DHCP attacks happen inside the LAN. Use switch protections like DHCP snooping and dynamic ARP inspection.
Your mission
Watch a device join the network
Quick check
Your gateway's MAC address in the ARP table now matches a classmate's laptop. What's likely going on?
Go deeper
- 1Learn what ARP spoofing is and why it enables man-in-the-middle attacks on a local network.
- 2Understand what ICMP is normally used for (like ping) and how it can be abused for tunneling.
- 3Research a basic DHCP starvation attack conceptually.
More topics at this stop
 OSI & TCP/IP Models
 IP Addressing & Subnetting
 DNS & DNS Security
 HTTP/HTTPS & TLS
 Firewalls
 VPNs
 Proxies & Reverse Proxies
 Network Segmentation
 Packet Analysis Basics (Wireshark)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
