Proxies & Reverse Proxies
Part of the Cybersecurity Roadmap
In short
Proxies sit in the middle of conversations, and that position is powerful. Companies use them to filter what staff visit and to shield their servers from the internet.
A proxy sits between a client and the internet (often used for filtering or anonymization); a reverse proxy sits in front of a server (used for load balancing and, notably, web application firewalls).
Think of it like this
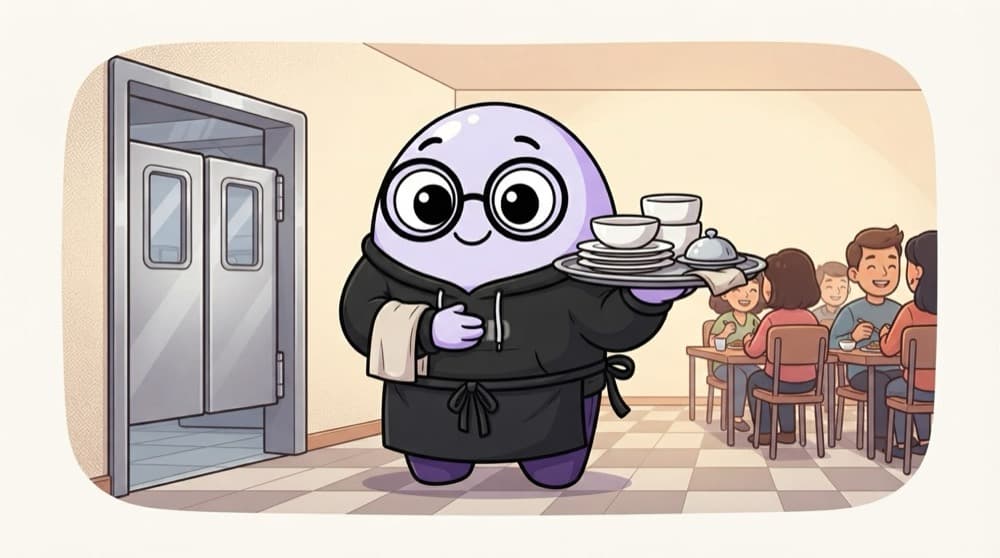
The restaurant waiter
Diners never walk into the kitchen. They tell the waiter, who passes orders in and brings food out. The kitchen stays hidden and safe. That waiter is a reverse proxy. A normal proxy is the opposite: a friend who buys tickets for you so the counter never sees you.
Watch it happen
Who does the middleman work for?
Forward proxy
- Sits in front of users
- Filters and logs outgoing browsing
- Websites see the proxy's IP
Reverse proxy
- Sits in front of servers
- Load balances, terminates TLS, adds a WAF
- Users never see the real server
A forward proxy protects and controls clients. A reverse proxy protects and scales servers. Many companies run both.
The big ideas
What you need to know
Forward proxies filter
Offices route web traffic through a proxy to block malware sites and keep logs of who visited what.
Reverse proxies shield
Nginx, HAProxy or a CDN sits in front, so attackers hit the proxy, not your app server directly.
WAFs live here
A web application firewall on the reverse proxy can block common attacks like SQL injection patterns.
Watch the real client IP
Behind a proxy, your app sees the proxy's IP. The original one arrives in the X-Forwarded-For header.
See it in code
Walk through the code
1# nginx reverse proxy: public port 443 -> private app on 30002server {3 listen 443 ssl;4 server_name shop.example.com;5 6 location / {7 proxy_pass http://127.0.0.1:3000;8 proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;9 }10}1/3nginx accepts HTTPS for one domain on the public port.
Only nginx faces the internet. The app listens on localhost, so nobody can reach it except through the proxy. (TLS certificate lines are left out to keep it short.)
Save yourself the pain
Common mistakes
Oops
Trusting X-Forwarded-For from anyone.
Do this instead
Clients can fake this header. Only trust it when it was set by your own proxy.
Oops
Leaving the app server reachable directly as well.
Do this instead
Bind the app to localhost or firewall it, so attackers can't skip the proxy and its protections.
Your mission
Put nginx in front of an app
Quick check
A company wants to log and filter which websites employees visit. Which do they need?
Go deeper
- 1Learn the difference between a forward proxy and a reverse proxy.
- 2Understand how a Web Application Firewall (a type of reverse proxy) filters malicious traffic.
- 3Research why attackers sometimes use proxy chains to obscure their origin.
More topics at this stop
 OSI & TCP/IP Models
 IP Addressing & Subnetting
 DNS & DNS Security
 HTTP/HTTPS & TLS
 Firewalls
 VPNs
 Network Segmentation
 Common Network Protocols (ARP, ICMP, DHCP)
 Packet Analysis Basics (Wireshark)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
