Firewalls
Part of the Cybersecurity Roadmap
In short
A firewall decides which traffic gets in and out, rule by rule. Most networks are only as safe as their firewall rules, and messy rules are one of the most common gaps auditors find.
A security control filtering network traffic based on defined rules — from simple packet-filtering firewalls to modern next-generation firewalls that inspect traffic more deeply.
Think of it like this
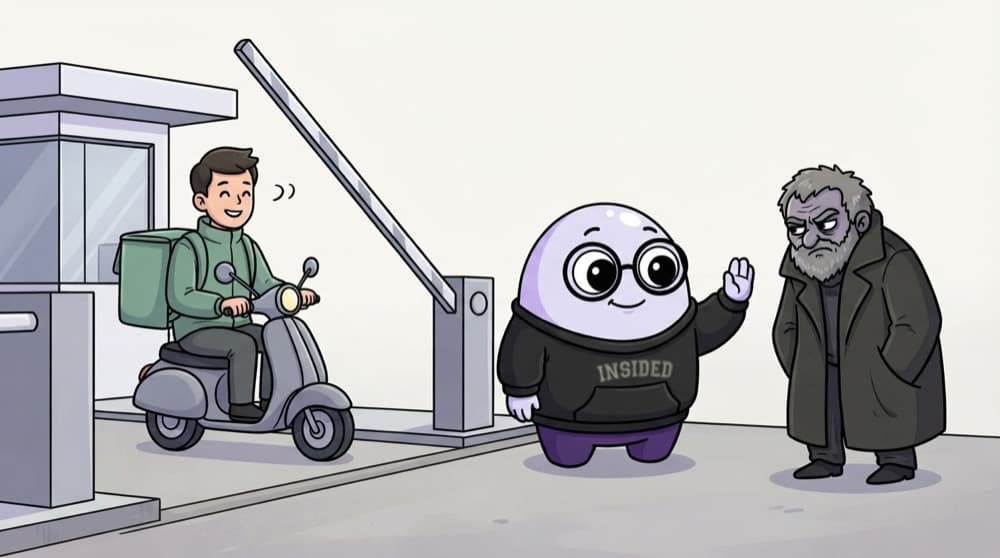
The society gate guard
The guard has a list: residents in, delivery riders to the lobby only, strangers stopped. He checks every visitor against the list from top to bottom and acts on the first match. A firewall reads its rules the same way.
Watch it happen
Rules are checked top to bottom, first match wins
1/7A packet arrives for port 443 (HTTPS). The firewall starts at rule 1.
The big ideas
What you need to know
Order matters
An early broad 'allow any' rule makes every rule below it useless. Put specific rules first.
Default deny
Allow only what's needed and block everything else. The opposite approach always leaves something open.
Stateful tracking
Modern firewalls remember connections, so replies to your outgoing requests come back without extra rules.
Next-gen firewalls
NGFWs look inside traffic to identify apps and threats, not just ports and IPs.
See it in code
Walk through the code
1# Ubuntu's simple firewall (run on your own VM)2sudo ufw default deny incoming3sudo ufw default allow outgoing4sudo ufw allow 443/tcp5sudo ufw allow from 10.0.0.0/24 to any port 22 proto tcp6sudo ufw enable7sudo ufw status numbered1/3Default deny for incoming traffic, allow for outgoing. Specific rules then punch small holes.
This is a sane starting point for a web server: HTTPS for everyone, SSH only from the internal network, everything else blocked.
Save yourself the pain
Common mistakes
Oops
Adding 'allow any any' to quickly fix a broken app.
Do this instead
Find the exact port and source the app needs and allow only that. Temporary rules tend to stay forever.
Oops
Running ufw enable over SSH before allowing port 22.
Do this instead
Allow your SSH access first, or you'll lock yourself out of a remote server.
Your mission
Lock down a lab VM
Quick check
A firewall's first rule is 'allow all from any'. Rule 5 is 'deny port 3389'. Is port 3389 blocked?
Go deeper
- 1Configure a basic firewall rule set allowing only necessary traffic on a practice VM.
- 2Learn the principle of least privilege applied to network access: deny by default, allow explicitly.
- 3Understand the difference between a stateless and a stateful firewall.
More topics at this stop
 OSI & TCP/IP Models
 IP Addressing & Subnetting
 DNS & DNS Security
 HTTP/HTTPS & TLS
 VPNs
 Proxies & Reverse Proxies
 Network Segmentation
 Common Network Protocols (ARP, ICMP, DHCP)
 Packet Analysis Basics (Wireshark)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
