DNS & DNS Security
Part of the Cybersecurity Roadmap
In short
Before almost every connection, your device asks DNS for an address. If an attacker can tamper with that answer, they can send you to a fake site without touching your browser at all.
The Domain Name System translates domain names into IP addresses — and is also a common attack surface, via DNS spoofing, cache poisoning, and DNS tunneling used to exfiltrate data covertly.
Think of it like this
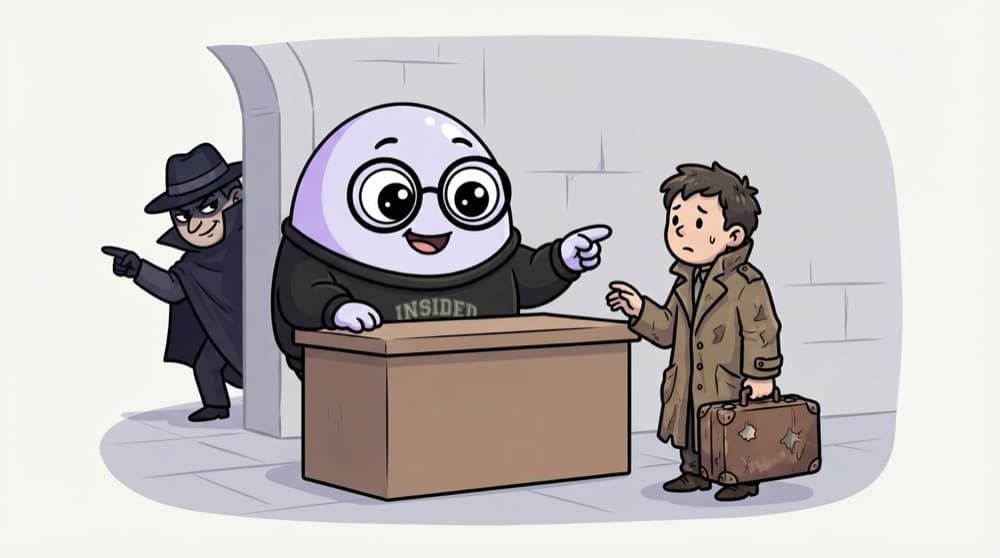
The railway enquiry counter
You ask the enquiry counter which platform your train is on and trust the answer. If a tout stands nearby shouting a wrong platform, you could miss your train. DNS is the counter, and DNS attacks are the tout.
Watch it happen
A normal lookup, and a poisoned one
A? mybank.in
1/5Your laptop asks the resolver for the IP address of mybank.in.
The big ideas
What you need to know
DNSSEC signs answers
Records are digitally signed, so a resolver that checks can reject forged replies.
DoH and DoT hide queries
DNS over HTTPS or TLS encrypts lookups, so people on your Wi-Fi can't read or change them easily.
DNS is a detection goldmine
Malware has to look up its servers. Odd domains or huge query volumes in DNS logs are strong clues.
Tunnelling smuggles data
Attackers can hide stolen data inside long DNS queries. Very long random subdomains are a red flag.
See it in code
Walk through the code
1# Ask for a domain's A record (IPv4 address)2dig example.com A +short3 4# Ask a specific resolver, like Cloudflare's5dig @1.1.1.1 example.com A +short6 7# Check if a domain is DNSSEC signed8dig example.com +dnssec | grep -i rrsig1/3dig asks your default resolver. +short prints just the answer.
If two resolvers give different answers for the same domain, find out why. An RRSIG record means the domain's answers are signed.
Save yourself the pain
Common mistakes
Oops
Ignoring DNS logs because 'it's just lookups'.
Do this instead
DNS logs show which domains every machine contacts. They catch malware callbacks that other logs miss.
Oops
Thinking HTTPS makes DNS attacks harmless.
Do this instead
HTTPS helps a lot, but users click through certificate warnings, and plain HTTP sites have no protection.
Your mission
Spot the odd lookup
Quick check
A laptop makes thousands of DNS queries like a8f3k2...x9.evil-domain.com every minute. What is the likely cause?
Go deeper
- 1Run dig or nslookup on a domain to see DNS resolution in action.
- 2Learn what DNS spoofing/cache poisoning is and why it's a serious trust attack.
- 3Understand why DNS tunneling is a technique attackers use to bypass network monitoring.
More topics at this stop
 OSI & TCP/IP Models
 IP Addressing & Subnetting
 HTTP/HTTPS & TLS
 Firewalls
 VPNs
 Proxies & Reverse Proxies
 Network Segmentation
 Common Network Protocols (ARP, ICMP, DHCP)
 Packet Analysis Basics (Wireshark)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
