
Penetration Testing Overview for QA
Part of the QA Testing Roadmap
In short
Penetration testers are hired to attack a system, with written permission, before real attackers do. You won't run full pentests as a QA, but knowing how they work makes you a better partner to them.
A conceptual understanding of what dedicated penetration testing involves — QA doesn't typically perform full pentests, but benefits from understanding how a specialized security team's work complements standard QA.
Think of it like this
The bank's permitted break-in
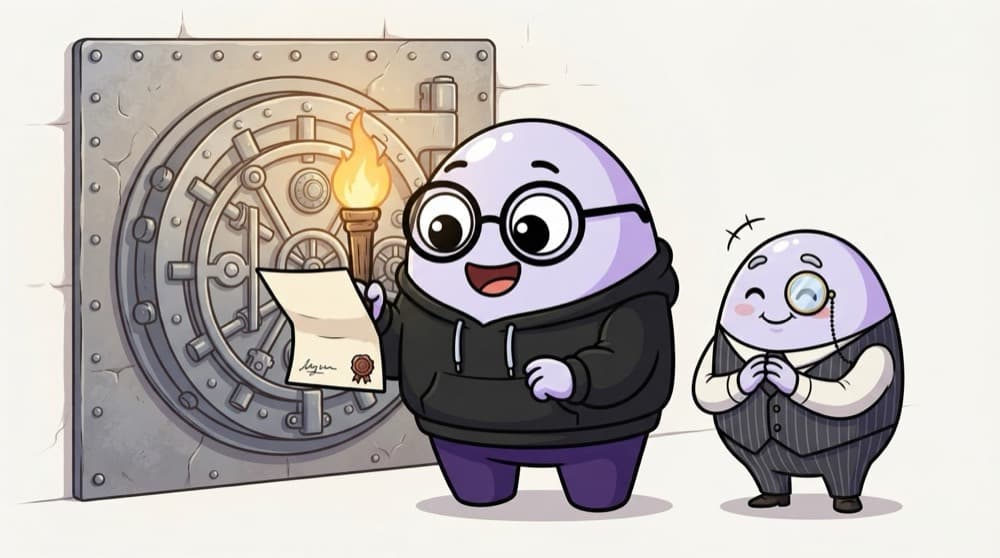
A bank hires a security expert, gives a signed letter saying 'try to get into the vault', and sets clear rules. The expert reports every weak spot. Without that letter, the same act is a crime. Pentesting works the same way.
Watch it happen
How an authorised pentest runs
1/6A written agreement says what's in scope, what's off limits, the dates, and who to call if something breaks.
The big ideas
What you need to know
Permission is everything
A pentest is legal because of a signed scope. The same actions without permission can be a crime.
QA vs pentest
QA checks the app works as intended. Pentesters check how it could be misused. Both are needed.
Turn findings into tests
Each fixed finding should become a regression test, so the hole never quietly reopens.
Practise in labs
Deliberately vulnerable apps like OWASP Juice Shop let you learn safely on your own machine.
Save yourself the pain
Common mistakes
Oops
Thinking a pentest once a year means the app is secure.
Do this instead
A pentest is a snapshot. New code ships every week, so security checks need to be part of normal testing too.
Oops
Running scanning tools against a company system because you're curious.
Do this instead
Only test inside an agreed scope. Ask your security team first, every time.
Your mission
Explore a practice lab
Quick check
What makes a penetration test legal and different from an attack?
Go deeper
- 1Read a conceptual overview of penetration testing methodology.
- 2Learn where QA testing and penetration testing overlap and where they diverge in scope.
- 3Understand when a QA team should escalate a suspected security issue to a dedicated security team.
More topics at this stop
 Security Testing Basics
 OWASP Top 10 for Testers
 Accessibility Testing (WCAG Basics)
 Automated Accessibility Testing Tools
 Vulnerability Scanning Basics
 Compliance Testing Overview

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
