
Compliance Basics (SOC 2, ISO 27001 Overview)
Part of the DevOps Roadmap
In short
Big companies won't buy from a startup until it proves their data is safe. SOC 2 and ISO 27001 are the proofs they ask for most, and DevOps builds much of the evidence.
Frameworks defining security and operational standards organizations must meet, often required to sell to enterprise customers — DevOps engineers frequently implement the technical controls compliance requires.
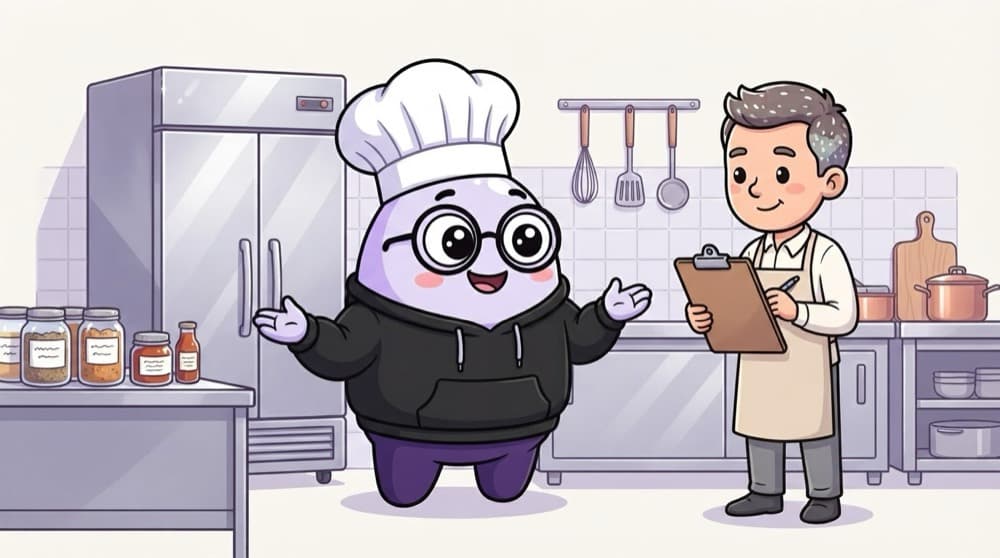
Think of it like this
The restaurant kitchen inspection
A food inspector doesn't taste every dish. They check the fridge temperature log, the cleaning schedule and the staff hygiene records. If records are kept and match reality, you pass. Compliance audits are like that: show your controls exist and that you follow them.
Watch it happen
SOC 2 vs ISO 27001 at a glance
SOC 2
- US-origin, from the AICPA
- Auditor's report on your controls
- Type II checks controls over months
ISO 27001
- International standard
- Certifies your security management system
- Certificate with yearly surveillance audits
Both ask similar things: access control, change management, logging, backups, incident response. Many companies pick based on where their customers are.
The big ideas
What you need to know
Controls are promises
A control is a rule you commit to, like 'every production change is reviewed' or 'access is removed within a day of leaving'.
Evidence proves them
Auditors ask for proof: pull request approvals, access review records, backup test logs. No proof means the control failed.
Pipelines make evidence
Required reviews, CI logs and Terraform history give you automatic, timestamped proof of change management.
It's continuous
Passing once isn't the end. SOC 2 Type II and ISO surveillance audits check you kept doing it over time.
How it works
A first compliance project
- 1
Pick the scope
Decide which systems and teams are covered, usually the product and its production cloud account.
- 2
Gap check
Compare what you do today against the framework's controls and list what's missing.
- 3
Fix and automate
Turn on MFA, branch protection, logging and backups. Automate evidence wherever you can.
- 4
Audit
An independent auditor reviews your evidence and either issues the report or certificate, or lists findings.
Save yourself the pain
Common mistakes
Oops
Thinking a compliance certificate means the company can't be hacked.
Do this instead
It means agreed controls exist and are followed. It lowers risk and builds trust, but it isn't a guarantee.
Oops
Collecting evidence by hand in screenshots the week before the audit.
Do this instead
Let the tools record it: protected branches, CI logs, ticket history, access review exports. Less stress, better proof.
Your mission
Map your own repo to controls
Quick check
An auditor asks how you know every production change was reviewed. What's the strongest answer?
Go deeper
- 1Read a high-level overview of what SOC 2 or ISO 27001 requires organizationally.
- 2Identify a technical control (like audit logging) that supports a specific compliance requirement.
- 3Understand why compliance often drives infrastructure decisions (like data residency) beyond pure technical preference.
More topics at this stop
 DevSecOps Principles ('Shift Left')
 Secrets Management (Vault, AWS Secrets Manager)
 Container & Image Scanning
 IAM & Least Privilege
 Network Security Basics
 Vulnerability Scanning in CI/CD
 Security Incident Response
 Zero Trust Architecture (Overview)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
