Zero Trust Architecture (Overview)
Part of the DevOps Roadmap
In short
The old idea was: once you're inside the office network, you're trusted. Then laptops went home and attackers learnt to get inside. Zero trust checks every request, every time, from everywhere.
A security model assuming no user or system should be trusted by default, even inside the network perimeter — every request is verified regardless of where it originates, replacing the older 'trusted internal network' assumption.
Think of it like this
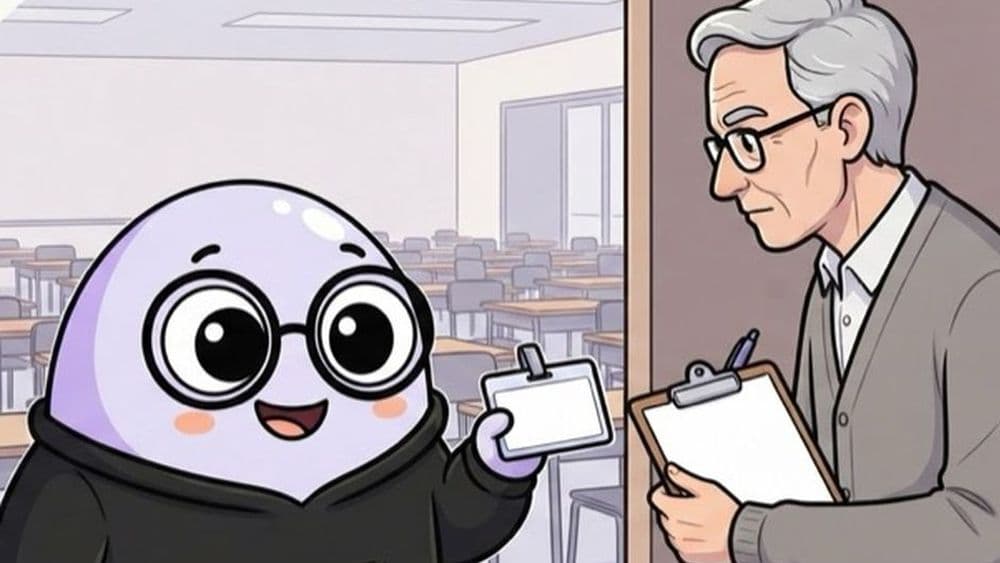
ID check at every exam hall
Getting through the college gate doesn't let you write any exam you like. The invigilator at each hall checks your ID card and hall ticket, for that subject, that day. Zero trust works the same way: passing one gate earns you nothing at the next.
Watch it happen
Opening an internal dashboard, zero trust style
GET /grafana
1/6No VPN. Your browser goes straight to an access proxy that sits in front of the internal app.
The big ideas
What you need to know
No trusted zone
Being on the office Wi-Fi or inside the VPC gives you nothing by itself. Location is not identity.
Verify identity and device
Every request needs a strong login, usually with MFA, and often a check that the device is healthy.
Least access, per app
You get access to the specific apps your role needs, not a network tunnel to everything.
Services verify each other
Inside the system, services prove identity to each other too, often with mutual TLS in a service mesh.
How it works
Moving a team toward zero trust
- 1
Single sign-on everywhere
Put every internal tool behind one identity provider with MFA turned on.
- 2
Inventory devices
Know which laptops are company-managed so policies can check them.
- 3
Replace the flat VPN
Put an identity-aware proxy in front of each internal app instead of one tunnel into everything.
- 4
Service identity
Give each service its own identity and encrypt service-to-service traffic with mutual TLS.
Save yourself the pain
Common mistakes
Oops
Buying one product labelled 'zero trust' and calling the job done.
Do this instead
Zero trust is a way of designing access: identity, device checks, least privilege and logging, rolled out step by step.
Oops
Thinking zero trust means trusting your own team less as people.
Do this instead
It's about not trusting network location. Your colleagues still get easy access, just verified on every request.
Your mission
Spot the implicit trust
Quick check
In a zero trust setup, an attacker gets onto the office Wi-Fi. What can they reach?
Go deeper
- 1Learn the core zero trust principle: 'never trust, always verify'.
- 2Compare zero trust to the traditional perimeter-based security model it's replacing.
- 3Understand why zero trust has become more relevant as remote work and cloud infrastructure blur network boundaries.
More topics at this stop
 DevSecOps Principles ('Shift Left')
 Secrets Management (Vault, AWS Secrets Manager)
 Container & Image Scanning
 IAM & Least Privilege
 Network Security Basics
 Compliance Basics (SOC 2, ISO 27001 Overview)
 Vulnerability Scanning in CI/CD
 Security Incident Response

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
