DevSecOps Principles ('Shift Left')
Part of the DevOps Roadmap
In short
A security bug found while you're typing costs you five minutes. The same bug found by a customer costs a weekend, an apology email and maybe a fine. Shift left means finding it early.
Integrating security checks earlier in the development lifecycle (during coding and CI, not just before production release) — 'shifting left' catches vulnerabilities when they're cheap to fix, not after they're deployed.
Think of it like this
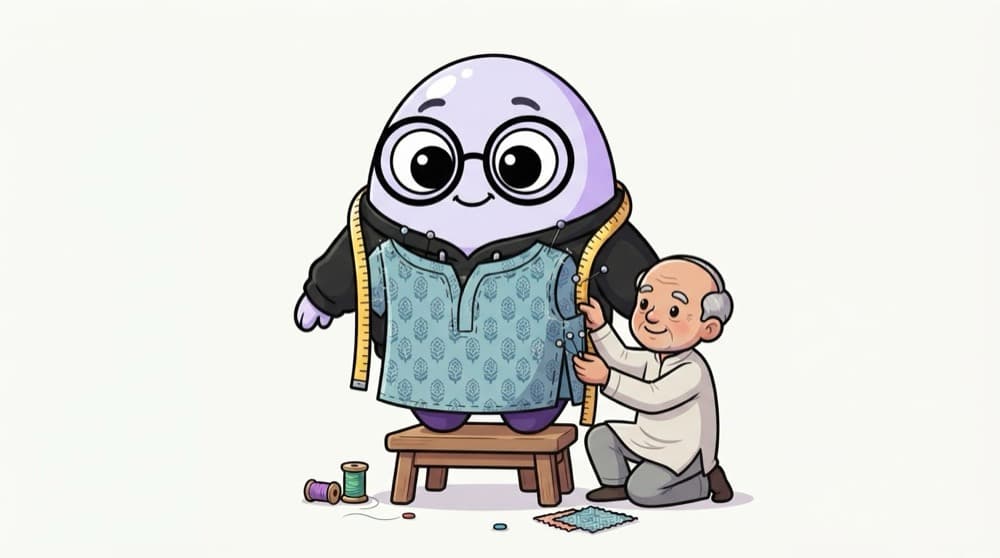
The tailor's trial fitting
A good tailor calls you for a trial when the kurta is only pinned together. A loose shoulder is fixed with two pins. Find it after the final stitching and the whole piece must be opened up. Security checks are trial fittings for your code.
Watch it happen
Security checks along the way
1/5A pre-commit hook and an editor plugin catch a hardcoded password before it ever leaves your laptop.
The big ideas
What you need to know
Earlier is cheaper
A fix during coding touches one file. The same fix after release needs a hotfix, a redeploy and maybe telling customers.
Everyone owns security
Developers, ops and security people share the work. The security team builds guardrails instead of acting as a last-minute gate.
Automate the boring checks
Machines are good at scanning every commit. Humans are good at threat thinking and reviews. Use each for what it's good at.
Keep it fast
If checks take 40 minutes or cry wolf all day, people will skip them. Fast, accurate checks are the ones that survive.
See it in code
Walk through the code
1# .pre-commit-config.yaml2# Runs on your laptop before every git commit3repos:4 - repo: https://github.com/gitleaks/gitleaks5 rev: v8.18.46 hooks:7 - id: gitleaks # blocks commits containing secrets8 - repo: https://github.com/pre-commit/pre-commit-hooks9 rev: v4.6.010 hooks:11 - id: detect-private-key12 - id: check-added-large-files1/3This file lives in your repo, so every teammate gets the same checks after running pre-commit install.
Install with pip install pre-commit, then run pre-commit install once in the repo. Pin rev to the latest release tag you find on each project's page.
Save yourself the pain
Common mistakes
Oops
Running one big security scan a week before release and dumping 300 findings on the team.
Do this instead
Run small checks on every commit and pull request, so each person fixes a few issues in code they just wrote.
Oops
Making every scanner block the build from day one, including low-severity noise.
Do this instead
Start by blocking only critical, fixable issues. Report the rest, tune false positives, then tighten the rules slowly.
Your mission
Catch a fake secret on your laptop
Quick check
What does 'shift left' actually change in a team's process?
Go deeper
- 1Diagram a traditional 'security review at the end' process versus a shift-left approach.
- 2Learn why fixing a vulnerability in code review is far cheaper than fixing it in production.
- 3Identify one security check from this phase that could be added directly into a CI pipeline (Phase 6).
More topics at this stop
 Secrets Management (Vault, AWS Secrets Manager)
 Container & Image Scanning
 IAM & Least Privilege
 Network Security Basics
 Compliance Basics (SOC 2, ISO 27001 Overview)
 Vulnerability Scanning in CI/CD
 Security Incident Response
 Zero Trust Architecture (Overview)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
