In short
Most cloud disasters aren't clever hacks. They're one leaked key that had admin rights. Least privilege makes sure a stolen key can only open one small door.
Identity and Access Management controls who can do what in a system — the principle of least privilege means granting only the minimum permissions needed, never broad access 'just in case'.
Think of it like this
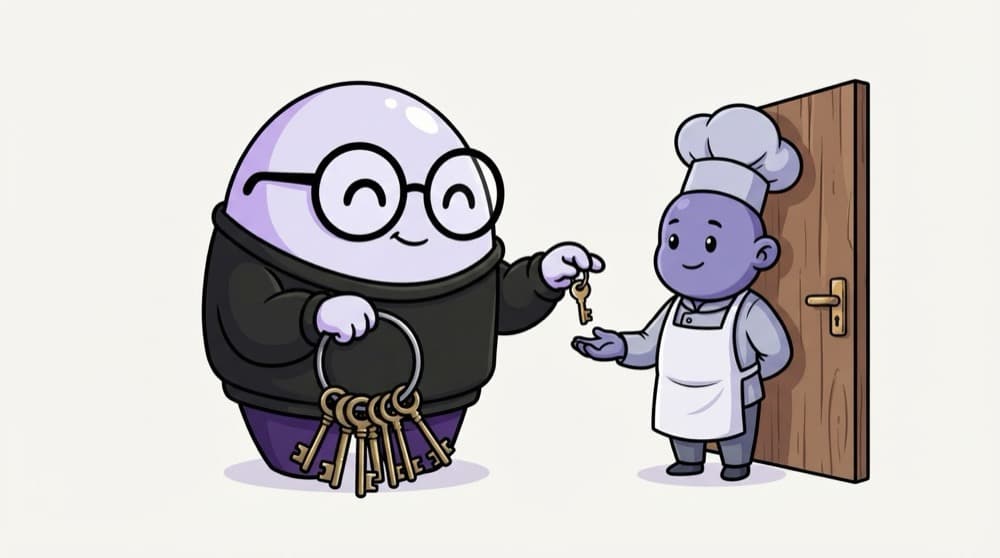
The hostel warden's key ring
The warden holds keys to every room. The mess cook gets one key: the kitchen store. Not the office, not the hostel rooms. If the cook loses it, only rice and dal are at risk. IAM is deciding who gets which key.
Watch it happen
How one request gets checked
PutObject invoices/42
1/6The orders app, running with its own role, tries to upload an invoice file.
The big ideas
What you need to know
Identity first
Every person and every app gets its own identity. Shared logins make it impossible to know who did what.
Policies list allowed actions
A policy says which actions on which resources are allowed. Everything else is denied by default.
Roles beat long-lived keys
Apps should assume a role and get temporary credentials, not carry a permanent access key that can leak.
Review and trim
Permissions grow over time. Cloud tools can show which permissions were never used, so you can remove them.
See it in code
Walk through the code
1{2 "Version": "2012-10-17",3 "Statement": [4 {5 "Effect": "Allow",6 "Action": ["s3:GetObject", "s3:PutObject"],7 "Resource": "arn:aws:s3:::shop-invoices/invoices/*"8 }9 ]10}1/3Version is fixed text. Statement holds one or more rules.
"2012-10-17" is the current AWS policy language version, not a typo. This role can read and write invoices and do nothing else.
Save yourself the pain
Common mistakes
Oops
Attaching AdministratorAccess to a CI user because the deploy kept failing with AccessDenied.
Do this instead
Read the error, add the single missing action, and retry. The error message usually names exactly what's needed.
Oops
Using the root account for everyday work.
Do this instead
Lock root away with MFA. Create named users or SSO logins, and give admin rights only to the few who truly need them.
Your mission
Write and test a tiny policy
Quick check
A policy allows s3:GetObject on one bucket. The app calls s3:DeleteObject on it. What happens?
Go deeper
- 1Audit a hypothetical IAM policy and identify any overly broad permissions.
- 2Practice writing a least-privilege IAM policy scoped to a specific task.
- 3Learn why 'admin access for everyone' is a common but serious security anti-pattern.
More topics at this stop
 DevSecOps Principles ('Shift Left')
 Secrets Management (Vault, AWS Secrets Manager)
 Container & Image Scanning
 Network Security Basics
 Compliance Basics (SOC 2, ISO 27001 Overview)
 Vulnerability Scanning in CI/CD
 Security Incident Response
 Zero Trust Architecture (Overview)

Stuck on this topic? Ask an Insider
Get 1:1 guidance from people who've walked this exact path — on the InsideEdge app.
